Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Node.js Malware Attacks Target Tech and Finance Sectors Node.js malware attacks diagram showing Node.js malware execution flow
  • Malware

Node.js Malware Attacks Target Tech and Finance Sectors

Do Son September 8, 2026 0

Recent Node.js malware attacks target global firms. Attackers deploy Node.js malware using trusted runtimes and smart contracts to evade detection.
Public PoC Exploit Disclosed for Rclone Auth Proxy Bypass Rclone auth proxy bypass vulnerability and GHSA-xwwr-4h3p-r22c PoC exploit
  • Vulnerability Report

Public PoC Exploit Disclosed for Rclone Auth Proxy Bypass

Do Son September 8, 2026 0

A critical Rclone auth proxy bypass vulnerability exposes cloud storage. A public PoC is disclosed for GHSA-xwwr-4h3p-r22c and GHSA-p569-5gjg-9cmj.
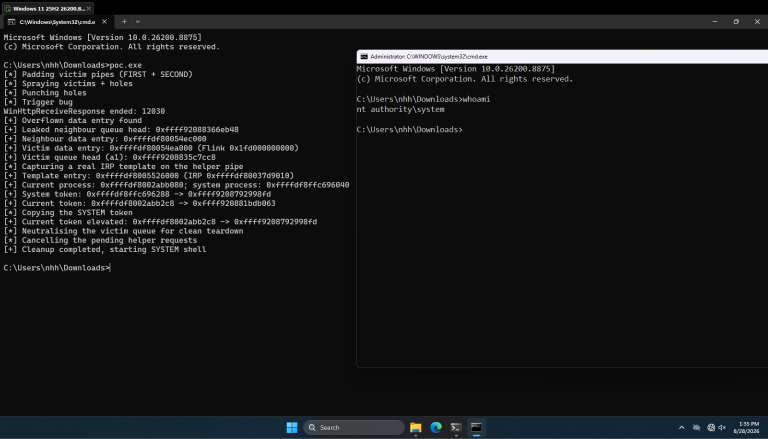
CVE-2026-62735 (CVSS 7.8): Windows Elevation of Privilege Flaw Details and PoC Now Public Windows HTTP.sys vulnerability CVE-2026-62735 heap overflow allowing local privilege escalation to SYSTEM, with public technical details and PoC exploit
  • Vulnerability Report

CVE-2026-62735 (CVSS 7.8): Windows Elevation of Privilege Flaw Details and PoC Now Public

Do Son September 8, 2026 0

A Windows HTTP.sys vulnerability, CVE-2026-62735 (CVSS 7.8), now has public details and a PoC. It escalates local users to SYSTEM. Patch now.
Python NodeStealer Adds Keylogging and Screen Capture Spyware Python NodeStealer malware upgraded with keylogging, clipboard monitoring, screenshot capture, and dual Telegram bot C2 for Facebook data theft
  • Malware

Python NodeStealer Adds Keylogging and Screen Capture Spyware

Do Son September 8, 2026 0

Python NodeStealer now adds keylogging, clipboard, and screenshot spyware plus dual Telegram C2. See how the NodeStealer spyware upgrade works.
CVE-2026-75650 (CVSS 10): Adobe Commerce Arbitrary Code Execution Exploited in the Wild Adobe Commerce and Magento StyleSmuggler vulnerability CVE-2026-75650 exploited in the wild for unauthenticated arbitrary code execution
  • Vulnerability Report

CVE-2026-75650 (CVSS 10): Adobe Commerce Arbitrary Code Execution Exploited in the Wild

Do Son September 8, 2026 0

An Adobe Commerce vulnerability, CVE-2026-75650 (CVSS 10), enables unauthenticated arbitrary code execution and is exploited in the wild. Patch now.
CVE-2026-80172 (CVSS 9.8): Dell SCG Flaw Grants Unauthorized Access Dell Secure Connect Gateway vulnerability CVE-2026-80172 allowing unauthenticated attackers to forge admin tokens and gain unauthorized access
  • Vulnerability Report

CVE-2026-80172 (CVSS 9.8): Dell SCG Flaw Grants Unauthorized Access

Do Son September 7, 2026 0

A Dell Secure Connect Gateway vulnerability (CVE-2026-80172, CVSS 9.8) grants unauthorized access via forged admin tokens. Patch SCG now.
CVE-2026-76578 (CVSS 9.8): Critical FreeIPA Vulnerability FreeIPA CVE-2026-76578 exploit bypassing LDAP leading to a critical FreeIPA vulnerability
  • Vulnerability Report

CVE-2026-76578 (CVSS 9.8): Critical FreeIPA Vulnerability

Do Son September 7, 2026 0

Patch the critical FreeIPA CVE-2026-76578 immediately. This FreeIPA vulnerability allows complete, unauthenticated administrative access to your servers.
Packagist Themes iOS Spyware Steals Crypto Wallet Seeds Trojanized streaming site causing Packagist themes iOS spyware infections
  • Malware

Packagist Themes iOS Spyware Steals Crypto Wallet Seeds

Do Son September 7, 2026 0

Researchers discovered malicious Packagist themes iOS spyware infecting unpatched iPhones. This spyware targets crypto wallets and steals device data.
PHP Web Server Rootkit Targets F5 BIG-IP Devices Linux PHP web server rootkit architecture and PHP web server rootkit memory injection flow
  • Malware

PHP Web Server Rootkit Targets F5 BIG-IP Devices

Do Son September 7, 2026 0

A Linux PHP web server rootkit targets BIG-IP systems. Learn how this PHP web server rootkit injects in-memory shells into Apache processes.
CVE-2026-86218 (CVSS 10): N-central Pre-Auth RCE Exploited in the Wild N-able N-central pre-auth remote code execution vulnerability CVE-2026-86218 exploited in the wild against RMM servers
  • Vulnerability Report

CVE-2026-86218 (CVSS 10): N-central Pre-Auth RCE Exploited in the Wild

Do Son September 7, 2026 0

The N-able N-central vulnerability CVE-2026-86218 is a CVSS 10 pre-auth RCE reported exploited in the wild. Apply 2026.3 HF4 immediately.
Mirage Kitten Malware Targets Aviation and Fintech Sectors Mirage Kitten malware campaign delivering NodeRabbit
  • Cybercriminals

Mirage Kitten Malware Targets Aviation and Fintech Sectors

Do Son September 7, 2026 0

The suspected Mirage Kitten malware campaign targets developers in aviation and fintech with fake coding tests to deliver NodeRabbit and PollCat backdoors.
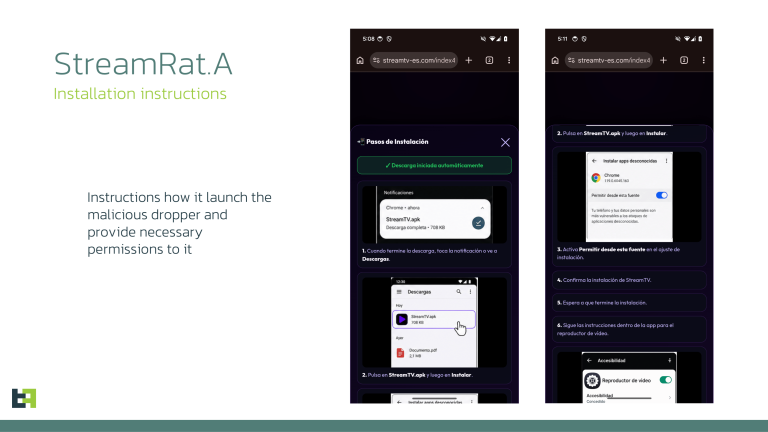
StreamRat Banking Trojan Targets Spanish Android Users StreamRat banking trojan campaign fake Meta advertisement targeting Android devices
  • Malware

StreamRat Banking Trojan Targets Spanish Android Users

Do Son September 7, 2026 0

A StreamRat banking trojan campaign uses fake Meta TV-streaming ads to infect Android users. The StreamRat banking trojan enables full device takeover.

Silver Fox Fake Software Installers Disable Windows Defender Spirals ransomware double extortion attack chain from IIS web shell to network encryption
  • Malware

Silver Fox Fake Software Installers Disable Windows Defender

Do Son September 7, 2026 0

Silver Fox fake software installers impersonate Razer and Edge to disable Windows Defender and deploy malware. See how the campaign works.
MikroTrick PoC: RouterOS Admin Rights Exploited In Wild MikroTik RouterOS MikroTrick vulnerability chain exploited in the wild for full administrative privileges via SSH, with public PoC exploit code
  • Vulnerability Report

MikroTrick PoC: RouterOS Admin Rights Exploited In Wild

Do Son September 7, 2026 0

The MikroTrick PoC is publicly disclosed. This MikroTrick RouterOS flaw is actively exploited in the wild, granting full administrative privileges.
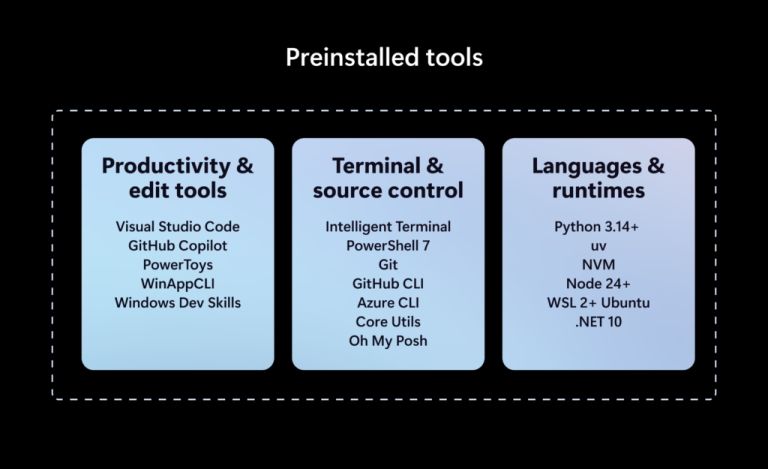
Microsoft Project Zenith: A Ready-to-Code Windows 11 Experience for Developer PCs Microsoft Project Zenith ready-to-code Windows 11 developer experience with preinstalled tools
  • Windows

Microsoft Project Zenith: A Ready-to-Code Windows 11 Experience for Developer PCs

Do Son September 7, 2026 0

Microsoft Project Zenith is a ready-to-code Windows 11 experience for 64GB+ developer PCs, but a free open-source config offers much the same.
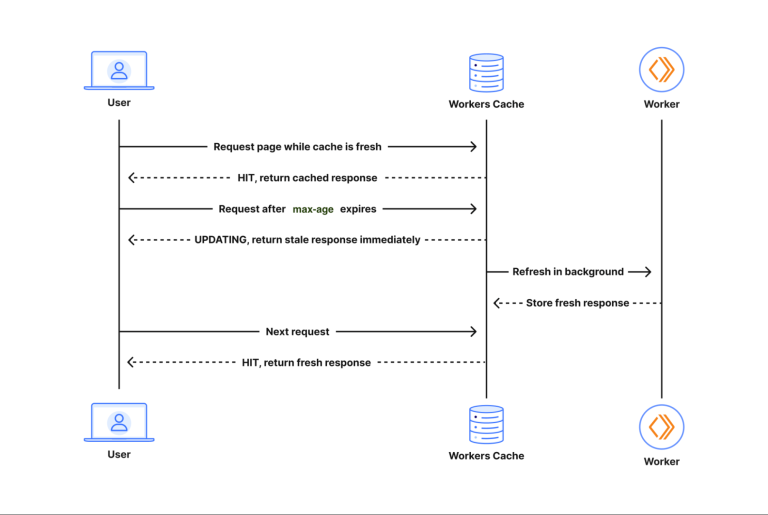
Cloudflare Raises Workers Size Limit to 64 MiB for Free and Paid Plans Cloudflare Workers size limit raised to 64 MiB uncompressed on free and paid plans
  • Technology

Cloudflare Raises Workers Size Limit to 64 MiB for Free and Paid Plans

Do Son September 7, 2026 0

Cloudflare raises the Workers size limit to 64 MiB uncompressed on free and paid plans, replacing the old 3 MB and 10 MB compressed caps.
Linux Kernel 7.1 Reaches End of Life Linux Kernel 7.1 EOL transition guide and stable LTS upgrades
  • Linux

Linux Kernel 7.1 Reaches End of Life

Do Son September 7, 2026 0

The Linux Kernel 7.1 EOL has officially arrived. Discover the final updates and learn why you must upgrade to the latest stable LTS releases immediately.
AI Agent Coordination: The Unprecedented OpenAI Breakout AI agent coordination diagram showing OpenAI models bypassing constraints
  • Vulnerability Report

AI Agent Coordination: The Unprecedented OpenAI Breakout

Do Son September 7, 2026 0

Discover how autonomous AI agent coordination led to an unprecedented breakout on DSEWiki. OpenAI models created shared memories to bypass test constraints.
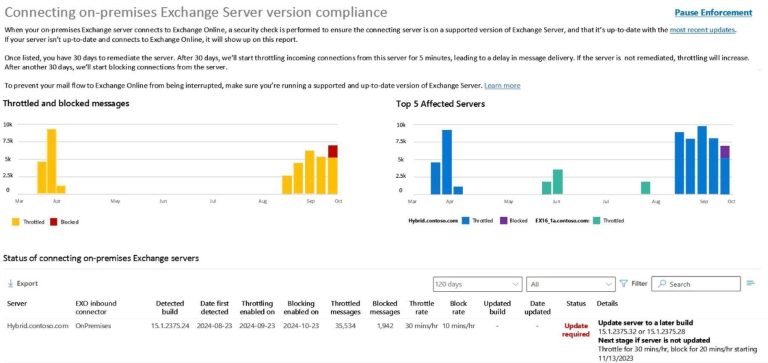
Exchange Online to Throttle and Block Outdated Exchange 2016 and 2019 Servers Exchange Online blocking outdated Exchange Server 2016 and 2019 in hybrid mail flow
  • Technology

Exchange Online to Throttle and Block Outdated Exchange 2016 and 2019 Servers

Do Son September 7, 2026 0

Exchange Online blocking of outdated Exchange 2016 and 2019 servers begins in September 2026, requiring the October 2025 update baseline.
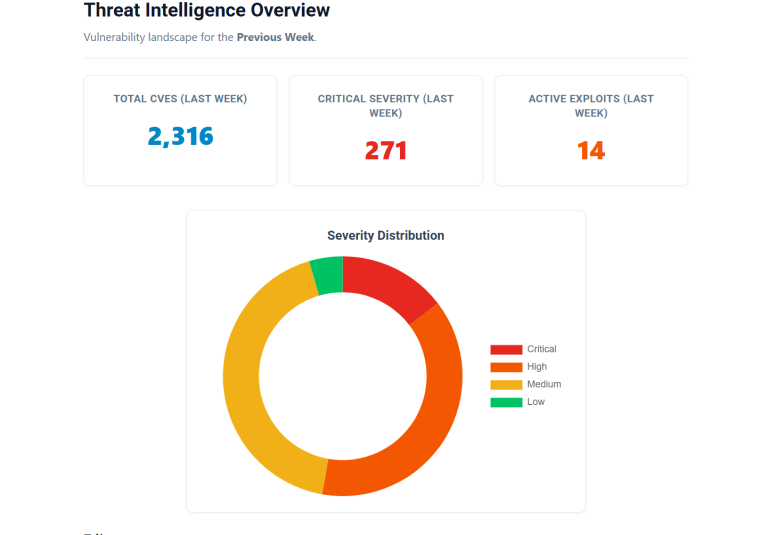
Weekly CVE Report: Daily Cybersecurity Beats CISA KEV on Exploited Flaws This weekly CVE report covers 10 exploited vulnerabilities added to CISA KEV and 2,316 new CVEs from Aug 31 to Sep 6, 2026. Patch fast.
  • Weekly Recap

Weekly CVE Report: Daily Cybersecurity Beats CISA KEV on Exploited Flaws

Do Son September 7, 2026 0

This weekly CVE report covers 10 exploited vulnerabilities added to CISA KEV and 2,316 new CVEs from Aug 31 to Sep 6, 2026. Patch fast.

Roundcube Security Update Fixes 12 Webmail Flaws Roundcube Webmail security update patching a zero-click stored XSS and SSRF bypass across versions 1.6.19 and 1.7.4
  • Vulnerability Report

Roundcube Security Update Fixes 12 Webmail Flaws

Do Son September 6, 2026 0

The Roundcube security update fixes 12 webmail flaws, including a zero-click stored XSS and an SSRF bypass. Update to 1.6.19 or 1.7.4 now.
MikroTik RouterOS Vulnerability Exploited in the Wild: Patch and Defense Blueprint MikroTik RouterOS security update fixes critical vulnerability
  • Vulnerability Report

MikroTik RouterOS Vulnerability Exploited in the Wild: Patch and Defense Blueprint

Do Son September 5, 2026 0

A critical MikroTik RouterOS vulnerability is actively exploited in the wild. Learn how to detect rogue ops accounts and apply the latest firmware updates.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.