Skip to content
November 11, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Telekopye Expands to Target Tourists via Hotel Booking Scam Telekopye scam toolkit
  • Cyber Security

Telekopye Expands to Target Tourists via Hotel Booking Scam

Do Son October 10, 2024 0

Discover the evolution of the Telekopye scam toolkit: from targeting online marketplace users to exploiting tourists via accommodation booking platforms.

The Future of Cloud Security: Automation Strategies and Techniques Cloud Security
  • Technique

The Future of Cloud Security: Automation Strategies and Techniques

Do Son October 10, 2024 0

Stay ahead of the game with cloud security automation. Explore the benefits of using automation tools to detect and respond to threats in real time.

CVE-2024-9466 Flaw in Palo Alto Networks’ Expedition Exposes Sensitive Credentials to Attackers, PoC Published CVE-2024-9466
  • Vulnerability

CVE-2024-9466 Flaw in Palo Alto Networks’ Expedition Exposes Sensitive Credentials to Attackers, PoC Published

Do Son October 10, 2024 0

Critical vulnerability in Palo Alto Networks' Expedition tool (CVE-2024-9466) could expose sensitive credentials to authenticated attackers.

CVE-2024-47223 (CVSS 9.4): SQLi Flaw in Mitel MiCollab Poses Severe Risk to Enterprises Mitel MiCollab SQL Injection MiCollab software - CVE-2024-47223 & CVE-2024-41713
  • Vulnerability

CVE-2024-47223 (CVSS 9.4): SQLi Flaw in Mitel MiCollab Poses Severe Risk to Enterprises

Do Son October 10, 2024 0

Mitel warns of high-severity SQL injection vulnerability (CVE-2024-47223) in MiCollab software. Find out about the potential impacts it could have on system security and corporate collaboration.

Internet Archive Under Siege: DDoS Attacks and a Mysterious Data Breach Internet Archive Data Breach
  • Cyber Security
  • Data Leak

Internet Archive Under Siege: DDoS Attacks and a Mysterious Data Breach

Do Son October 9, 2024 0

Discover the shocking details of the Internet Archive data breach: 31 million user records compromised and dumped online.

CVE-2024-9164 (CVSS 9.6): GitLab Users Urged to Update Now CVE-2024-9164 - CVE-2025-0376 GitLab Wiki XSS, Session Hijack Flaw
  • Vulnerability

CVE-2024-9164 (CVSS 9.6): GitLab Users Urged to Update Now

Do Son October 9, 2024 0

Stay secure with GitLab's latest security updates. Learn about crucial patches that address flaws, including the critical CVE-2024-9164.
Researcher Details Privilege Escalation in Palo Alto Networks’ GlobalProtect MSI Installer (CVE-2024-9473) CVE-2024-9473
  • Vulnerability

Researcher Details Privilege Escalation in Palo Alto Networks’ GlobalProtect MSI Installer (CVE-2024-9473)

Do Son October 9, 2024 0

Learn about the recently discovered local privilege escalation vulnerability (CVE-2024-9473) affecting Palo Alto Networks' GlobalProtect software.

OpenBAS: A Powerful Open-Source Platform for Cyber Adversary Simulations Cyber Adversary Simulations
  • Open Source Tool

OpenBAS: A Powerful Open-Source Platform for Cyber Adversary Simulations

Do Son October 9, 2024 0

OpenBAS is an open-source platform aimed at providing organizations with the ability to plan and execute detailed cyber adversary simulations

CVE-2024-45720: Code Execution Flaw Discovered in Apache Subversion for Windows Apache Subversion - CVE-2024-45720
  • Vulnerability

CVE-2024-45720: Code Execution Flaw Discovered in Apache Subversion for Windows

Do Son October 9, 2024 0

Learn about CVE-2024-45720, a security flaw in Apache Subversion (SVN), and its potential ramifications for developers on Windows platforms.

North Korean Threat Actors Targeting Tech Job Seekers with Contagious Interview Campaign Contagious Interview
  • Cyber Security

North Korean Threat Actors Targeting Tech Job Seekers with Contagious Interview Campaign

Do Son October 9, 2024 0

Beware of the Contagious Interview campaign: North Korean threat actors posing as recruiters target tech job seekers with malware.

Researcher Details Arbitrary File Read Vulnerability (CVE-2024-36814) in AdGuard Home Screenshot 2024-10-09 150347
  • Vulnerability

Researcher Details Arbitrary File Read Vulnerability (CVE-2024-36814) in AdGuard Home

Do Son October 9, 2024 0

Stay informed about the latest vulnerability in AdGuard Home. Discover how attackers can exploit CVE-2024-36814 to access sensitive files on your system.

CVE-2024-8884 (CVSS 9.8): Critical Flaw Exposes Schneider Electric Industrial PCs to Attack CVE-2024-8884 & CVE-2024-11737 Schneider Electric, Critical Vulnerabilities
  • Vulnerability

CVE-2024-8884 (CVSS 9.8): Critical Flaw Exposes Schneider Electric Industrial PCs to Attack

Do Son October 9, 2024 0

Schneider Electric warns of critical security vulnerability (CVE-2024-8884) in Harmony Industrial PC Series and Pro-face PS5000 Legacy Industrial PC Series.

Exploiting Livewire: CVE-2024-47823 Puts Laravel Apps at Risk Livewire - CVE-2024-47823
  • Vulnerability

Exploiting Livewire: CVE-2024-47823 Puts Laravel Apps at Risk

Do Son October 9, 2024 0

Learn about CVE-2024-47823, a critical vulnerability in Livewire framework for Laravel, allowing remote code execution via file uploads.

Dark Angels Ransomware Group: The Shadowy Threat Behind the Record $75M Ransom Rhysida Ransomware
  • Malware

Dark Angels Ransomware Group: The Shadowy Threat Behind the Record $75M Ransom

Do Son October 9, 2024 0

Discover the Dark Angels Ransomware Group, a highly sophisticated and stealthy threat targeting large enterprises with targeted attacks.

Palo Alto Networks Issues Fix for Critical Vulnerabilities, Including CVE-2024-9463 (CVSS 9.9) CVE-2024-9463
  • Vulnerability

Palo Alto Networks Issues Fix for Critical Vulnerabilities, Including CVE-2024-9463 (CVSS 9.9)

Do Son October 9, 2024 0

Learn about the critical flaw affecting Palo Alto Networks Expedition migration tool (CVE-2024-9463 & CVE-2024-9465) and the potential risks to firewall admin accounts and sensitive information.
CISA Adds Three Actively Exploited Security Vulnerabilities to KEV Catalog, Urges Urgent Patching State-Sponsored Exploitation CISA KEV Catalog F5 BIG-IP RCE CISA KEV Catalog SolarWinds WHD Exploit CVE-2025-40551 Zimbra XSS Zero-Day CVE-2025-27915 Exploited Windows Security Vulnerabilities
  • Vulnerability

CISA Adds Three Actively Exploited Security Vulnerabilities to KEV Catalog, Urges Urgent Patching

Do Son October 9, 2024 0

Get the latest updates on exploited security vulnerabilities. Find out how to protect your systems from the newly added threats.

Firefox Zero-Day Vulnerability: Urgent Update Needed to Patch CVE-2024-9680 CVE-2024-9680
  • Vulnerability

Firefox Zero-Day Vulnerability: Urgent Update Needed to Patch CVE-2024-9680

Do Son October 9, 2024 0

Get up-to-date information on the zero-day vulnerability (CVE-2024-9680) in Firefox, its potential impact, and steps to mitigate the risk.
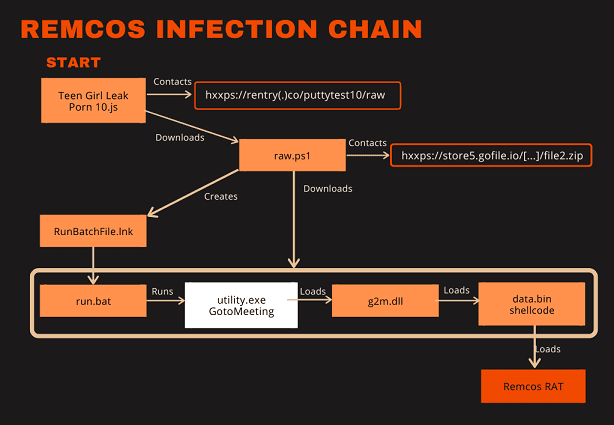
Tax Extension Malware Campaign Exploits Trusted GitHub Repositories to Deliver Remcos RAT GDATA_GotoMeeting_Remcos_JS_infection_chain
  • Malware

Tax Extension Malware Campaign Exploits Trusted GitHub Repositories to Deliver Remcos RAT

Do Son October 9, 2024 0

Beware of a new tax extension malware campaign exploiting GitHub links. Find out how threat actors are bypassing security defenses and distributing the Remcos RAT.

Ukrainian National Pleads Guilty to Operating Raccoon Infostealer Malware-as-a-Service Raccoon Infostealer
  • Cyber Security

Ukrainian National Pleads Guilty to Operating Raccoon Infostealer Malware-as-a-Service

Do Son October 9, 2024 0

Explore the dark world of the Raccoon Infostealer and its impact on cybersecurity and personal data protection.

JAXA Cyberattack: Hackers Breach Accounts of Top Officials, Exposing Sensitive Space and Defense Data JAXA cyberattacks
  • Cyber Security

JAXA Cyberattack: Hackers Breach Accounts of Top Officials, Exposing Sensitive Space and Defense Data

Do Son October 9, 2024 0

Uncover the cyberattacks on JAXA. Find out how sophisticated attacks compromised accounts and exposed sensitive information.

Russia Bans Discord Over Illegal Content Concerns Russia ban Discord
  • Technology

Russia Bans Discord Over Illegal Content Concerns

Do Son October 8, 2024 0

Russia enforces ban on Discord amidst ongoing dispute. Learn more about the reasons behind the block and its implications for users.

Casio Confirms Network Breach, Investigates Potential Data Compromise Casio Network Breach - data leak
  • Cyber Security

Casio Confirms Network Breach, Investigates Potential Data Compromise

Do Son October 8, 2024 0

Casio faces cybersecurity incident. Unauthorized access to the network causes disruptions and potential compromise of personal data.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-126259CVSS 9.0
    Missing authentication for critical function in FortiOS
    📅 Updated: Nov 10, 2026
  • CVE-2026-126262CVSS 9.3
    Improper neutralization of special elements used in an SQL command in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126260CVSS 9.0
    Server side request forgery vulnerability in FortiAnalyzer, FortiManager with FortiAnalyzer features & FortiAnalyzer-BigData
    📅 Updated: Nov 10, 2026
  • CVE-2026-126170CVSS 9.8
    Unauthenticated RCE in multiple products
    📅 Updated: Nov 10, 2026
  • CVE-2026-126261CVSS 9.0
    Improper authorizatin vulnerability in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126187CVSS 9.5
    React is a JavaScript library for building user interfaces. From 19.0.0 until 19.0.9, 19.1.10, 19.2.9, and 19.3.1, the...
    📅 Updated: Nov 10, 2026
  • CVE-2026-126229CVSS 9.1
    Authorization Bypass in FortiManager, FortiAnalyzer, FortiManager Cloud and FortiAnalyzer Cloud
    📅 Updated: Nov 10, 2026
  • CVE-2026-126253CVSS 9.3
    OSPF Authentication Bypass in multiple product
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.