Skip to content
November 11, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Microsoft Warns of Sophisticated Identity Phishing Campaigns Misusing File Hosting Services File hosting services
  • Cyber Security

Microsoft Warns of Sophisticated Identity Phishing Campaigns Misusing File Hosting Services

Do Son October 8, 2024 0

Beware of phishing campaigns using file hosting services as a launching pad for business email compromise attacks. Stay informed and secure.

Google Pays $55,000 Bounty for Chrome Security Flaw CVE-2024-9602 & CVE-2024-9603
  • Vulnerability

Google Pays $55,000 Bounty for Chrome Security Flaw

Do Son October 8, 2024 0

Stay protected with the latest Chrome update. Learn about the important security fixes, including the patching of critical vulnerabilities CVE-2024-9602.

Critical Vulnerabilities Discovered in Siemens SINEC Security Monitor Siemens RTLS, CVE-2025-40746 CVE-2024-22040 - SINEC Security Monitor Siemens Security Advisory SENTRON 7KT PAC1260
  • Vulnerability

Critical Vulnerabilities Discovered in Siemens SINEC Security Monitor

Do Son October 8, 2024 0

Critical security update for Siemens' SINEC Security Monitor. Discover how to address vulnerabilities and ensure the safety of your industrial systems.
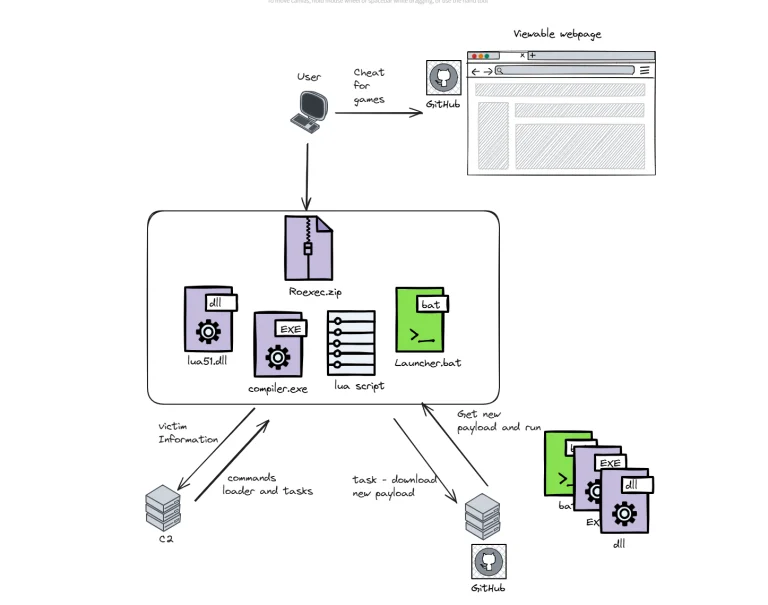
Global Malware Campaign Exploits Lua in Gaming and Education Sectors Lua Malware
  • Malware

Global Malware Campaign Exploits Lua in Gaming and Education Sectors

Do Son October 8, 2024 0

Stay informed about the latest wave of Lua malware attacks targeting the educational sector and gaming communities.

Microsoft’s October 2024 Patch Tuesday: Zero-Day Exploits and Critical Vulnerabilities Patched Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability

Microsoft’s October 2024 Patch Tuesday: Zero-Day Exploits and Critical Vulnerabilities Patched

Do Son October 8, 2024 0

Microsoft Patches 121 Vulnerabilities in October 2024: Two Zero-Day Exploits Under Active Attack: CVE-2024-43573 and CVE-2024-43572

Pronsis Loader: The Emerging Threat Behind JPHP-Driven Malware Caminho LSB Steganography, Loader-as-a-Service 2023 Threat Report
  • Cyber Security
  • Malware

Pronsis Loader: The Emerging Threat Behind JPHP-Driven Malware

Do Son October 8, 2024 0

Discover Pronsis Loader: A Java implementation of PHP malware that poses a significant risk. Learn about its similarities to D3F@ck Loader.

GoldenJackal Bypasses Air-Gaps in Sophisticated Espionage Campaigns GoldenJackal
  • Cyber Security
  • Malware

GoldenJackal Bypasses Air-Gaps in Sophisticated Espionage Campaigns

Do Son October 8, 2024 0

Uncover the cyberespionage campaigns of GoldenJackal, an elusive APT group targeting governmental entities across Europe, the Middle East, and South Asia.

Yunit Stealer: How This Advanced Malware Evades Detection While Stealing Your Information Yunit Stealer
  • Malware

Yunit Stealer: How This Advanced Malware Evades Detection While Stealing Your Information

Do Son October 8, 2024 0

Stay informed about the latest cybersecurity threat, the Yunit Stealer. Learn how this advanced malware extracts sensitive data while evading detection.

New Campaign by Awaken Likho APT Group: Changes in Software and Techniques Oracle EBS Zero-Day, GRACEFUL SPIDER Cracked Software, Supply Chain Attack Black Basta - NOVA stealer
  • Cyber Security

New Campaign by Awaken Likho APT Group: Changes in Software and Techniques

Do Son October 8, 2024 0

Get insights into the advanced techniques of the Awaken Likho APT group as they exploit the MeshCentral platform in their targeted attacks.

CVE-2024-37404: Critical RCE Flaw Discovered in Ivanti Connect Secure & Policy Secure, PoC Published CVE-2024-37404
  • Vulnerability

CVE-2024-37404: Critical RCE Flaw Discovered in Ivanti Connect Secure & Policy Secure, PoC Published

Do Son October 8, 2024 0

Stay secure with Ivanti Connect Secure and Policy Secure. Find out about the critical RCE vulnerability CVE-2024-37404 and learn how to protect your systems.

Ivanti Patches CSA Appliance Against Vulnerabilities, Including Actively Exploited Flaws Ivanti EPMM Zero-Day CVE-2026-6973 Exploitation CVE-2024-9379, CVE-2024-9380, CVE-2024-9381
  • Vulnerability

Ivanti Patches CSA Appliance Against Vulnerabilities, Including Actively Exploited Flaws

Do Son October 8, 2024 0

This exploitation involves chaining CVE-2024-9379, CVE-2024-9380, or CVE-2024-9381 with a previously addressed vulnerability

Hidden Cryptocurrency Mining Campaign Hits Over 28,000 Users, Stealing Thousands in Crypto Cryptocurrency Mining Campaign
  • Malware

Hidden Cryptocurrency Mining Campaign Hits Over 28,000 Users, Stealing Thousands in Crypto

Do Son October 8, 2024 0

Unveiling a widespread malware campaign: how attackers disguise cryptomining and cryptostealing malware as legitimate software.

CVE-2024-41798 (CVSS 9.8): Siemens SENTRON PAC3200 Meters Vulnerable to Easy Attacks, No Patch! Siemens SIVaaS CVE-2025-40804 CVE-2022-43400 & CVE-2024-41798 Siemens SINEC NMS, Critical Vulnerabilities
  • Vulnerability

CVE-2024-41798 (CVSS 9.8): Siemens SENTRON PAC3200 Meters Vulnerable to Easy Attacks, No Patch!

Do Son October 8, 2024 0

Learn about the security flaw (CVE-2024-41798) in Siemens SENTRON PAC3200 meters, allowing attackers to compromise sensitive energy management data.

SAP Patches Critical BusinessObjects Vulnerability with October Security Updates
  • Vulnerability

SAP Patches Critical BusinessObjects Vulnerability with October Security Updates

Do Son October 8, 2024 0

SAP's October Security Patch Day: Protect your business from critical vulnerabilities. Stay informed about the latest security updates.

MoneyGram Notifies Consumers of Data Breach Affecting Sensitive Personal Information MoneyGram data breach
  • Data Leak

MoneyGram Notifies Consumers of Data Breach Affecting Sensitive Personal Information

Do Son October 8, 2024 0

MoneyGram data breach: unauthorized access to sensitive customer information prompts swift action for consumer protection.
PoC Exploit Releases for CVE-2023-52447: A Linux Kernel Flaw Enabling Container Escape Linux Kernel 2025 Year in Review, Rust for Linux graduation Linux Security, Core Dump CVE-2023-52447 PoC Exploit
  • Vulnerability

PoC Exploit Releases for CVE-2023-52447: A Linux Kernel Flaw Enabling Container Escape

Do Son October 7, 2024 0

Researchers have published technical details and a (PoC) exploit for a vulnerability in the Linux kernel, designated as CVE-2023-52447
Critical Zero-Day Automotive Systems Vulnerabilities Exposed Automotive Systems Vulnerabilities
  • Vulnerability

Critical Zero-Day Automotive Systems Vulnerabilities Exposed

Do Son October 7, 2024 0

Stay informed about the safety of modern vehicles. Discover the critical vulnerabilities in automotive systems and the potential consequences.

Exploit Releases for TeamViewer Flaws (CVE-2024-7479 & CVE-2024-7481) Let Unprivileged Users Load Arbitrary Kernel Drivers CVE-2024-7481 exploit
  • Vulnerability

Exploit Releases for TeamViewer Flaws (CVE-2024-7479 & CVE-2024-7481) Let Unprivileged Users Load Arbitrary Kernel Drivers

Do Son October 7, 2024 0

Gabaldon published the PoC exploit on GitHub, allowing researchers & security professionals to better understand and test CVE-2024-7479 & CVE-2024-7481
Chinese Threat Groups Leverage Ransomware for Political Gain Chinese Threat Groups
  • Cyber Security

Chinese Threat Groups Leverage Ransomware for Political Gain

Do Son October 7, 2024 0

Explore the evolving landscape of ransomware deployment by Chinese threat groups. Discover the motivations and tactics behind these attacks in this comprehensive report.

New Anti-Theft Arsenal: Android Gets Theft Detection, Offline, and Remote Lock Theft Detection Lock, Offline Device Lock, and Remote Lock
  • Technology

New Anti-Theft Arsenal: Android Gets Theft Detection, Offline, and Remote Lock

Do Son October 7, 2024 0

Enhance the security of your Android phone with powerful anti-theft features like Theft Detection Lock, Offline Device Lock, and Remote Lock.

Your Smart TV is Watching You: New Research Reveals the Extent of ACR Tracking Automatic Content Recognition
  • Data Leak

Your Smart TV is Watching You: New Research Reveals the Extent of ACR Tracking

Do Son October 7, 2024 0

Discover how smart TVs use Automatic Content Recognition (ACR) technology to track viewing habits and collect data for targeted advertising.

Researcher Releases Open-Source Scanner for CVE-2024-47176 CUPS Vulnerability CVE-2024-47176 Vulnerability Scanner
  • Open Source Tool
  • Vulnerability

Researcher Releases Open-Source Scanner for CVE-2024-47176 CUPS Vulnerability

Do Son October 7, 2024 0

Learn about the critical vulnerabilities in CUPS and how Marcus Hutchins' open-source tool can help you detect and mitigate the CVE-2024-47176 vulnerability.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-126259CVSS 9.0
    Missing authentication for critical function in FortiOS
    📅 Updated: Nov 10, 2026
  • CVE-2026-126262CVSS 9.3
    Improper neutralization of special elements used in an SQL command in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126260CVSS 9.0
    Server side request forgery vulnerability in FortiAnalyzer, FortiManager with FortiAnalyzer features & FortiAnalyzer-BigData
    📅 Updated: Nov 10, 2026
  • CVE-2026-126170CVSS 9.8
    Unauthenticated RCE in multiple products
    📅 Updated: Nov 10, 2026
  • CVE-2026-126261CVSS 9.0
    Improper authorizatin vulnerability in FortiManager
    📅 Updated: Nov 10, 2026
  • CVE-2026-126187CVSS 9.5
    React is a JavaScript library for building user interfaces. From 19.0.0 until 19.0.9, 19.1.10, 19.2.9, and 19.3.1, the...
    📅 Updated: Nov 10, 2026
  • CVE-2026-126229CVSS 9.1
    Authorization Bypass in FortiManager, FortiAnalyzer, FortiManager Cloud and FortiAnalyzer Cloud
    📅 Updated: Nov 10, 2026
  • CVE-2026-126253CVSS 9.3
    OSPF Authentication Bypass in multiple product
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.