Skip to content
November 11, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Sophisticated Okta SSO Phishing Bypasses Defenses to Steal Session Tokens With Salary Review Lures UAT-8099 BadIIS Malware Pacific Islands Forum Cyberattack
  • Cybercriminals

Sophisticated Okta SSO Phishing Bypasses Defenses to Steal Session Tokens With Salary Review Lures

Do Son December 12, 2025 0
Just as employees begin anticipating their year-end performance reviews, a sophisticated new phishing campaign has emerged, turning...
Read More Read more about Sophisticated Okta SSO Phishing Bypasses Defenses to Steal Session Tokens With Salary Review Lures
CVE-2025-64188 (CVSS 9.8): Critical “Soledad” Theme Flaw Lets Subscribers Take Over WordPress Sites CVE-2023-3460 WordPress Theme Critical Flaw
  • Vulnerability Report

CVE-2025-64188 (CVSS 9.8): Critical “Soledad” Theme Flaw Lets Subscribers Take Over WordPress Sites

Do Son December 12, 2025 0
A critical security vulnerability has been discovered in Soledad, one of the most popular general-purpose WordPress themes...
Read More Read more about CVE-2025-64188 (CVSS 9.8): Critical “Soledad” Theme Flaw Lets Subscribers Take Over WordPress Sites
DiCaprio Movie Torrent Lures Users: Agent Tesla Deployed via Malicious LNK and Subtitle File Code Hiding Agent Tesla Movie Lure, Subtitle File Infection
  • Malware

DiCaprio Movie Torrent Lures Users: Agent Tesla Deployed via Malicious LNK and Subtitle File Code Hiding

Do Son December 12, 2025 0
Cybersecurity researchers have uncovered a new, sophisticated malware campaign targeting movie pirates with a lure they can’t...
Read More Read more about DiCaprio Movie Torrent Lures Users: Agent Tesla Deployed via Malicious LNK and Subtitle File Code Hiding
GOLD BLADE APT Hits Canadian Firms with BYOVD EDR Killer and Ransomware Delivered Via Fake Resumes GOLD BLADE Canada, BYOVD EDR Killer
  • Malware

GOLD BLADE APT Hits Canadian Firms with BYOVD EDR Killer and Ransomware Delivered Via Fake Resumes

Do Son December 12, 2025 0
A notorious threat group has pivoted its focus to the Great White North, unleashing a sophisticated campaign...
Read More Read more about GOLD BLADE APT Hits Canadian Firms with BYOVD EDR Killer and Ransomware Delivered Via Fake Resumes
1inch Named Exclusive Swap Provider at Launch for Ledger Multisig 1inch_ase_study_Ledger_1765444649YfKehgLWGE
  • Press Release

1inch Named Exclusive Swap Provider at Launch for Ledger Multisig

cybernewswire December 11, 2025 0
Road Town, British Virgin Islands, 11th December 2025, CyberNewsWire
Read More Read more about 1inch Named Exclusive Swap Provider at Launch for Ledger Multisig
INE Highlights Enterprise Shift Toward Hands-On Training Amid Widening Skills Gaps Blog___December_2025___Enterprises_Tackle_Skills_G_1765308844mvXzfDKnPu
  • Press Release

INE Highlights Enterprise Shift Toward Hands-On Training Amid Widening Skills Gaps

cybernewswire December 11, 2025 0
Cary, North Carolina, USA, 11th December 2025, CyberNewsWire
Read More Read more about INE Highlights Enterprise Shift Toward Hands-On Training Amid Widening Skills Gaps
Urgent Patch: Notepad++ WinGUp Flaw Allowed Malware to Hijack Updates CVE-2023-40031 Notepad++ Update Hijacking, WinGUp Vulnerability
  • Vulnerability Report

Urgent Patch: Notepad++ WinGUp Flaw Allowed Malware to Hijack Updates

Do Son December 11, 2025 0
Security researchers recently uncovered a vulnerability in the open-source text and code editor Notepad++, allowing attackers in...
Read More Read more about Urgent Patch: Notepad++ WinGUp Flaw Allowed Malware to Hijack Updates
16-Year Battle Ends: Intel Loses Appeal, Must Pay €237 Million EU Fine Intel EU Antitrust Fine, Naked Restrictions Intel Layoff Data Theft Jinfeng Luo Intel leadership change Intel SoftBank Intel Foundry, Semiconductor Market Intel Arrow Lake Refresh, Copilot+ PC Intel GPU Performance, Security Mitigations Mitigation Downfall Vulnerability
  • Technology

16-Year Battle Ends: Intel Loses Appeal, Must Pay €237 Million EU Fine

Do Son December 11, 2025 0
In a case spanning sixteen years and regarded as one of the most protracted antitrust battles in...
Read More Read more about 16-Year Battle Ends: Intel Loses Appeal, Must Pay €237 Million EU Fine
Qualcomm Buys Ventana to Double Down on RISC-V and Custom Oryon CPU Qualcomm Samsung 2nm foundry deal, Snapdragon 8 Elite 2nm refresh Qualcomm Ventana Acquisition, RISC-V Strategy Qualcomm Autotalks, China Antitrust Qualcomm Antitrust, Which? Lawsuit Qualcomm GPU driver, CVE-2024-38399 Qualcomm's March 2025 Security Bulletin
  • Technology

Qualcomm Buys Ventana to Double Down on RISC-V and Custom Oryon CPU

Do Son December 11, 2025 0
To further consolidate its technological leadership in the computing domain, Qualcomm has announced its acquisition of Ventana...
Read More Read more about Qualcomm Buys Ventana to Double Down on RISC-V and Custom Oryon CPU
You’re In Control: Instagram Launches “Your Algorithm” Feature for Reels Instagram Your Algorithm, Reels Personalization
  • Technology

You’re In Control: Instagram Launches “Your Algorithm” Feature for Reels

Do Son December 11, 2025 0
Instagram has announced the launch of a new feature called “Your Algorithm,” marking the first time users...
Read More Read more about You’re In Control: Instagram Launches “Your Algorithm” Feature for Reels
❮ Prev Page
Next Page ❯
NGINX Open Source Makes the Jump to GitHub, Boosting Collaboration and Community Engagement NGINX JavaScript Module Vulnerability CVE-2026-8711 NGINX 1.30.1 Security Update CVE-2026-42945 RCE NGINX Vulnerability CVE-2026-1642 NGINX Github - CVE-2025-23419
  • Technology

NGINX Open Source Makes the Jump to GitHub, Boosting Collaboration and Community Engagement

Do Son September 10, 2024 0

Enhance collaboration and engagement with NGINX's migration of its open-source development repository to GitHub.

CISA Alerts on Active Exploitation of Flaws in ImageMagick, Linux Kernel, and SonicWall SonicWall vulnerability
  • Vulnerability

CISA Alerts on Active Exploitation of Flaws in ImageMagick, Linux Kernel, and SonicWall

Do Son September 9, 2024 0

Urgent warning from CISA: Actively exploited vulnerabilities in ImageMagick, Linux Kernel, and SonicWall. Learn how to safeguard against potential cyberattacks.
CVE-2024-6342: Critical Command Injection Flaw in Zyxel NAS Devices, Hotfixes Released for End-of-Support Products CVE-2024-6342 - Zyxel NAS542 & NAS326
  • Vulnerability

CVE-2024-6342: Critical Command Injection Flaw in Zyxel NAS Devices, Hotfixes Released for End-of-Support Products

Do Son September 9, 2024 0

Discover the critical command injection vulnerability (CVE-2024-6342) affecting Zyxel NAS326 and NAS542 and how to mitigate it.

CVE-2024-30051: Windows Elevation of Privilege Flaw Exploited by QakBot Malware, PoC Published CVE-2024-30051 exploit PoC
  • Vulnerability

CVE-2024-30051: Windows Elevation of Privilege Flaw Exploited by QakBot Malware, PoC Published

Do Son September 9, 2024 0

Discover the details of the CVE-2024-30051 vulnerability in Windows and the PoC exploit. Stay informed about this critical flaw and the potential risks it poses.

FreeBSD Issues Urgent Security Advisory for CVE-2024-43102 (CVSS 10)
  • Vulnerability

FreeBSD Issues Urgent Security Advisory for CVE-2024-43102 (CVSS 10)

Do Son September 9, 2024 0

Critical vulnerability (CVE-2024-43102) in FreeBSD: Learn about the flaw that could lead to a complete system compromise and how to mitigate it.

Chinese APT Groups Continue to Leverage Open-Source and Custom Reconnaissance Tools in Cyber Espionage Campaigns Open-Source
  • Cyber Security

Chinese APT Groups Continue to Leverage Open-Source and Custom Reconnaissance Tools in Cyber Espionage Campaigns

Do Son September 9, 2024 0

Explore the reconnaissance techniques used by Chinese APT groups like APT41 and APT10. Learn about the open-source and customized tools they rely on for cyber espionage.

ToneShell Backdoor Targets IISS Defence Summit Attendees in Latest Espionage Campaign ToneShell Backdoor
  • Cyber Security
  • Malware

ToneShell Backdoor Targets IISS Defence Summit Attendees in Latest Espionage Campaign

Do Son September 9, 2024 0

Uncover the cyber espionage tactics of the Mustang Panda group and their use of the ToneShell backdoor. Explore their latest operation targeting attendees of a major defense and security summit.

New Loki Backdoor Emerges: A Private Agent for Mythic Framework Unveiled Loki backdoor
  • Malware

New Loki Backdoor Emerges: A Private Agent for Mythic Framework Unveiled

Do Son September 9, 2024 0

Learn about the new threat Loki, a sophisticated backdoor linked to the Mythic framework, posing challenges to cybersecurity defenders.

SpyAgent Malware Targets Crypto Wallets via Image Scanning SpyAgent
  • Malware

SpyAgent Malware Targets Crypto Wallets via Image Scanning

Do Son September 9, 2024 0

Beware of SpyAgent, a sophisticated Android malware targeting cryptocurrency wallets. Learn how to protect yourself from this insidious threat.

Chinese APT Stately Taurus Exploits Visual Studio Code in Cyberespionage Attacks The observed connection between Listener.bat of Stately Taurus and ShadowPad
  • Cyber Security
  • Malware

Chinese APT Stately Taurus Exploits Visual Studio Code in Cyberespionage Attacks

Do Son September 9, 2024 0

Discover the latest tactic employed by the Chinese APT group Stately Taurus. Learn how they abuse Visual Studio Code to gain unauthorized access to sensitive networks.
TIDRONE: The Unseen Cyberespionage Threat Targeting Taiwan’s Military and Satellite Industries TIDRONE
  • Cyber Security

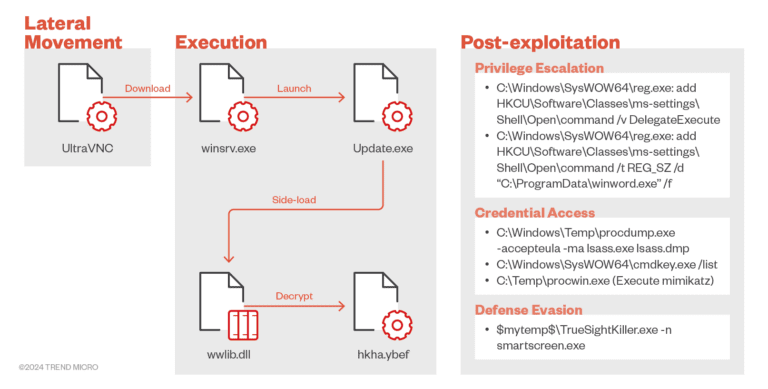
TIDRONE: The Unseen Cyberespionage Threat Targeting Taiwan’s Military and Satellite Industries

Do Son September 9, 2024 0

Learn about TIDRONE, a cyber threat targeting the Taiwanese military and satellite industries. Discover their motives, techniques, and the potential dangers for national security.

Critical Kibana Flaws (CVE-2024-37288, CVE-2024-37285) Expose Systems to Arbitrary Code Execution CVE-2024-37288 and CVE-2024-37285 Kibana XSS SSRF, Vega Vulnerability
  • Vulnerability

Critical Kibana Flaws (CVE-2024-37288, CVE-2024-37285) Expose Systems to Arbitrary Code Execution

Do Son September 8, 2024 0

URGENT: Critical security advisory for Kibana users. Update to version 8.15.1 now to mitigate vulnerabilities CVE-2024-37288 and CVE-2024-37285.

HAProxy Vulnerability CVE-2024-45506 Under Active Exploit: Urgent Patching Required HAProxy QUIC Vulnerability CVE-2026-26081 CVE-2024-45506 - HAProxy vulnerability
  • Vulnerability

HAProxy Vulnerability CVE-2024-45506 Under Active Exploit: Urgent Patching Required

Do Son September 8, 2024 0

Stay informed about the latest security vulnerability: CVE-2024-45506 impacting popular load balancing and proxy software HAProxy.

PoC Exploit Releases for Windows Elevation of Privilege Vulnerability CVE-2024-26230 CVE-2024-26230 PoC Exploit
  • Vulnerability

PoC Exploit Releases for Windows Elevation of Privilege Vulnerability CVE-2024-26230

Do Son September 8, 2024 0

Get insights into the technical details and PoC exploit of the serious elevation of privilege vulnerability (CVE-2024-26230) in Windows Telephony service

BlindEagle APT Targets Colombian Insurance with BlotchyQuasar RAT BlotchyQuasar RAT
  • Cyber Security
  • Malware

BlindEagle APT Targets Colombian Insurance with BlotchyQuasar RAT

Do Son September 8, 2024 0

BlindEagle APT group targets Colombian insurance sector with BlotchyQuasar RAT. Discover how this remote access trojan is compromising systems and monitoring banking activities.

Akira Ransomware Exploits SonicWall SSLVPN Flaw (CVE-2024-40766) Akira ransomware affiliates Akira Ransomware, SonicWall VPN
  • Malware
  • Vulnerability

Akira Ransomware Exploits SonicWall SSLVPN Flaw (CVE-2024-40766)

Do Son September 8, 2024 0

Learn about the active exploitation of a critical vulnerability in SonicWall devices by the notorious Akira ransomware affiliates.

Fog Ransomware Group Shifts Focus: Financial Sector Now in Crosshairs Fog Ransomware Group
  • Malware

Fog Ransomware Group Shifts Focus: Financial Sector Now in Crosshairs

Do Son September 8, 2024 0

Learn how the Fog ransomware group is targeting the financial services industry and how one cybersecurity company successfully mitigated an attack.
Predator Spyware Roars Back: New Infrastructure, Evasive Tactics Predator spyware
  • Cyber Security
  • Malware

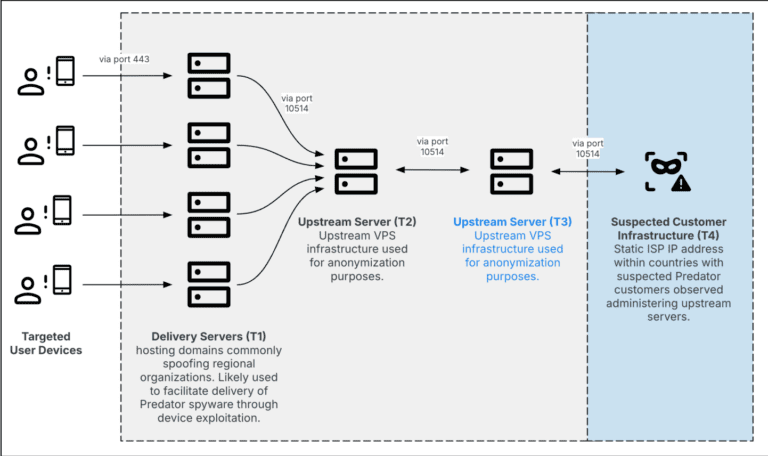
Predator Spyware Roars Back: New Infrastructure, Evasive Tactics

Do Son September 8, 2024 0

Learn about the reengineered spyware delivery system of the Predator spyware and its impact on global surveillance.

Beware the Drive-By Download: LummaC2 Stealer and Malicious Chrome Extension Wreak Havoc LummaC2 Stealer
  • Malware

Beware the Drive-By Download: LummaC2 Stealer and Malicious Chrome Extension Wreak Havoc

Do Son September 8, 2024 0

Stay informed about the latest malware threat: LummaC2 Stealer. Learn how this sophisticated campaign uses DLL side-loading to steal sensitive financial information.

MindsDB Fixes Critical CVE-2024-24759: DNS Rebinding Attack Bypasses Security Protections CVE-2024-24759 - MindsDB
  • Vulnerability

MindsDB Fixes Critical CVE-2024-24759: DNS Rebinding Attack Bypasses Security Protections

Do Son September 7, 2024 0

Learn how MindsDB, the open-source AI platform, patched a critical security vulnerability CVE-2024-24759, preventing potential attacks and ensuring user data safety.

Unmasking PackXOR: The FIN7 Packer Exposed PackXOR
  • Malware

Unmasking PackXOR: The FIN7 Packer Exposed

Do Son September 7, 2024 0

Explore the in-depth analysis of PackXOR, a private packer used by threat actors, including FIN7, to evade detection and carry out malicious activities.

Cybercriminals Target LatAm Banks: Mekotio, BBTok Lead the Charge mekotio banking trojan
  • Cyber Security
  • Malware

Cybercriminals Target LatAm Banks: Mekotio, BBTok Lead the Charge

Do Son September 7, 2024 0

Learn about the latest phishing tactics in Latin America and the reappearance of Mekotio, BBTok, and Grandoreiro banking Trojans.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114160CVSS 9.8
    Server-side request forgery (ssrf) in Azure Managed Grafana allows an unauthorized attacker to elevate privileges over a network.
    📅 Updated: Nov 11, 2026
  • CVE-2026-109469CVSS 10.0
    Authorization bypass through user-controlled key in Entra Device Registration allows an unauthorized attacker to elevate privileges over a...
    📅 Updated: Nov 11, 2026
  • CVE-2026-101763CVSS 9.8
    Vulnerability in the Oracle Communications BRM - Elastic Charging Engine product of Oracle Communications (component: Cloud native deployment)....
    📅 Updated: Nov 11, 2026
  • CVE-2026-101809CVSS 10.0
    Vulnerability in the Workflow product of Oracle E-Business Suite (component: Workflow Notification Mailer). Supported versions that are affected...
    📅 Updated: Nov 11, 2026
  • CVE-2026-126253CVSS 9.3
    An Authentication Bypass by Primary Weakness vulnerability [cwe-305] in FortiOS and FortiSASE ospf daemon may allow an unauthenticated...
    📅 Updated: Nov 11, 2026
  • CVE-2026-126170CVSS 9.8
    An Improper Encoding or Escaping of Output vulnerability [CWE-116] in FortiSASE-Sovereign, FortiAnalyzer, FortiManager, FortiAnalyzer Cloud, FortiManager Cloud and...
    📅 Updated: Nov 11, 2026
  • CVE-2026-91220CVSS 9.8
    Vulnerability in the Oracle Business Process Management Suite product of Oracle Fusion Middleware (component: Human Workflow). Supported versions...
    📅 Updated: Nov 11, 2026
  • CVE-2026-91222CVSS 9.9
    Vulnerability in the Oracle Business Process Management Suite product of Oracle Fusion Middleware (component: Human Workflow (11g+)). Supported...
    📅 Updated: Nov 11, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.