Skip to content
November 11, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The IP Wall Falls: Disney Invests $1B in OpenAI to License 200+ Characters for AI Disney OpenAI $1B, AI Character Licensing
  • Technology

The IP Wall Falls: Disney Invests $1B in OpenAI to License 200+ Characters for AI

Do Son December 12, 2025 0
Long regarded as the “most formidable legal department in the Western Hemisphere,” Disney has historically guarded its...
Read More Read more about The IP Wall Falls: Disney Invests $1B in OpenAI to License 200+ Characters for AI
The AI Super-App Rises: Photoshop & Adobe Express Integrate into ChatGPT OpenAI Adobe Integration, ChatGPT Super-App
  • Technology

The AI Super-App Rises: Photoshop & Adobe Express Integrate into ChatGPT

Do Son December 12, 2025 0
Following earlier integrations with Spotify and Canva, OpenAI has taken yet another decisive step toward its ambition...
Read More Read more about The AI Super-App Rises: Photoshop & Adobe Express Integrate into ChatGPT
The “USB-C of AI” is Here: Google Launches Managed Servers for MCP Protocol Google MCP Protocol, Agentic AI Managed Servers Google Cloud Meta Google Cloud UniSuper
  • Technology

The “USB-C of AI” is Here: Google Launches Managed Servers for MCP Protocol

Do Son December 12, 2025 0
Following the Linux Foundation’s establishment of the Agentic AI Foundation (AAIF) and its designation of the Model...
Read More Read more about The “USB-C of AI” is Here: Google Launches Managed Servers for MCP Protocol
YouTube TV’s New Subscription Bundles: Is Streaming Becoming Cable All Over Again? YouTube TV Gemini Ask YouTube TV Bundles, Streaming Cable Model
  • Technology

YouTube TV’s New Subscription Bundles: Is Streaming Becoming Cable All Over Again?

Do Son December 12, 2025 0
Streaming television appears to be retracing the path once taken by traditional cable. YouTube TV has announced...
Read More Read more about YouTube TV’s New Subscription Bundles: Is Streaming Becoming Cable All Over Again?
Farewell, Tabs: Google’s Experimental Disco Browser Generates Web Apps with AI Google Disco Browser, Gemini PWA Generation
  • Technology

Farewell, Tabs: Google’s Experimental Disco Browser Generates Web Apps with AI

Do Son December 12, 2025 0
The race among artificial intelligence models has entered a fevered, white-hot phase—and AI-driven browsers have now gained...
Read More Read more about Farewell, Tabs: Google’s Experimental Disco Browser Generates Web Apps with AI
React Patches Two New Flaws Risking Server-Crashing DoS and Source Code Disclosure React Server Components Vulnerability CVE-2026-23870 React Server Components Server-Side DoS React DoS Vulnerability CVE-2026-23864 React Server Components DoS, Source Code Disclosure React RCE, Server Components Deserialization CVE-2025-55182
  • Vulnerability Report

React Patches Two New Flaws Risking Server-Crashing DoS and Source Code Disclosure

Do Son December 12, 2025 0
The security saga surrounding React Server Components continues this week. Just days after the React team patched...
Read More Read more about React Patches Two New Flaws Risking Server-Crashing DoS and Source Code Disclosure
Core Banking System Flaw: Apache Fineract IDOR Risks Authorization Bypass & Customer Data Access CVE-2024-32838 Apache Fineract IDOR, Core Banking Bypass
  • Vulnerability Report

Core Banking System Flaw: Apache Fineract IDOR Risks Authorization Bypass & Customer Data Access

Do Son December 12, 2025 0
A trio of security vulnerabilities has been disclosed in Apache Fineract, the open-source core banking system that...
Read More Read more about Core Banking System Flaw: Apache Fineract IDOR Risks Authorization Bypass & Customer Data Access
New 01flip Ransomware Hits APAC Critical Infra: Cross-Platform Rust Weapon Uses Sliver C2 01flip Rust Ransomware, Cross-Platform APAC
  • Malware

New 01flip Ransomware Hits APAC Critical Infra: Cross-Platform Rust Weapon Uses Sliver C2

Do Son December 12, 2025 0
A new and sophisticated ransomware player has entered the cybercrime arena, targeting critical infrastructure in the Asia-Pacific...
Read More Read more about New 01flip Ransomware Hits APAC Critical Infra: Cross-Platform Rust Weapon Uses Sliver C2
CISA KEV Alert: GeoServer XXE Flaw Under Active Attack Risks Data Theft & Internal Network Scanning CISA active exploit catalog known exploited vulnerabilities ActiveMQ RCE CVE-2026-34197 CISA KEV Catalog Actively Exploited Vulnerabilities CISA KEV Catalog CVE-2025-37164 GeoServer XXE, CISA KEV FortiWeb SQLi, CISA KEV Critical Vulnerabilities CVE-2024-20953
  • Vulnerability Report

CISA KEV Alert: GeoServer XXE Flaw Under Active Attack Risks Data Theft & Internal Network Scanning

Do Son December 12, 2025 0
The Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability affecting the widely used OSGeo...
Read More Read more about CISA KEV Alert: GeoServer XXE Flaw Under Active Attack Risks Data Theft & Internal Network Scanning
Military-Grade ValleyRAT Goes Rogue: Kernel Rootkit Builder Leak Triggers Massive Global Surge ValleyRAT Builder Leak, Kernel Rootkit Comoditization
  • Malware

Military-Grade ValleyRAT Goes Rogue: Kernel Rootkit Builder Leak Triggers Massive Global Surge

Do Son December 12, 2025 0
A sophisticated cyber weapon previously linked to targeted espionage has gone rogue, flooding the threat landscape after...
Read More Read more about Military-Grade ValleyRAT Goes Rogue: Kernel Rootkit Builder Leak Triggers Massive Global Surge
❮ Prev Page
Next Page ❯
CosmicBeetle’s ScRansom Ransomware: A Growing Threat to European and Asian Businesses CosmicBeetle - ScRansom
  • Cyber Security
  • Malware

CosmicBeetle’s ScRansom Ransomware: A Growing Threat to European and Asian Businesses

Do Son September 11, 2024 0

Discover the latest developments in the activities of the threat actor known as CosmicBeetle and its new custom ransomware tool, ScRansom.

Cybercriminals Increasingly Target Google, Microsoft, and Amazon in Sophisticated Phishing Schemes Atera RAT
  • Cyber Security

Cybercriminals Increasingly Target Google, Microsoft, and Amazon in Sophisticated Phishing Schemes

Do Son September 11, 2024 0

Discover the danger of typosquatting and brand impersonation in phishing campaigns. Tech giants like Google, Microsoft, and Amazon are top targets.

PAN-OS Vulnerabilities: Command Injection (CVE-2024-8686) and GlobalProtect Exposure (CVE-2024-8687) CVE-2024-8686 & CVE-2024-8687
  • Vulnerability

PAN-OS Vulnerabilities: Command Injection (CVE-2024-8686) and GlobalProtect Exposure (CVE-2024-8687)
Do Son September 11, 2024 0

Protect your organization from critical vulnerabilities in Palo Alto Networks products. Learn more about CVE-2024-8686 and CVE-2024-8687.

FBI’s 2023 Cryptocurrency Fraud Report: $5.6 Billion Lost in Exploding Investment Scams SEC Crypto Regulation, Project Crypto Stablecoin Regulation, GENIUS Act Cryptocurrency Fraud Report Garantex, stablecoin
  • Cyber Security

FBI’s 2023 Cryptocurrency Fraud Report: $5.6 Billion Lost in Exploding Investment Scams

Do Son September 11, 2024 0

Discover the alarming trends in cryptocurrency fraud. Learn about the growing threat of investment scams and the billions of dollars lost in 2023.

Scattered Spider Targets the Cloud: A Growing Threat to the Insurance and Financial Sectors Scattered Spider attack
  • Cyber Security

Scattered Spider Targets the Cloud: A Growing Threat to the Insurance and Financial Sectors

Do Son September 11, 2024 0

Discover the alarming rise of Scattered Spider's ransomware attacks on cloud infrastructures. Find out how they exploit cloud-native tools and manipulate MFA settings.

Fake Recruiter Coding Tests Target Developers with Malicious Python Packages in Ongoing North Korean Cyber Campaign Oracle EBS Zero-Day, GRACEFUL SPIDER Cracked Software, Supply Chain Attack Black Basta - NOVA stealer
  • Cyber Security
  • Malware

Fake Recruiter Coding Tests Target Developers with Malicious Python Packages in Ongoing North Korean Cyber Campaign

Do Son September 11, 2024 0

Stay informed about the sophisticated VMConnect cyber campaign targeting developers. Discover the tactics used by North Korea's Lazarus Group.
MiniTool ShadowMaker 4.5: Your Simple, Powerful Backup Solution Screenshot 2024-09-12 074754
  • Technique

MiniTool ShadowMaker 4.5: Your Simple, Powerful Backup Solution

Do Son September 11, 2024 0
In the ever-evolving digital landscape, the data backup is very important. From accidental deletions and hardware failures...
Read More Read more about MiniTool ShadowMaker 4.5: Your Simple, Powerful Backup Solution
Emergence of Repellent Scorpius: Distributors of Cicada3301 Ransomware Cicada3301 Ransomware
  • Cyber Security
  • Malware

Emergence of Repellent Scorpius: Distributors of Cicada3301 Ransomware

Do Son September 11, 2024 0

Learn about the rise of Repellent Scorpius, a ransomware group employing the Cicada3301 ransomware and a multi-extortion model.

CVE-2024-43491 (CVSS 9.8): Critical Windows 0-Day Flaw Uncovered, Urgent Patching Required CVE-2024-43491 - Windows Update
  • Vulnerability
  • Windows

CVE-2024-43491 (CVSS 9.8): Critical Windows 0-Day Flaw Uncovered, Urgent Patching Required

Do Son September 11, 2024 0

Discover the severity of CVE-2024-43491, a critical zero-day vulnerability in Windows Update. Learn how it can lead to remote code execution and system compromise.

LNK Stomping (CVE-2024-38217): Microsoft Patches Years-Old Zero-Day Flaw CVE-2024-38217 - LNK stomping
  • Vulnerability
  • Windows

LNK Stomping (CVE-2024-38217): Microsoft Patches Years-Old Zero-Day Flaw

Do Son September 11, 2024 0

Discover the details of CVE-2024-38217 (LNK stomping), a zero-day vulnerability affecting Microsoft Defender. See how hackers exploit this flaw to bypass security safeguards.

From Charging to Hijacking: The Autel MaxiCharger Vulnerability Autel MaxiCharger
  • Vulnerability

From Charging to Hijacking: The Autel MaxiCharger Vulnerability

Do Son September 10, 2024 0

Discover the security risks associated with the Autel MaxiCharger: researchers demonstrate how it can be remotely compromised.

CVE-2024-45032 (CVSS 10): Siemens Issues Critical Security Patch for Industrial Edge Management CVE-2024-33698 & CVE-2024-35783 & CVE-2024-45032
  • Vulnerability

CVE-2024-45032 (CVSS 10): Siemens Issues Critical Security Patch for Industrial Edge Management

Do Son September 10, 2024 0

Discover the potential consequences of CVE-2024-45032, a critical vulnerability in Siemens' Industrial Edge Management platform.

CVE-2024-45411: Twig Sandbox Bypass Vulnerability Puts PHP Applications at Risk CVE-2024-45411
  • Vulnerability

CVE-2024-45411: Twig Sandbox Bypass Vulnerability Puts PHP Applications at Risk

Do Son September 10, 2024 0

Stay protected from the critical security vulnerability CVE-2024-45411 in Twig template engine. Learn how to safeguard your web applications.

CVE-2024-6596 (CVSS 9.8): Critical Code Injection Flaw Found in Endress+Hauser Products CVE-2024-6596 - Endress+Hauser
  • Vulnerability

CVE-2024-6596 (CVSS 9.8): Critical Code Injection Flaw Found in Endress+Hauser Products

Do Son September 10, 2024 0

Critical security vulnerability (CVE-2024-6596) in Endress+Hauser products. Learn about the risk, impacts, and steps to protect your systems.
Cybercriminals Exploit Legitimate Windows Tool for Cryptojacking Binary Managed Object File
  • Malware

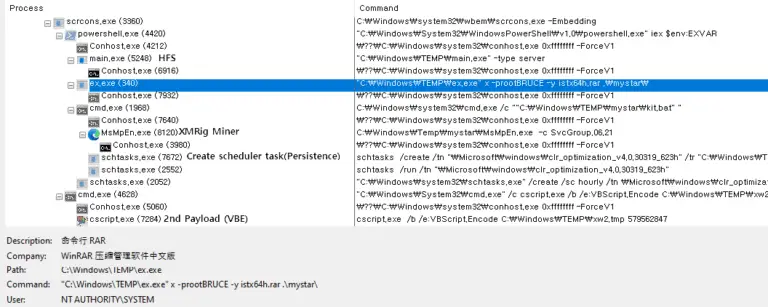
Cybercriminals Exploit Legitimate Windows Tool for Cryptojacking

Do Son September 10, 2024 0

ASEC reveals the increasing sophistication of cybercriminals distributing XMRig malware through Binary Managed Object Files. Stay informed about this threat.

Microsoft’s September Patch Tuesday: A Patchwork of Urgency with 4 Zero-Days Under Attack Microsoft Patch Tuesday September
  • Vulnerability
  • Windows

Microsoft’s September Patch Tuesday: A Patchwork of Urgency with 4 Zero-Days Under Attack

Do Son September 10, 2024 0

Learn about the crucial Microsoft Patch Tuesday September updates. Protect your systems from 79 vulnerabilities, including zero-day exploits.

CVE-2024-42500 (CVSS 9.3): Critical HPE HP-UX Vulnerability Demands Immediate Action HPE HP-UX - CVE-2024-42500 CVE-2024-540385
  • Vulnerability

CVE-2024-42500 (CVSS 9.3): Critical HPE HP-UX Vulnerability Demands Immediate Action

Do Son September 10, 2024 0

Protect your HPE HP-UX systems from a critical vulnerability (CVE-2024-42500) that could lead to DoS attacks. Take action now to safeguard your organization's data.

Earth Preta’s Cyber Arsenal Expands: New Malware and Strategies Target APAC Governments Earth Preta
  • Cyber Security
  • Malware

Earth Preta’s Cyber Arsenal Expands: New Malware and Strategies Target APAC Governments

Do Son September 10, 2024 0

Discover the evolving tactics of Earth Preta, a notorious cyber espionage group, and their heightened threat to government entities in the APAC region.

CVE-2024-8517: Critical SPIP Flaw Leaves Websites Vulnerable to Remote Attacks, PoC Published CVE-2024-8517 exploit
  • Vulnerability

CVE-2024-8517: Critical SPIP Flaw Leaves Websites Vulnerable to Remote Attacks, PoC Published

Do Son September 10, 2024 0

SPIP CMS at risk! Read about CVE-2024-8517, a critical security vulnerability that enables unauthenticated attackers to take control of affected servers.

Quad7 Operators Unveil New Moves with Advanced HTTP Reverse Shells and Botnet Expansion FsyNet
  • Malware

Quad7 Operators Unveil New Moves with Advanced HTTP Reverse Shells and Botnet Expansion

Do Son September 10, 2024 0

Discover the evolving techniques and growing threat of the Quad7 botnet. Learn about their new tools and tactics aimed at evading detection and expanding their reach.

Ivanti Issues Patch for Critical Vulnerabilities in Endpoint Manager, Including CVE-2024-29847 (CVSS 10.0) Ivanti EPM Vulnerability CVE-2026-1603 Ivanti EPM Critical XSS, Unauthenticated File Write CVE-2024-29847 & CVE-2024-8190 Ivanti ITSM, Authentication Bypass
  • Vulnerability

Ivanti Issues Patch for Critical Vulnerabilities in Endpoint Manager, Including CVE-2024-29847 (CVSS 10.0)

Do Son September 10, 2024 0

Stay protected with Ivanti Endpoint Manager (EPM) updates. Address critical vulnerabilities like CVE-2024-29847 to secure your organization's endpoints.

Siemens Issues Critical Security Advisory for User Management Component (UMC) – CVE-2024-33698 CVE-2024-33698 & CVE-2024-35783 & CVE-2024-45032
  • Vulnerability

Siemens Issues Critical Security Advisory for User Management Component (UMC) – CVE-2024-33698

Do Son September 10, 2024 0

Discover the critical vulnerability CVE-2024-33698 in Siemens' User Management Component (UMC) and its potential impact on industrial control systems.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114160CVSS 9.8
    Server-side request forgery (ssrf) in Azure Managed Grafana allows an unauthorized attacker to elevate privileges over a network.
    📅 Updated: Nov 11, 2026
  • CVE-2026-109469CVSS 10.0
    Authorization bypass through user-controlled key in Entra Device Registration allows an unauthorized attacker to elevate privileges over a...
    📅 Updated: Nov 11, 2026
  • CVE-2026-101763CVSS 9.8
    Vulnerability in the Oracle Communications BRM - Elastic Charging Engine product of Oracle Communications (component: Cloud native deployment)....
    📅 Updated: Nov 11, 2026
  • CVE-2026-101809CVSS 10.0
    Vulnerability in the Workflow product of Oracle E-Business Suite (component: Workflow Notification Mailer). Supported versions that are affected...
    📅 Updated: Nov 11, 2026
  • CVE-2026-126253CVSS 9.3
    An Authentication Bypass by Primary Weakness vulnerability [cwe-305] in FortiOS and FortiSASE ospf daemon may allow an unauthenticated...
    📅 Updated: Nov 11, 2026
  • CVE-2026-126170CVSS 9.8
    An Improper Encoding or Escaping of Output vulnerability [CWE-116] in FortiSASE-Sovereign, FortiAnalyzer, FortiManager, FortiAnalyzer Cloud, FortiManager Cloud and...
    📅 Updated: Nov 11, 2026
  • CVE-2026-91220CVSS 9.8
    Vulnerability in the Oracle Business Process Management Suite product of Oracle Fusion Middleware (component: Human Workflow). Supported versions...
    📅 Updated: Nov 11, 2026
  • CVE-2026-91222CVSS 9.9
    Vulnerability in the Oracle Business Process Management Suite product of Oracle Fusion Middleware (component: Human Workflow (11g+)). Supported...
    📅 Updated: Nov 11, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.