Muhstik Malware Exploits Apache RocketMQ Flaw: Thousands at Risk Malware Muhstik Malware Exploits Apache RocketMQ Flaw: Thousands at Risk Do Son June 6, 2024 0 Read More Read more about Muhstik Malware Exploits Apache RocketMQ Flaw: Thousands at Risk
CVE-2024-20404/20405: Cisco Finesse Vulnerabilities Open Door to Attacks Vulnerability CVE-2024-20404/20405: Cisco Finesse Vulnerabilities Open Door to Attacks Do Son June 6, 2024 0 Read More Read more about CVE-2024-20404/20405: Cisco Finesse Vulnerabilities Open Door to Attacks
ThinkPHP Vulnerabilities Under Active Exploit: Researchers Warn Cyber Security Vulnerability ThinkPHP Vulnerabilities Under Active Exploit: Researchers Warn Do Son June 6, 2024 0 Read More Read more about ThinkPHP Vulnerabilities Under Active Exploit: Researchers Warn
Beware of Fake Advanced IP Scanner: Malicious Installer Delivers CobaltStrike Backdoor Cyber Security Malware Beware of Fake Advanced IP Scanner: Malicious Installer Delivers CobaltStrike Backdoor Do Son June 6, 2024 0 Read More Read more about Beware of Fake Advanced IP Scanner: Malicious Installer Delivers CobaltStrike Backdoor
xFileSyncerx: Malicious Package with Wiper Components Discovered on PyPI Malware xFileSyncerx: Malicious Package with Wiper Components Discovered on PyPI Do Son June 6, 2024 0 Read More Read more about xFileSyncerx: Malicious Package with Wiper Components Discovered on PyPI
Zerologon Vulnerability Strikes Again: RansomHub Exploits Legacy Flaw Malware Zerologon Vulnerability Strikes Again: RansomHub Exploits Legacy Flaw Do Son June 6, 2024 0 Read More Read more about Zerologon Vulnerability Strikes Again: RansomHub Exploits Legacy Flaw
Commando Cat Cryptojacking Campaign Unleashed: Docker Users Under Threat Cyber Security Malware Commando Cat Cryptojacking Campaign Unleashed: Docker Users Under Threat Do Son June 6, 2024 0 Read More Read more about Commando Cat Cryptojacking Campaign Unleashed: Docker Users Under Threat
libaom Video Codec Library Exposed: Critical CVE-2024-5171 Vulnerability with CVSS 10 Vulnerability libaom Video Codec Library Exposed: Critical CVE-2024-5171 Vulnerability with CVSS 10 Do Son June 5, 2024 0 Read More Read more about libaom Video Codec Library Exposed: Critical CVE-2024-5171 Vulnerability with CVSS 10
Cybercriminal on Cybercriminal Crime: Ransomware Hijacks CoinMiner Cyber Security Malware Cybercriminal on Cybercriminal Crime: Ransomware Hijacks CoinMiner Do Son June 5, 2024 0 Read More Read more about Cybercriminal on Cybercriminal Crime: Ransomware Hijacks CoinMiner
Secshow’s Massive DNS Probing Operation Exposed Cyber Security Secshow’s Massive DNS Probing Operation Exposed Do Son June 5, 2024 0 Read More Read more about Secshow’s Massive DNS Probing Operation Exposed
Beware of “How to Fix” Button: New Phishing Emails Trick Users into Executing Malicious Commands Malware Beware of “How to Fix” Button: New Phishing Emails Trick Users into Executing Malicious Commands Do Son June 5, 2024 0 Read More Read more about Beware of “How to Fix” Button: New Phishing Emails Trick Users into Executing Malicious Commands
CVE-2024-4295: Critical Vulnerability in Popular WordPress Plugin Exposes 90K+ Sites Vulnerability CVE-2024-4295: Critical Vulnerability in Popular WordPress Plugin Exposes 90K+ Sites Do Son June 5, 2024 0 Read More Read more about CVE-2024-4295: Critical Vulnerability in Popular WordPress Plugin Exposes 90K+ Sites
Kali Linux 2024.2 Released: An Upgrade for the Penetration Tester’s Arsenal Linux Kali Linux 2024.2 Released: An Upgrade for the Penetration Tester’s Arsenal Do Son June 5, 2024 0 Read More Read more about Kali Linux 2024.2 Released: An Upgrade for the Penetration Tester’s Arsenal
TargetCompany Ransomware Evolves: New Linux Variant Targets ESXi Environments Cyber Security Malware TargetCompany Ransomware Evolves: New Linux Variant Targets ESXi Environments Do Son June 5, 2024 0 Read More Read more about TargetCompany Ransomware Evolves: New Linux Variant Targets ESXi Environments
Parrot OS 6.1: The Ultimate Update for Security Experts Linux Parrot OS 6.1: The Ultimate Update for Security Experts Do Son June 5, 2024 0 Read More Read more about Parrot OS 6.1: The Ultimate Update for Security Experts
TikTok Hit by Zero-Day Attack: High-Profile Accounts Compromised Vulnerability TikTok Hit by Zero-Day Attack: High-Profile Accounts Compromised Do Son June 5, 2024 0 Read More Read more about TikTok Hit by Zero-Day Attack: High-Profile Accounts Compromised
Proof-of-Concept Code Released for Linux Kernel Exploit Vulnerability Proof-of-Concept Code Released for Linux Kernel Exploit Do Son June 4, 2024 0 Read More Read more about Proof-of-Concept Code Released for Linux Kernel Exploit
Apache Wicket Addresses Critical RCE Vulnerability (CVE-2024-36522) Vulnerability Apache Wicket Addresses Critical RCE Vulnerability (CVE-2024-36522) Do Son June 4, 2024 0 Read More Read more about Apache Wicket Addresses Critical RCE Vulnerability (CVE-2024-36522)
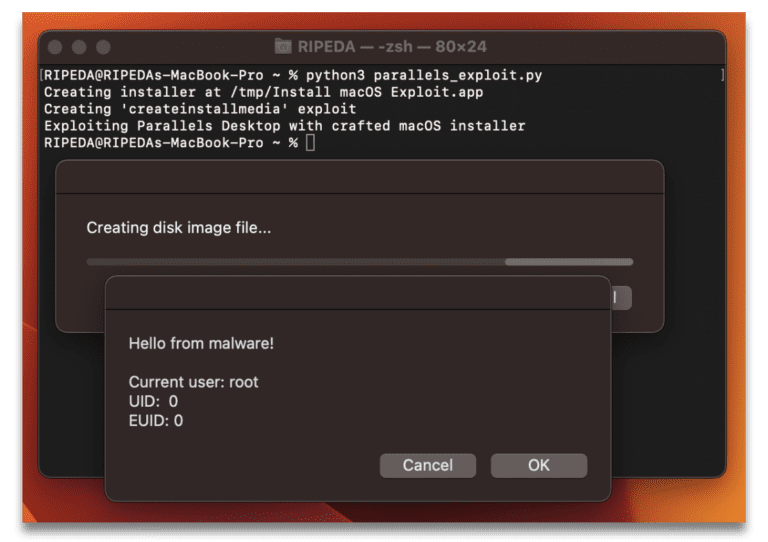
CVE-2024-34331: Parallels Desktop Vulnerability Gives Root to Hackers, PoC Published Vulnerability CVE-2024-34331: Parallels Desktop Vulnerability Gives Root to Hackers, PoC Published Do Son June 4, 2024 0 Read More Read more about CVE-2024-34331: Parallels Desktop Vulnerability Gives Root to Hackers, PoC Published
UNC1151 Escalates Cyber Warfare: Attacks Target Ukrainian Defense Infrastructure Cyber Security Malware UNC1151 Escalates Cyber Warfare: Attacks Target Ukrainian Defense Infrastructure Do Son June 4, 2024 0 Read More Read more about UNC1151 Escalates Cyber Warfare: Attacks Target Ukrainian Defense Infrastructure
Tripwire Enterprise Faces Critical Authentication Bypass Flaw (CVE-2024-4332) Vulnerability Tripwire Enterprise Faces Critical Authentication Bypass Flaw (CVE-2024-4332) Do Son June 4, 2024 0 Read More Read more about Tripwire Enterprise Faces Critical Authentication Bypass Flaw (CVE-2024-4332)
CVE-2024-27348: Apache HugeGraph RCE Vulnerability, PoC Exploit Published Vulnerability CVE-2024-27348: Apache HugeGraph RCE Vulnerability, PoC Exploit Published Do Son June 4, 2024 0 Read More Read more about CVE-2024-27348: Apache HugeGraph RCE Vulnerability, PoC Exploit Published

 Do Son