Tripwire Enterprise Faces Critical Authentication Bypass Flaw (CVE-2024-4332) Vulnerability Tripwire Enterprise Faces Critical Authentication Bypass Flaw (CVE-2024-4332) Do Son June 4, 2024 0 Read More Read more about Tripwire Enterprise Faces Critical Authentication Bypass Flaw (CVE-2024-4332)
CVE-2024-27348: Apache HugeGraph RCE Vulnerability, PoC Exploit Published Vulnerability CVE-2024-27348: Apache HugeGraph RCE Vulnerability, PoC Exploit Published Do Son June 4, 2024 0 Read More Read more about CVE-2024-27348: Apache HugeGraph RCE Vulnerability, PoC Exploit Published
Azure Service Tags Vulnerability Exposes Cloud Services to Potential Attacks Vulnerability Azure Service Tags Vulnerability Exposes Cloud Services to Potential Attacks Do Son June 4, 2024 0 Read More Read more about Azure Service Tags Vulnerability Exposes Cloud Services to Potential Attacks
Urgent Security Update for Zyxel NAS Devices: Patches Available for Critical Flaws Vulnerability Urgent Security Update for Zyxel NAS Devices: Patches Available for Critical Flaws Do Son June 3, 2024 0 Read More Read more about Urgent Security Update for Zyxel NAS Devices: Patches Available for Critical Flaws
macOS Root Access Exploit: PoC Code for CVE-2024-27822 Released Vulnerability macOS Root Access Exploit: PoC Code for CVE-2024-27822 Released Do Son June 3, 2024 0 Read More Read more about macOS Root Access Exploit: PoC Code for CVE-2024-27822 Released
CVE-2024-21512: MySQL2 Vulnerability Puts Millions of Downloads at Risk Vulnerability CVE-2024-21512: MySQL2 Vulnerability Puts Millions of Downloads at Risk Do Son June 3, 2024 0 Read More Read more about CVE-2024-21512: MySQL2 Vulnerability Puts Millions of Downloads at Risk
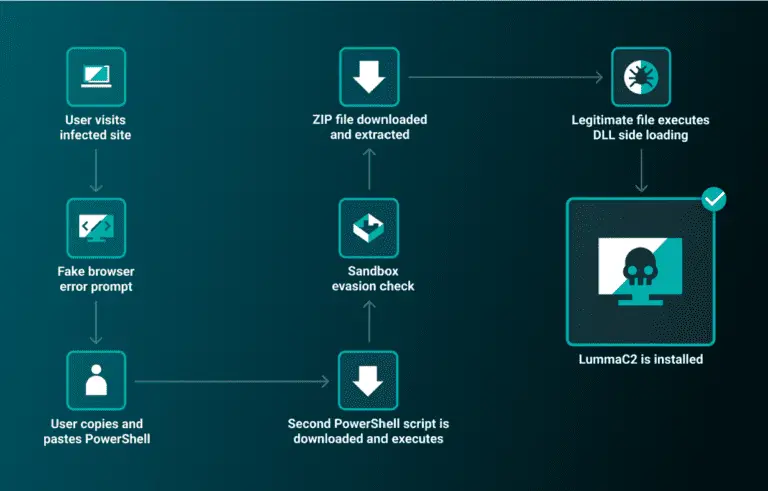
ClearFake Campaign Employs Novel Social Engineering Tactic to Deliver LummaC2 Infostealer Cyber Security Malware ClearFake Campaign Employs Novel Social Engineering Tactic to Deliver LummaC2 Infostealer Do Son June 3, 2024 0 Read More Read more about ClearFake Campaign Employs Novel Social Engineering Tactic to Deliver LummaC2 Infostealer
CVE-2024-3584: Critical Path Traversal Flaw Exposes Qdrant Vector Database to Remote Takeover Vulnerability CVE-2024-3584: Critical Path Traversal Flaw Exposes Qdrant Vector Database to Remote Takeover Do Son June 3, 2024 0 Read More Read more about CVE-2024-3584: Critical Path Traversal Flaw Exposes Qdrant Vector Database to Remote Takeover
Excel File Unleashes Sophisticated Cobalt Strike Cyberattack Cyber Security Malware Excel File Unleashes Sophisticated Cobalt Strike Cyberattack Do Son June 3, 2024 0 Read More Read more about Excel File Unleashes Sophisticated Cobalt Strike Cyberattack
CVE-2024-5404: Critical Vulnerability Found in moneo IIoT Platform Vulnerability CVE-2024-5404: Critical Vulnerability Found in moneo IIoT Platform Do Son June 3, 2024 0 Read More Read more about CVE-2024-5404: Critical Vulnerability Found in moneo IIoT Platform
Wave of Attacks on WordPress: Urgent Update for WP Statistics, WP Meta SEO, LiteSpeed Cache Cyber Security Vulnerability Wave of Attacks on WordPress: Urgent Update for WP Statistics, WP Meta SEO, LiteSpeed Cache Do Son June 3, 2024 0 Read More Read more about Wave of Attacks on WordPress: Urgent Update for WP Statistics, WP Meta SEO, LiteSpeed Cache
Patch Now to Avoid Apache OFBiz Remote Code Execution – CVE-2024-36104 Vulnerability Patch Now to Avoid Apache OFBiz Remote Code Execution – CVE-2024-36104 Do Son June 3, 2024 0 Read More Read more about Patch Now to Avoid Apache OFBiz Remote Code Execution – CVE-2024-36104
CVE-2024-29415: Popular Node.js Package ‘node-ip’ Exposes Millions to Potential SSRF Attacks Vulnerability CVE-2024-29415: Popular Node.js Package ‘node-ip’ Exposes Millions to Potential SSRF Attacks Do Son June 3, 2024 0 Read More Read more about CVE-2024-29415: Popular Node.js Package ‘node-ip’ Exposes Millions to Potential SSRF Attacks
13,800+ Check Point Gateways Exposed: 0-Day CVE-2024-24919 Flaw Under Attack Vulnerability 13,800+ Check Point Gateways Exposed: 0-Day CVE-2024-24919 Flaw Under Attack Do Son June 2, 2024 0 Read More Read more about 13,800+ Check Point Gateways Exposed: 0-Day CVE-2024-24919 Flaw Under Attack
Hugging Face Spaces Platform Hit by Unauthorized Access Cyber Security Data Leak Hugging Face Spaces Platform Hit by Unauthorized Access Do Son June 2, 2024 0 Read More Read more about Hugging Face Spaces Platform Hit by Unauthorized Access
CVE-2024-3820 (CVSS 10) in wpDataTables Puts 70,000 WordPress Sites at Risk Vulnerability CVE-2024-3820 (CVSS 10) in wpDataTables Puts 70,000 WordPress Sites at Risk Do Son June 2, 2024 0 Read More Read more about CVE-2024-3820 (CVSS 10) in wpDataTables Puts 70,000 WordPress Sites at Risk
BlueDelta: GRU-Linked Cyber Espionage Group Targets Critical European Networks Cyber Security Malware BlueDelta: GRU-Linked Cyber Espionage Group Targets Critical European Networks Do Son June 2, 2024 0 Read More Read more about BlueDelta: GRU-Linked Cyber Espionage Group Targets Critical European Networks
CVE-2024-32850 (CVSS 9.8): Critical Flaw in SkyBridge Routers Exposes Thousands to Cyberattacks Vulnerability CVE-2024-32850 (CVSS 9.8): Critical Flaw in SkyBridge Routers Exposes Thousands to Cyberattacks Do Son June 2, 2024 0 Read More Read more about CVE-2024-32850 (CVSS 9.8): Critical Flaw in SkyBridge Routers Exposes Thousands to Cyberattacks
CVE-2024-35204: Veritas System Recovery Vulnerability Puts Data at Risk Vulnerability CVE-2024-35204: Veritas System Recovery Vulnerability Puts Data at Risk Do Son June 2, 2024 0 Read More Read more about CVE-2024-35204: Veritas System Recovery Vulnerability Puts Data at Risk
Telegram: The Dark Horse of Website Malware Attacks Malware Telegram: The Dark Horse of Website Malware Attacks Do Son June 2, 2024 0 Read More Read more about Telegram: The Dark Horse of Website Malware Attacks
CarnavalHeist Banking Trojan Targets Brazilian Financial Institutions with Sophisticated Overlay Attacks Malware CarnavalHeist Banking Trojan Targets Brazilian Financial Institutions with Sophisticated Overlay Attacks Do Son June 2, 2024 0 Read More Read more about CarnavalHeist Banking Trojan Targets Brazilian Financial Institutions with Sophisticated Overlay Attacks
RedTail Cryptominer Malware Targets PAN-OS Vulnerability Malware Vulnerability RedTail Cryptominer Malware Targets PAN-OS Vulnerability Do Son June 1, 2024 0 Read More Read more about RedTail Cryptominer Malware Targets PAN-OS Vulnerability
 Do Son