
 Do Son
Salesforce has issued an urgent security alert after discovering unusual activity involving Gainsight-published applications connected to its...
Latest news

MTI Security researchers have identified a sophisticated new threat in the mobile landscape: Sturnus, a privately operated...

The AhnLab Security Intelligence Center (ASEC) has uncovered an active exploitation campaign in which threat actors weaponized...

SonicWall has issued a security advisory for a newly identified pre-authentication stack-based buffer overflow vulnerability in its...

Grafana has released emergency security updates for Grafana Enterprise addressing a critical privilege-escalation flaw in its SCIM...

NVIDIA has released its financial report for the third quarter of fiscal year 2026, directly addressing mounting...

OpenAI has announced the launch of ChatGPT for Teachers, an AI-powered service designed specifically for educators. The...

Google has released the second edition of its Accelerator Impact Report, reviewing the outcomes of its global...

The Mozilla Foundation’s open-source email client Thunderbird has released version 145.0, introducing full, native support for Microsoft...

According to the latest announcement from the European Commission, three investigations will be launched into cloud-computing services...

A new, insidious phishing scam targeting employees' Microsoft credentials has been unveiled by cybersecurity experts at Cofense

Adding to the urgency, the proof-of-concept (PoC) exploit code for CVE-2024-36401 has already been published online.

A critical zero-day vulnerability has been identified in Alibaba's Nacos platform, a widely used open-source tool for dynamic service

CVE-2024-6744 has been assigned a critical severity score of 9.8 on the CVSS scale, indicating its high potential impact on affected systems.

Alphabet, Google's parent company, plans to acquire the cybersecurity startup Wiz for $23 billion, with the deal potentially concluding soon.

Squarespace has recently issued a security advisory warning its customers of an ongoing domain hijacking campaign

In a recent vulnerability analysis by SSD Secure Disclosure, critical security flaws were discovered in the SonicWall SMA100 series

Supermicro Computer, a leading provider of server and motherboard solutions, has disclosed a critical security vulnerability (CVE-2024-36435)

MSI has experienced an identical security breach. Specific keywords in search engines can easily locate MSI's after-sales service site

Netgear emphasizes the importance of downloading and installing the firmware updates to mitigate the risks associated with these vulnerabilities
Mitel has issued two critical security advisories warning users of a severe vulnerability in the PHP scripting engine
ReversingLabs has uncovered a sophisticated malicious campaign targeting the NuGet package manager, a widely-used platform

Fabasoft has released security advisories addressing a high-severity vulnerability (CVE-2024-4367) in the widely used PDF.js library
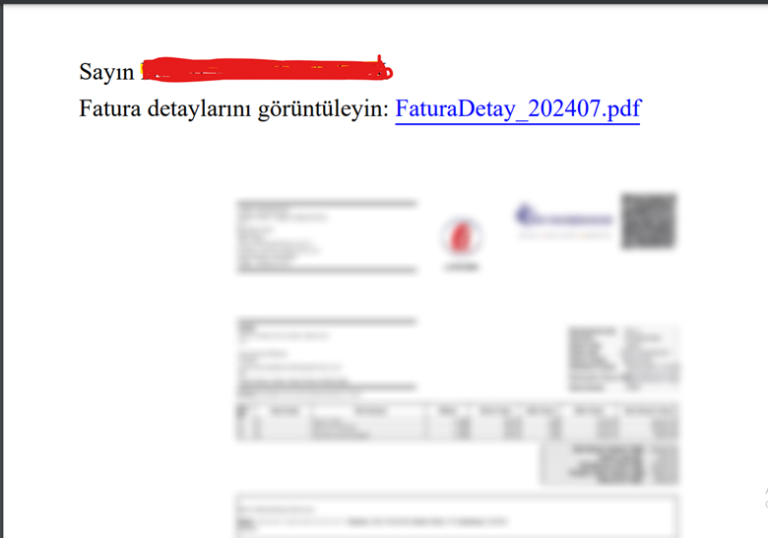
Forcepoint X-Labs has unveiled a new ransomware strain dubbed "ShadowRoot" specifically targeting Turkish businesses

Juniper Networks has issued patches to address five vulnerabilities discovered within its Junos OS Evolved operating system
A critical vulnerability in PHP, designated CVE-2024-4577, has become a prime target for cybercriminals within a day of its public disclosure

While initially focused on the mining sector, Cofense's report reveals that Poco RAT malware has expanded its reach into other industries

Japanese organizations are being targeted by the notorious North Korean advanced persistent threat (APT) group, Kimsuky

Kolte, who reported the CVE-2024-39202 flaw to D-Link, also published detailed technical information and a proof-of-concept (PoC) exploit code

Cloud Software Group has issued a security advisory warning customers of a critical vulnerability (CVE-2024-6387) in OpenSSH

DarkGate has reemerged, leveraging a clever combination of Microsoft Excel files and public Samba shares to distribute its malicious payload
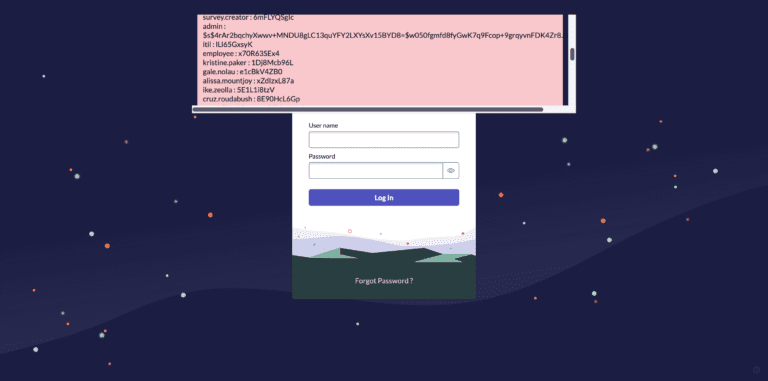
The most alarming of these flaws are CVE-2024-4879 and CVE-2024-5217, both carrying a critical CVSSv4 score of 9.3 and 9.2, respectively