
 Do Son
Apache Causeway, a popular framework for rapidly developing domain-driven Java applications, has been found vulnerable to a...
Latest news

For many public venues, large displays are used to show advertisements or important information — airports, for...

For years, driver-related failures have appeared with relentless regularity. Whether produced by hardware manufacturers or software vendors,...

 cybernewswire
Tel Aviv, Israel, 19th November 2025, CyberNewsWire

Palo Alto, California, 19th November 2025, CyberNewsWire

Cloudflare CEO Matthew Prince has issued a detailed explanation regarding the recent large-scale outage that took numerous...

At Microsoft’s recent Ignite 2025 developer conference, the spotlight focused on fully empowering the “AI lifecycle”—from foundational...
Apple has, for various reasons, adjusted AirDrop so that it now defaults to receiving content only from...

Dutch police recently seized a so-called “bulletproof hosting” provider operating in the Netherlands, confiscating 250 physical servers...

Singapore, Singapore, 19th November 2025, CyberNewsWire

This includes the use of LNK files, MSbuild for loading the fileless backdoor, and novel methods for disabling event logging

A severe vulnerability (CVE-2024-5441) has been discovered in the widely used WordPress plugin Modern Events Calendar
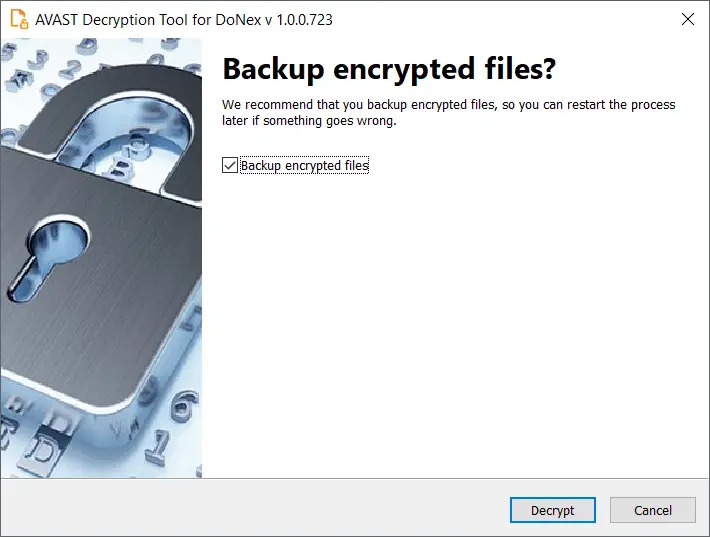
The free DoNex ransomware decryptor tool, now available to the public, is user-friendly and guides victims through the decryption process
Hardware manufacturer ZOTAC faced a significant security lapse that compromised sensitive customer information

Cisco has issued a critical security advisory, warning users of a high-severity vulnerability (CVE-2024-6387) codenamed "regreSSHion"

The most severe vulnerability (CVE-2024-39349) was a classic buffer overflow in the libjansson component, which could enable RCE

Halcyon's research team has identified a new ransomware group dubbed "Volcano Demon," responsible for a series of recent attacks

CRIL has revealed a surge in cyberattacks exploiting the patched Microsoft Defender SmartScreen vulnerability (CVE-2024-21412)

CVE-2024-6209 and CVE-2024-6298, pose a significant risk to organizations utilizing ASPECT for optimizing energy consumption in buildings

The AhnLab Security Intelligence Center (ASEC) has issued a warning about a new backdoor malware called HappyDoor

Trend Micro, a global leader in cybersecurity, has issued a warning about a recent wave of attacks targeting misconfigured Jenkins servers

The KDE development team has issued a critical security advisory warning users of a high-severity vulnerability (CVE-2024-36041)

The vulnerability, identified as CVE-2024-6376, stems from insufficient sandbox protection settings within the ejson shell parser

Cloudflare's popular 1.1.1.1 public DNS resolver service experienced disruptions, leaving a small percentage of users worldwide unable to access the service

To mitigate the risk posed by CVE-2024-39943, users of HFS are strongly advised to update their software to version 0.52.10 or later

Apache HTTP Server version 2.4.61, a crucial update that addresses a severe source code disclosure vulnerability (CVE-2024-39884)

The attack involves the distribution of trojanized versions of jQuery through dozens of packages on the npm repository

A high-severity vulnerability (CVE-2024-38513) has been discovered in Fiber, a widely-used web framework for the Go programming language

An analysis detailing the advanced evasion techniques employed by GootLoader, a pervasive malware known for its role in delivering ransomware

An attacker can first bypass authentication using CVE-2024-5716 and then leverage CVE-2024-5717 to execute arbitrary code

A new wave of cyberattacks utilizing the sophisticated Mekotio banking trojan is raising alarms across Latin America

The OpenStack Foundation has issued an urgent security advisory, disclosing a critical vulnerability (CVE-2024-32498)