
 Do Son
Microsoft has announced that Windows 11 will soon introduce an array of new recovery tools and capabilities...
Latest news

Google has announced the launch of Gemini 3, its newest generation of artificial intelligence models. CEO Sundar...

Following its recent revision of the partnership agreement with OpenAI, Microsoft has announced that it will further...

To reinforce its global leadership in artificial intelligence, Google has unveiled a major annual investment initiative titled...

Elon Musk’s artificial intelligence company, xAI, has launched a surprise offensive with the quiet release of its...

Google announced a suite of new tools and expanded capabilities for its “AI Mode,” enabling the system...

Fortinet has issued an urgent advisory warning customers that a newly disclosed vulnerability in FortiWeb, tracked as...

Security researchers at Oligo Security have uncovered a massive, fast-evolving cyberattack campaign hijacking exposed Ray AI clusters...

D-Link has issued a security advisory warning users of the DIR-878 router series that multiple newly disclosed...

METZ CONNECT GmbH, in coordination with CERT@VDE, has issued an urgent security advisory warning of multiple critical...

Victims whose files have been encrypted by the Mallox ransomware Linux variant may be able to recover their data using the decryptors

Security researchers from Graz University of Technology have unveiled a novel cybersecurity threat dubbed "SnailLoad" (CVE-2024-39920)
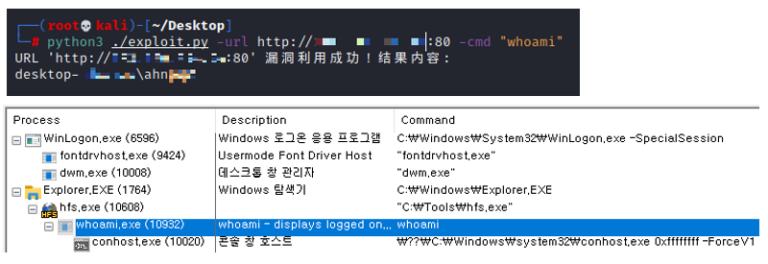
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware

Adding to the urgency, security researcher carsonchan12345 has published a proof-of-concept (PoC) exploit code for CVE-2024-37726

The team has observed a surge in malicious PDF files distributed via email, which contain embedded QR codes

SonarSource, a leading code security firm, has uncovered four unpatched vulnerabilities in Gogs, a popular open-source self-hosted Git service

CVE-2024-21586 (CVSSv4 8.7), allows unauthenticated attackers to remotely crash the Packet Forwarding Engine (PFE) and cause a DoS condition

A severe security flaw, CVE-2024-36401 (CVSS 9.8), has been discovered in GeoServer, a widely-used open-source software platform

Nearly three years after the notorious ProxyLogon and ProxyShell vulnerabilities caused widespread havoc on Microsoft Exchange servers

CVE-2024-6172 has been assigned a near-maximum CVSS score of 9.8, underscoring its critical nature & potential impact on the over 90,000 websites

Google released the July 2024 security patches for the Android operating system, which address several critical vulnerabilities

CVE-2024-38472 (Important): Server-Side Request Forgery (SSRF) vulnerability on Windows systems, potentially leaking sensitive NTML hashes

A security researcher has published a PoC exploit code targeting a high-severity CVE-2024-1085 vulnerability in the Linux kernel

McPhail has identified a critical vulnerability (CVE-2024-1724) in Snap, a popular package manager for Ubuntu and other Linux distributions
CVE-2024-3330 stems from insufficient input validation, allowing low-privileged attackers with read/write access to craft malicious Analyst files
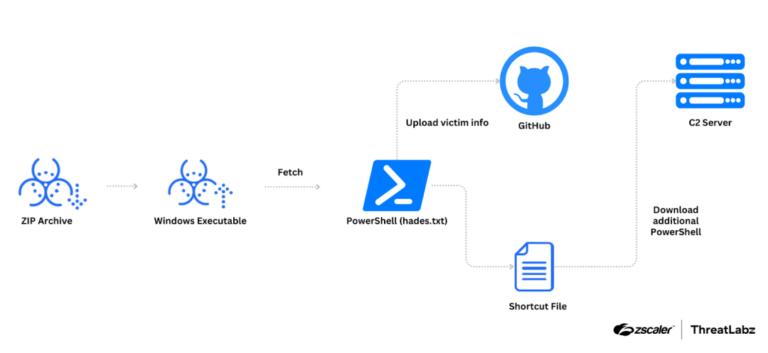
The group is deploying a malicious Google Chrome extension called "TRANSLATEXT" to steal sensitive information from South Korean academics

CVE-2024-20399 has been discovered in Cisco NX-OS Software, the operating system powering a wide range of Cisco's networking devices

TRU has detailed a CVE-2024-6387 flaw, dubbed 'regreSSHion,' that leaves millions of Linux systems vulnerable to remote code execution

Chrome 127 and all subsequent versions will no longer trust newly issued digital certificates from the U.S private software company, Entrust

A security researcher has released PoC exploit code targeting a high-severity vulnerability (CVE-2024-0193) within the Linux kernel

The Document Foundation has issued an urgent security advisory regarding a critical flaw (CVE-2024-5261) in its LibreOfficeKit component

Dubbed "Indirector" attacks, exploit weaknesses in the chip's branch prediction mechanisms to precisely manipulate program execution flow