
 Do Son
In a joint announcement, the Cybersecurity and Infrastructure Security Agency (CISA)—alongside the NSA, FBI, DoD Cyber Crime...
Latest news

A new technical deep-dive by malware researcher 0x0d4y reveals the inner workings of ScoringMathTea, a sophisticated remote...

A newly released analysis from Unit 42 details how a global data storage and infrastructure company was...

The Cybereason Threat Intelligence Team has published an in-depth analysis of a rapidly evolving ransomware group known...

The Akamai Hunt team has uncovered a new malware strain that hides its command-and-control (C2) traffic behind...

A new report from Trend Research warns that ransomware operators are rapidly shifting their focus from traditional...

A highly active cybercriminal group has shifted tactics in a long-running campaign that abuses remote monitoring and...

Apache Causeway, a popular framework for rapidly developing domain-driven Java applications, has been found vulnerable to a...

For many public venues, large displays are used to show advertisements or important information — airports, for...

For years, driver-related failures have appeared with relentless regularity. Whether produced by hardware manufacturers or software vendors,...

The most severe vulnerability (CVE-2024-39349) was a classic buffer overflow in the libjansson component, which could enable RCE

Halcyon's research team has identified a new ransomware group dubbed "Volcano Demon," responsible for a series of recent attacks

CRIL has revealed a surge in cyberattacks exploiting the patched Microsoft Defender SmartScreen vulnerability (CVE-2024-21412)

CVE-2024-6209 and CVE-2024-6298, pose a significant risk to organizations utilizing ASPECT for optimizing energy consumption in buildings

The AhnLab Security Intelligence Center (ASEC) has issued a warning about a new backdoor malware called HappyDoor

Trend Micro, a global leader in cybersecurity, has issued a warning about a recent wave of attacks targeting misconfigured Jenkins servers

The KDE development team has issued a critical security advisory warning users of a high-severity vulnerability (CVE-2024-36041)

The vulnerability, identified as CVE-2024-6376, stems from insufficient sandbox protection settings within the ejson shell parser

Cloudflare's popular 1.1.1.1 public DNS resolver service experienced disruptions, leaving a small percentage of users worldwide unable to access the service

To mitigate the risk posed by CVE-2024-39943, users of HFS are strongly advised to update their software to version 0.52.10 or later

Apache HTTP Server version 2.4.61, a crucial update that addresses a severe source code disclosure vulnerability (CVE-2024-39884)

The attack involves the distribution of trojanized versions of jQuery through dozens of packages on the npm repository

A high-severity vulnerability (CVE-2024-38513) has been discovered in Fiber, a widely-used web framework for the Go programming language

An analysis detailing the advanced evasion techniques employed by GootLoader, a pervasive malware known for its role in delivering ransomware

An attacker can first bypass authentication using CVE-2024-5716 and then leverage CVE-2024-5717 to execute arbitrary code

A new wave of cyberattacks utilizing the sophisticated Mekotio banking trojan is raising alarms across Latin America

The OpenStack Foundation has issued an urgent security advisory, disclosing a critical vulnerability (CVE-2024-32498)

Victims whose files have been encrypted by the Mallox ransomware Linux variant may be able to recover their data using the decryptors

Security researchers from Graz University of Technology have unveiled a novel cybersecurity threat dubbed "SnailLoad" (CVE-2024-39920)
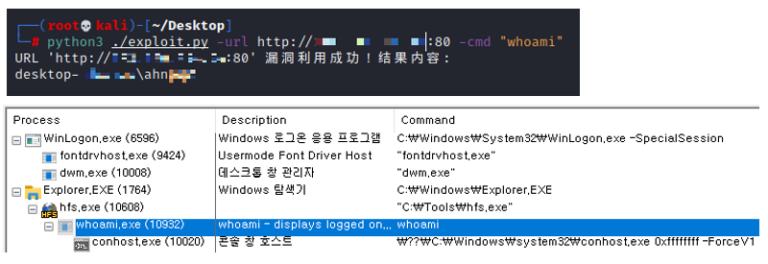
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware

Adding to the urgency, security researcher carsonchan12345 has published a proof-of-concept (PoC) exploit code for CVE-2024-37726

The team has observed a surge in malicious PDF files distributed via email, which contain embedded QR codes