
 Do Son
SonicWall has issued a security advisory for a newly identified pre-authentication stack-based buffer overflow vulnerability in its...
Latest news

Grafana has released emergency security updates for Grafana Enterprise addressing a critical privilege-escalation flaw in its SCIM...

NVIDIA has released its financial report for the third quarter of fiscal year 2026, directly addressing mounting...

OpenAI has announced the launch of ChatGPT for Teachers, an AI-powered service designed specifically for educators. The...

Google has released the second edition of its Accelerator Impact Report, reviewing the outcomes of its global...

The Mozilla Foundation’s open-source email client Thunderbird has released version 145.0, introducing full, native support for Microsoft...

According to the latest announcement from the European Commission, three investigations will be launched into cloud-computing services...

In May 2025, Google introduced a one-year Google AI Pro subscription package for university students across the...

ASUSTOR has issued a security advisory warning of a critical DLL hijacking vulnerability affecting its backup and...

A widely used Python library implementing JOSE standards, joserfc, has disclosed a critical uncontrolled resource consumption vulnerability—tracked...

The lighttpd project has now obtained CVE-2018-25103 to formally identify the vulnerability and alert supply-chain partners

Group-IB provides a detailed examination of this breach, shedding light on the tactics employed by the emerging threat actor known as EstateRansomware

CVE-2024-6385 enables attackers to impersonate other users and run arbitrary pipeline jobs, posing a significant risk

These vulnerabilities, assigned CVEs 2024-28747 through 2024-28751, could allow attackers to seize control of affected devices

Recorded Future's Insikt Group has exposed "Vortax," as a sophisticated front for a massive malware operation targeting cryptocurrency users

Security researcher Janggggg has disclosed PoC exploit code for three vulnerabilities (CVE-2024-38023, CVE-2024-38024, CVE-2024-38094)

CVE-2024-6235 and CVE-2024-6236 could allow unauthorized access to sensitive information and even cause denial-of-service (DoS) attacks

OpenVPN, a leading provider of virtual private network solutions, has refuted claims of zero-day vulnerabilities in its OpenVPN2 software

According to the ImmuneFi Severity Classification System, the severity of CVE-2024-39696 has been classified as Critical

Despite the critical nature of CVE-2023-46685, LevelOne has declined to patch the vulnerability in their software.

A new, insidious phishing scam impersonating India's RTO has been detected, preying on unsuspecting Android users via WhatsApp

Cybersecurity researchers at Morphisec have discovered a critical zero-click remote code execution (RCE) vulnerability, CVE-2024-38021

This zero-day vulnerability, designated CVE-2024-38112, has been addressed by Microsoft in its July 2024 Patch Tuesday update

CVE-2024-6409, has been found to expose systems to potential remote code execution (RCE) due to a race condition in signal handling

A PoC exploit has been released, targeting a recently patched high-severity vulnerability (CVE-2024-22274) in the VMware vCenter Server

The most severe vulnerability, CVE-2024-36138, is a bypass of an incomplete fix for a previous issue, CVE-2024-27980

Apache Software Foundation has issued an urgent security advisory, disclosing two critical vulnerabilities (CVE-2024-38346 and CVE-2024-39864)

This includes the use of LNK files, MSbuild for loading the fileless backdoor, and novel methods for disabling event logging

A severe vulnerability (CVE-2024-5441) has been discovered in the widely used WordPress plugin Modern Events Calendar
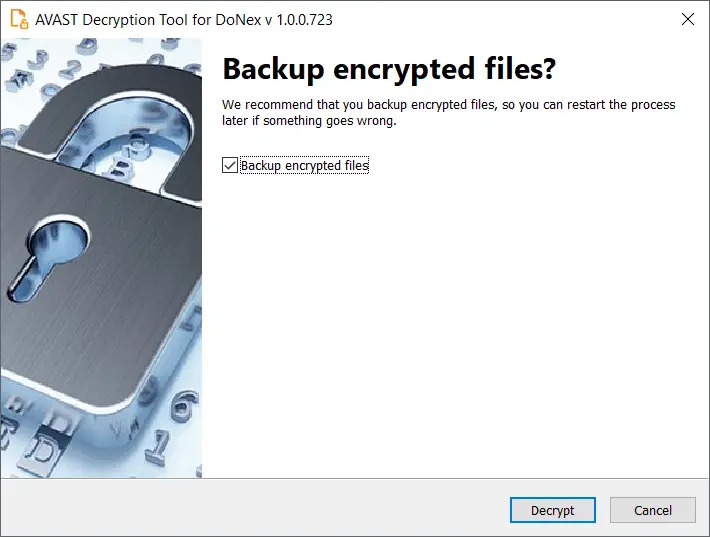
The free DoNex ransomware decryptor tool, now available to the public, is user-friendly and guides victims through the decryption process
Hardware manufacturer ZOTAC faced a significant security lapse that compromised sensitive customer information

Cisco has issued a critical security advisory, warning users of a high-severity vulnerability (CVE-2024-6387) codenamed "regreSSHion"