
 Do Son
SonicWall has released security updates addressing two vulnerabilities in its Email Security appliances, including one that could...
Latest news
AI agentic browsers have shifted from simple internet gateways to active tools. They rely on autonomous agents...
Have you ever gotten a text from your bank asking if you just spent money in a...

Google announced that its cross-platform file-sharing service, Android Quick Share, will officially support interoperability with Apple’s AirDrop,...

Earlier this year, Chromium browser engineers began submitting code to develop a vertical tab feature. This capability...

OpenAI began limited testing of ChatGPT’s group chat feature last week, and after a short trial period,...

Google announced the release of the Nano Banana Pro image-generation model, the successor to the Nano Banana...

Salesforce has issued an urgent security alert after discovering unusual activity involving Gainsight-published applications connected to its...

MTI Security researchers have identified a sophisticated new threat in the mobile landscape: Sturnus, a privately operated...

The AhnLab Security Intelligence Center (ASEC) has uncovered an active exploitation campaign in which threat actors weaponized...

Squarespace has recently issued a security advisory warning its customers of an ongoing domain hijacking campaign

In a recent vulnerability analysis by SSD Secure Disclosure, critical security flaws were discovered in the SonicWall SMA100 series

Supermicro Computer, a leading provider of server and motherboard solutions, has disclosed a critical security vulnerability (CVE-2024-36435)

MSI has experienced an identical security breach. Specific keywords in search engines can easily locate MSI's after-sales service site

Netgear emphasizes the importance of downloading and installing the firmware updates to mitigate the risks associated with these vulnerabilities
Mitel has issued two critical security advisories warning users of a severe vulnerability in the PHP scripting engine
ReversingLabs has uncovered a sophisticated malicious campaign targeting the NuGet package manager, a widely-used platform

Fabasoft has released security advisories addressing a high-severity vulnerability (CVE-2024-4367) in the widely used PDF.js library
Forcepoint X-Labs has unveiled a new ransomware strain dubbed "ShadowRoot" specifically targeting Turkish businesses

Juniper Networks has issued patches to address five vulnerabilities discovered within its Junos OS Evolved operating system
A critical vulnerability in PHP, designated CVE-2024-4577, has become a prime target for cybercriminals within a day of its public disclosure

While initially focused on the mining sector, Cofense's report reveals that Poco RAT malware has expanded its reach into other industries

Japanese organizations are being targeted by the notorious North Korean advanced persistent threat (APT) group, Kimsuky

Kolte, who reported the CVE-2024-39202 flaw to D-Link, also published detailed technical information and a proof-of-concept (PoC) exploit code

Cloud Software Group has issued a security advisory warning customers of a critical vulnerability (CVE-2024-6387) in OpenSSH

DarkGate has reemerged, leveraging a clever combination of Microsoft Excel files and public Samba shares to distribute its malicious payload
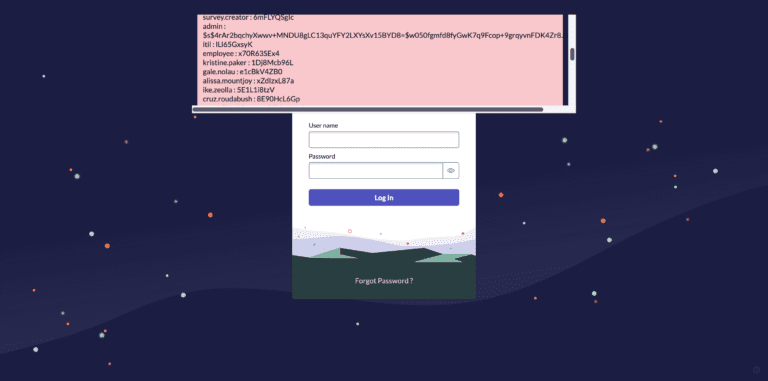
The most alarming of these flaws are CVE-2024-4879 and CVE-2024-5217, both carrying a critical CVSSv4 score of 9.3 and 9.2, respectively

These vulnerabilities, identified as CVE-2024-6422 and CVE-2024-6421, pose significant risks, including information disclosure

ASEC reveals new cyberattacks utilizing a novel method to distribute the AsyncRAT remote access trojan (RAT)

Session Hijacking: Unauthorized users may hijack console sessions, gaining elevated privileges (CVE-2024-36451).

CVE-2024-5910 affects Expedition configuration management tool and could allow an attacker with network access to take over admin accounts

Resurgence of Mirai botnet variants, coupled with AI-enhanced DDoS attacks, underscores the critical need for robust cybersecurity measures