
 Do Son
Jamf Threat Labs has uncovered a new macOS infostealer—named DigitStealer—that demonstrates an unusually high degree of sophistication,...
Latest news

Researchers at Palo Alto Networks Unit 42 have uncovered two expansive and interconnected malware campaigns active throughout...

eSentire’s Threat Response Unit (TRU) has uncovered a widespread malware operation leveraging a deceptive social-engineering technique known...

Elastic Security Labs has uncovered a highly sophisticated malware campaign led by the Dragon Breath APT group...

The United States Cybersecurity and Infrastructure Security Agency (CISA), alongside a coalition of global law-enforcement and cybersecurity...

Google has issued an urgent, out-of-band security update for the Chrome Stable channel, addressing two separate Type...

 cybernewswire
Menlo Park, California, USA, 17th November 2025, CyberNewsWire


According to a report by Bloomberg journalist Mark Gurman, Apple appears to have abandoned the Mac Pro....

Google has suffered yet another setback on Europe’s antitrust front. According to a report from Reuters, a...

Advanced Persistent Threat (APT) group APT-C-35, also known as DoNot Team, has been identified as one of the actors employing Rafel RAT
Tracked as CVE-2024-5756 (CVSS 9.8), the flaw allows unauthenticated attackers to inject malicious code into the plugin's database queries

A new ransomware-as-a-service (RaaS) called RansomHub has emerged, targeting Windows, Linux, and ESXi operating systems

In a recent report, the eSentire Threat Response Unit (TRU) has uncovered a sophisticated adware strain dubbed AdsExhaust

The flaw, designated CVE-2024-2003 (CVSS 7.3) and discovered by the Zero Day Initiative, could have allowed attackers to escalate privileges

Cisco Talos identified the SneakyChef group after observing a series of cyberattacks using the SugarGh0st RAT to target users
ANY.RUN, a popular malware analysis service, has reported a recent security incident involving a phishing attack

The vulnerability, tracked as CVE-2024-6027 (CVSS 9.8), could allow attackers to extract sensitive information from a store's database

The flaw, designated CVE-2024-28397 and assigned a high CVSS score of 8.8, enables malicious actors to break out of the JavaScript sandbox

The vulnerability, identified as CVE-2024-36680, allows unauthorized users to inject malicious SQL code into the website's database

A newly discovered vulnerability dubbed "CosmicSting" (CVE-2024-34102) has sent shockwaves through the e-commerce world
Given the critical nature of these vulnerabilities, it is imperative for all Ghostscript users to update to version 10.03.1 immediately

From early to mid-June 2024, the Zergeca botnet primarily targeted regions such as Canada, the United States, and Germany
CVE-2024-0087, rated with a critical CVSS score of 9.0, allows attackers to exploit Triton Server's log configuration interface to write arbitrary files

SocGholish, a sophisticated JavaScript malware framework, has been a persistent threat since its emergence in 2017.

The French National Cybersecurity Agency (ANSSI) has issued a warning about the continued activity of the Nobelium intrusion set

The perpetrators, utilizing tools linked to various Chinese espionage groups, have successfully penetrated these telecom networks

Fortra has issued a security advisory warning users of a high-severity flaw (CVE-2024-5275) in both FileCatalyst Direct and FileCatalyst Workflow

CVE-2024-28995 is a path-traversal vulnerability that allows unauthenticated attackers to retrieve arbitrary files from the filesystem

UNC3886 exploited a now-patched vulnerability in FortiOS, alongside a custom malware ecosystem targeting Fortinet devices

DataDog Security Labs has uncovered a concerning campaign targeting Amazon Web Services (AWS) environments
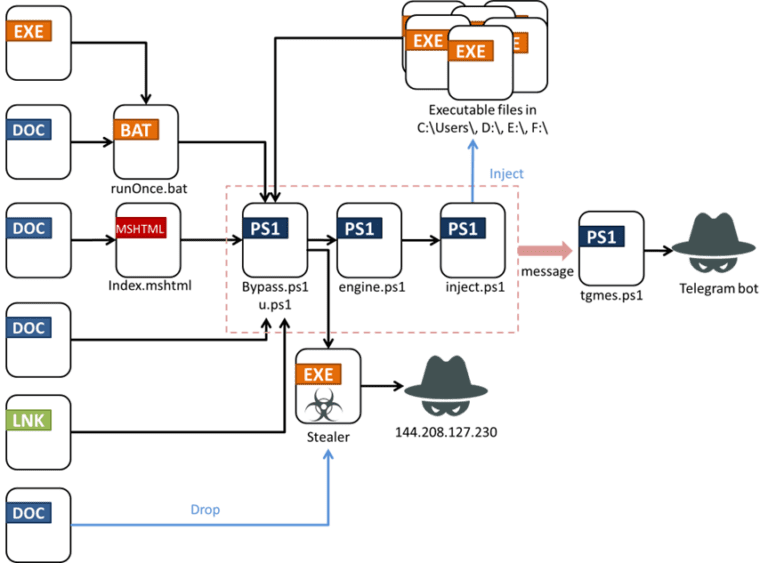
Fickle Stealer executes several scripts designed to bypass User Account Control (UAC) and prepare the environment for the main payload