
 Do Son
The Acronis Threat Research Unit (TRU) has identified a new DragonForce ransomware variant that showcases a dramatic...
Latest news

 cybernewswire

Intel is currently undergoing a massive wave of layoffs. Over the past few years, the chipmaker has...

Microsoft’s Threat Intelligence team has disclosed a novel side-channel attack on remote language models, demonstrating that a...

In addition to the upcoming satellite features for the iPhone, Bloomberg News has outlined Apple’s ambitious 2026...

According to a report by Bloomberg’s Mark Gurman in his latest Power On newsletter, Apple is actively...

Researchers from Unit 42, the threat intelligence team at Palo Alto Networks, have discovered a previously unknown...

Researchers at zLabs have uncovered a sophisticated Android Remote Access Trojan (RAT) known as Fantasy Hub, being...

A sophisticated supply-chain attack has been uncovered in the NuGet package registry, where nine packages published under...

A sophisticated, self-propagating malware campaign known as GlassWorm has re-emerged, infecting three new VS Code extensions and...
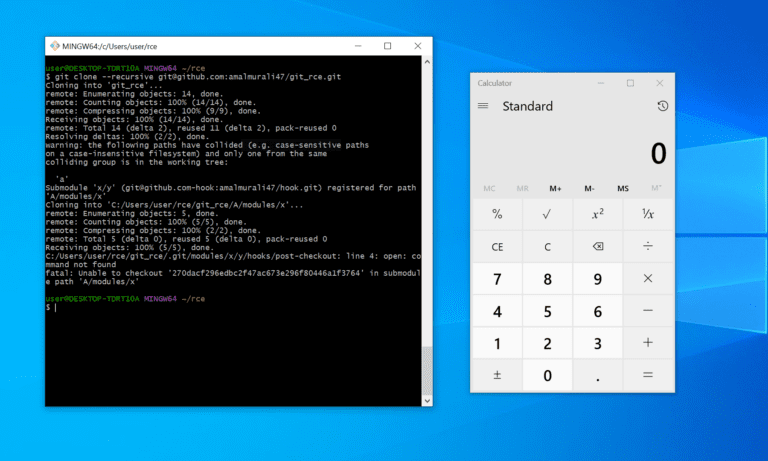
In addition to the technical details, Murali crafted a proof-of-concept (PoC) exploit for CVE-2024-32002 to demonstrate the RCE.

The North Korean state-sponsored group Springtail (also known as Kimsuky) has added a new Linux backdoor, dubbed Gomir, to its arsenal
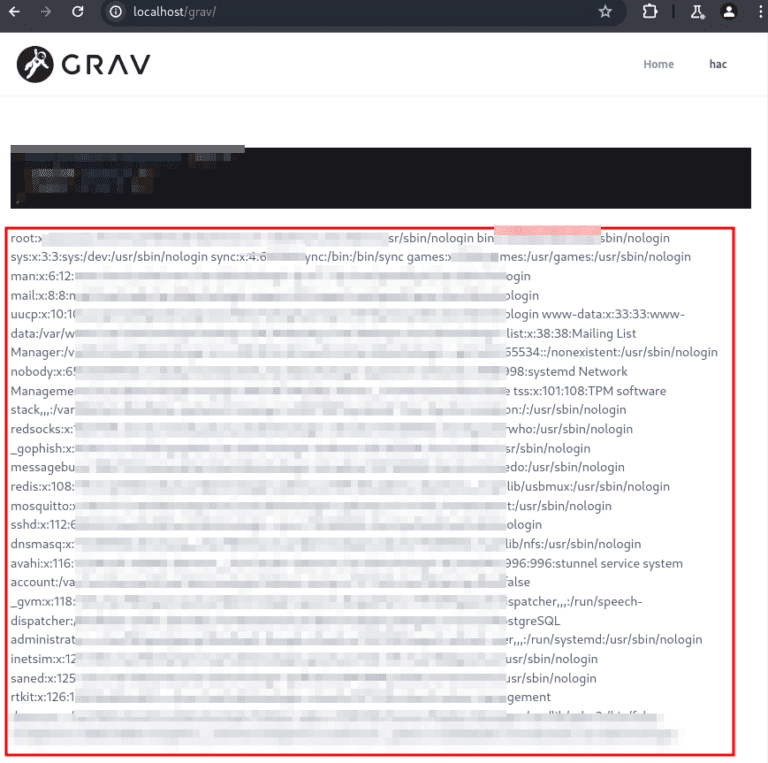
Tracked as CVE-2024-34082 (CVSS 8.5), the vulnerability stems from Grav's use of the Twig templating engine.

This novel use of Tesseract is part of a broader strategy by ViperSoftX to install additional malware strains, including Quasar RAT

A recent analysis by S-RM, a global cybersecurity consultancy, has shed light on the escalating sophistication of...

A series of critical vulnerabilities have been discovered in the XStore theme and its accompanying XStore Core plugin

Exploiting CVE-2024-22120 allows attackers to dump any values from the database, including sensitive information

Each tasked with managing activities and establishing communication with compromised IPs to facilitate the distribution of XMRig cryptominers

Bryan Smith shared the technical details and a proof-of-concept (PoC) for CVE-2024-22026 in Ivanti's Enterprise Mobility Management Platform

The flaw, tracked as CVE-2024-22476, could allow an unauthenticated attacker to “enable escalation of privilege via remote access”.

The campaign, dubbed UNK_SweetSpecter, utilizes a Remote Access Trojan (RAT) known as SugarGh0st to infiltrate systems and exfiltrate sensitive data

A critical SQL injection vulnerability (CVE-2024-32888) has been discovered in the Amazon JDBC Driver for Redshift
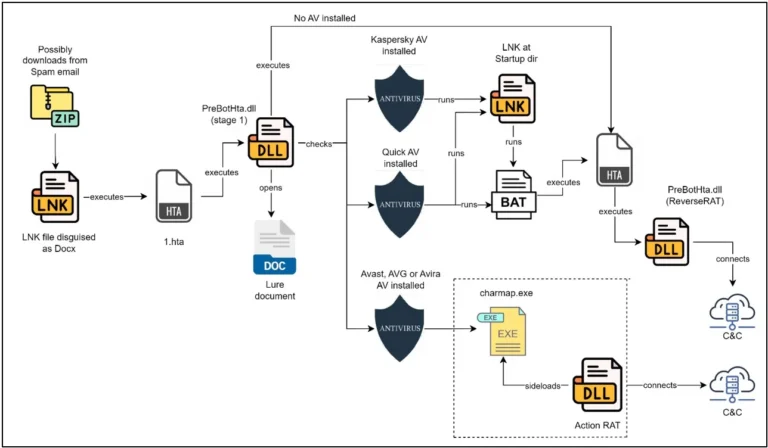
Upon further investigation, CRIL uncovered the use of malicious LNK files in the SideCopy malware campaign. These files, once executed

The PrestaShop project has recently issued a security advisory revealing two significant vulnerabilities (CVE-2024-34716 & CVE-2024-34717)

The campaign exploits GitHub, a legitimate platform for software development, to distribute various malware families

The campaign's success lies in its ability to bypass MFA, a security measure designed to protect accounts from unauthorized access

Two of the vulnerabilities, CVE-2014-100005 and CVE-2021-40655, affect specific models of D-Link routers (DIR-600 and DIR-605)

CVE-2024-22039, CVE-2024-22040, and CVE-2024-22041, reside within the network communication stack of the affected systems

CVE-2024-4984 could allow malicious actors to inject harmful scripts into websites, potentially compromising visitor data, redirecting traffic

Git project addressed a series of critical security flaws that could expose users to remote code execution (CVE-2024-32002, CVE-2024-32004)

One of the most prevalent scams involves the Instagram influencer program, designed to connect content creators with brand partnerships

A critical vulnerability (CVE-2024-34070) has been discovered in Froxlor, a popular open-source web hosting control panel