
 Do Son
Adobe has recently unveiled a major update to its generative AI suite Firefly, dramatically expanding its capabilities...
Latest news

The AhnLab Security Intelligence Center (ASEC) has published an in-depth analysis of the Gunra ransomware group, which...

Cybersecurity researchers at ThreatFabric have discovered a new Android banking Trojan dubbed Herodotus, a malware strain that...

The Docker Compose project has disclosed a high-severity path traversal vulnerability tracked as CVE-2025-62725 (CVSS v4 8.9),...

The North Korean APT group BlueNoroff — also known as Sapphire Sleet, APT38, Alluring Pisces, Stardust Chollima,...


The Akamai Security Intelligence Group has issued an urgent warning after observing active exploitation in the wild...

Researchers at the AhnLab Security Intelligence Center (ASEC) have released an in-depth analysis of the Beast ransomware...

A newly disclosed vulnerability, CVE-2025-61481, rated a maximum CVSS score of 10.0, affects MikroTik RouterOS (v7.14.2) and...

Researchers from Trend Research have identified a major evolution in the Water Saci malware campaign, marking one...

Security researchers at SonicWall Capture Labs have uncovered a dangerous new variant of the WhiteSnake information stealer

malicious Android apps are disguising themselves as beloved gaming titles to sneak onto your device and unleash a torrent of intrusive advertisements

Netskope Threat Labs has uncovered a sneaky malware campaign misusing a popular Google service to deliver the infamous Azorult infostealer

A serious vulnerability (CVE-2024-1753) has been discovered in the popular containerization tools Podman and Buildah

The core issue within CVE-2024-22257 lies in the way Spring Security handles authentication checks when its AuthenticatedVoter

PixPirate departs from the traditional method of malware hiding by removing the application icon via the SetComponentEnabledSetting API

The Earth Krahang threat actor uses a combination of brute-force attacks and custom scripts to breach email servers and steal sensitive data.

CVE-2024-28353 and CVE-2024-28354 leave these routers alarmingly exposed to potential remote takeover by cyberattackers

Fujitsu, the Japanese multinational technology giant, has revealed a data breach resulting from a malware infection within its corporate network

These patches address two flaws (CVE-2024-23138 & CVE-2024-23139) that could have severe consequences for users of affected software versions

The report from F-Secure on the “free wedding invite” scam is a stark reminder of the ever-evolving landscape of cyber threats

This new loader isn't limited to SPARKRAT; they've found versions containing Cobalt Strike – a penetration testing framework often misused by hackers

AutoSmuggle represents a pivotal development in the malware delivery arena. By embedding executable or archive files within SVG or HTML files

BlueSpy exploit highlights how the widespread use of insecure pairing methods in consumer Bluetooth headsets poses a significant privacy risk

Introduction In the realm of DNS (Domain Name System) configurations, the debate between Anycast and Unicast has...

Mitel has issued a critical security patch to address a vulnerability (CVE-2024-28815) in its InAttend and CMG products

CVE-2024-23334 in the popular Python web framework aiohttp has swiftly landed on the radar of notorious ransomware operators, ShadowSyndicate

CVE-2024-27307 poses a serious security risk & could allow attackers to remotely execute malicious code within apps that rely on the library

Apache ZooKeeper, a widely used coordination service for distributed applications, has a serious security flaw, tracked as CVE-2024-23944

Phoenix Contact has issued an urgent security alert regarding multiple critical vulnerabilities discovered within the firmware of CHARX SEC
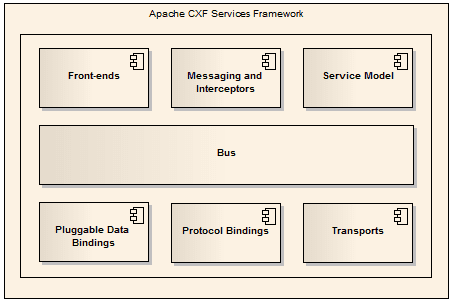
A Server-Side Request Forgery (SSRF) vulnerability, tracked as CVE-2024-28752, has been discovered in versions before 4.0.4, 3.6.3, and 3.5.8

ELVIA INFOTECH operate a 'Malware-as-a-Service' (MaaS) model, essentially providing ready-made phishing scams and malware to criminals