
 Do Son
According to a report by the Financial Times, Apple has lost a major antitrust class-action lawsuit in...
Latest news

OpenAI recently announced the acquisition of a company called Software Applications, best known for its newly released...

Following the massive service outage that occurred on October 20 in its US-EAST-1 (Northern Virginia) region, AWS...

Amazon has officially relaunched its cloud gaming and streaming service, Amazon Luna, which had been teased for...

Following Microsoft’s announcement in May of this year that it would lay off 3% of its global...

Amazon recently confirmed that it is developing a pair of smart glasses designed specifically for its delivery...

The Wordfence Threat Intelligence team has issued a new warning about the resurgence of large-scale attacks exploiting...

 cybernewswire

Palo Alto Networks’ Unit 42 has published an in-depth analysis of a financially motivated cyber campaign dubbed...

Researchers from Symantec and Carbon Black have published a detailed analysis of Warlock ransomware, a newly emerging...
This flaw (CVE-2024-1403) carries a CVSS score of 10 – the highest severity rating possible, affecting Progress OpenEdge

Stored XSS vulnerability (CVE-2023-40000) was recently discovered and patched in the widely used WordPress plugin LiteSpeed Cache

Daikin Industries recently faced a challenging situation - a data breach compromising the personal data of its suppliers
A significant security flaw (CVE-2023-50379) has been uncovered in Apache Ambari versions earlier than 2.7.8
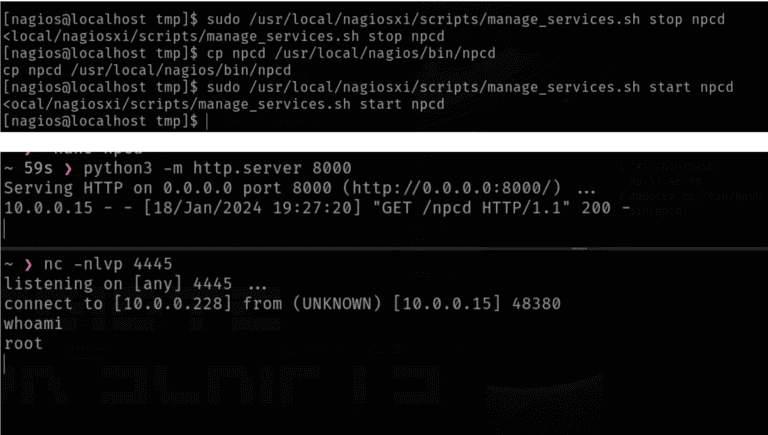
These vulnerabilities, assigned CVE-2024-24401 and CVE-2024-24402, leave businesses using Nagios XI exposed to potential cyberattacks

Forcepoint has uncovered a sophisticated malware campaign exploiting Booking.com's brand reputation to deliver Agent Tesla malware
A critical SQL injection vulnerability (CVE-2024-1698) was discovered in the widely used NotificationX WordPress plugin

Cyble Research and Intelligence Labs has uncovered a sophisticated phishing campaign actively exploiting ConnectWise ScreenConnect
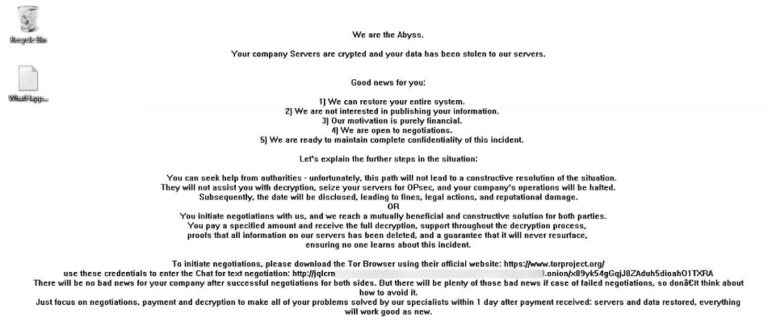
Abyss Locker ransomware terminates a plethora of processes related to security, productivity, and system management software

The quest to hire Fullstack Python developers is more than a mere task in this digital environment,...
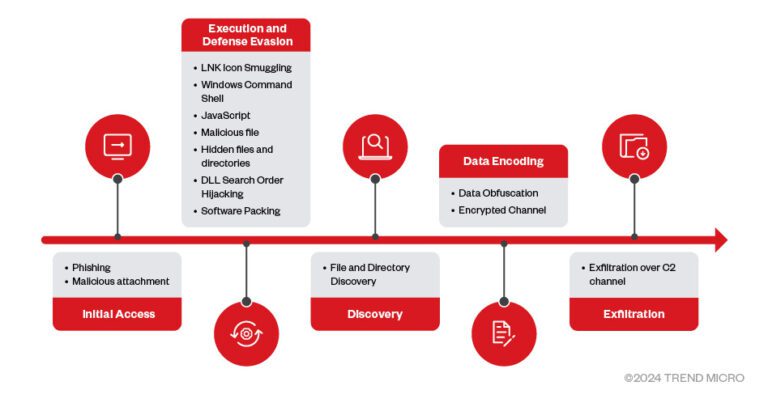
A startling revelation linked Earth Lusca to a Chinese entity known as I-Soon, unmasked through a breach of private documents
These vulnerabilities, dubbed CVE-2024-26592 (CVSS 9.0) and CVE-2024-26594 (CVSS 9.3), carried severe consequences

The infamous PlugX RAT, used by various threat actors, frequently leverages DLL side-loading to evade detection

The new PIKABOT version introduces a novel unpacking method alongside heavy obfuscation, marking a significant evolution in its design

This campaign, attributed to the Russia-aligned Doppelgänger network, focused on anti-Ukrainian content but has expanded to target audiences

The campaign investigated demonstrates Turla's focus on targeted attacks. This 'Pelmeni Wrapper' loads the next stage payload.
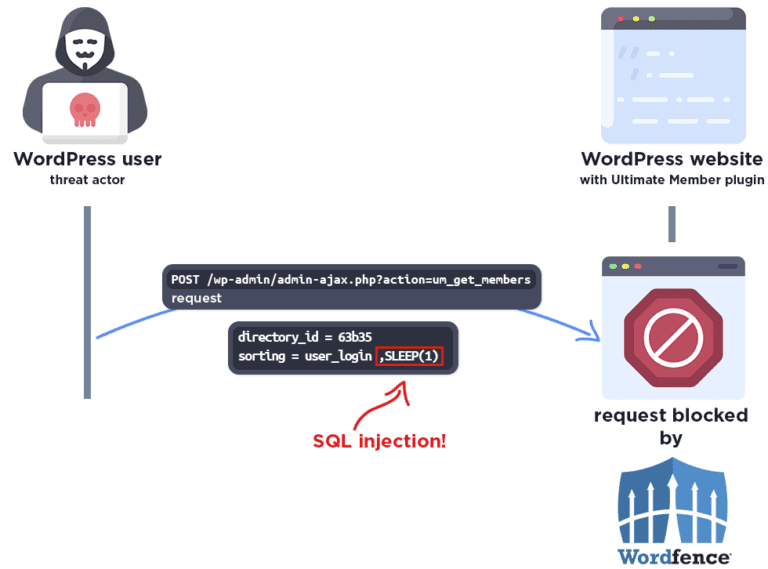
CVE-2024-1071 (CVSS 9.8), underscoring the grave risk it poses to websites utilizing this widely adopted plugin

The recently disclosed vulnerabilities in ScreenConnect (CVE-2024-1709, CVE-2024-1708) necessitate immediate action

In an era where digital transactions are ubiquitous, the significance of safeguarding these interactions cannot be overstated....

A high-severity vulnerability, designated CVE-2024-26582, has been discovered within the Transport Layer Security subsystem of the Linux kernel

The CVE-2024-23204 vulnerability existed in macOS and iOS devices running versions before macOS Sonoma 14.3, iOS 17.3, and iPadOS 17.3

VOLTZITE, a threat group known for persistent targeting of global critical infrastructure sectors, continues to refine its methods