
 Do Son
Swiss building automation manufacturer Sauter AG has disclosed six vulnerabilities in the embedded firmware of its modulo...
Latest news

Kaspersky researchers have uncovered new details about PassiveNeuron, a long-running cyberespionage campaign targeting government, financial, and industrial...

Researchers at Palo Alto Networks’ Unit 42 have observed a surge in activity from Scattered LAPSUS$ Hunters...

Industrial automation giant ABB has disclosed a critical missing authentication vulnerability (CVE-2025-9574) affecting its ALS-mini-S4/S8 IP intelligent...

China-based cybersecurity firm Qianxin Threat Intelligence Center has uncovered a new wave of attacks linked to the...

Google’s Threat Intelligence Group (GTIG) has uncovered a major post-exposure evolution in the operations of COLDRIVER—a Russian...

Security researcher Jordan Jay has published an extensive technical breakdown of CVE-2025-24990, a high-severity Elevation of Privilege...

The WSO2 project has released urgent security advisories addressing two critical access control vulnerabilities—CVE-2025-9804 and CVE-2025-10611—that affect...

 cybernewswire
Wilmington, Delaware, 21st October 2025, CyberNewsWire

Computers are essential tools in both personal and professional life, handling everything from work and communication to...

Armed with a diverse arsenal of malware, including the notorious AppleSeed and AlphaSeed strains, Kimsuky's tactics have evolved
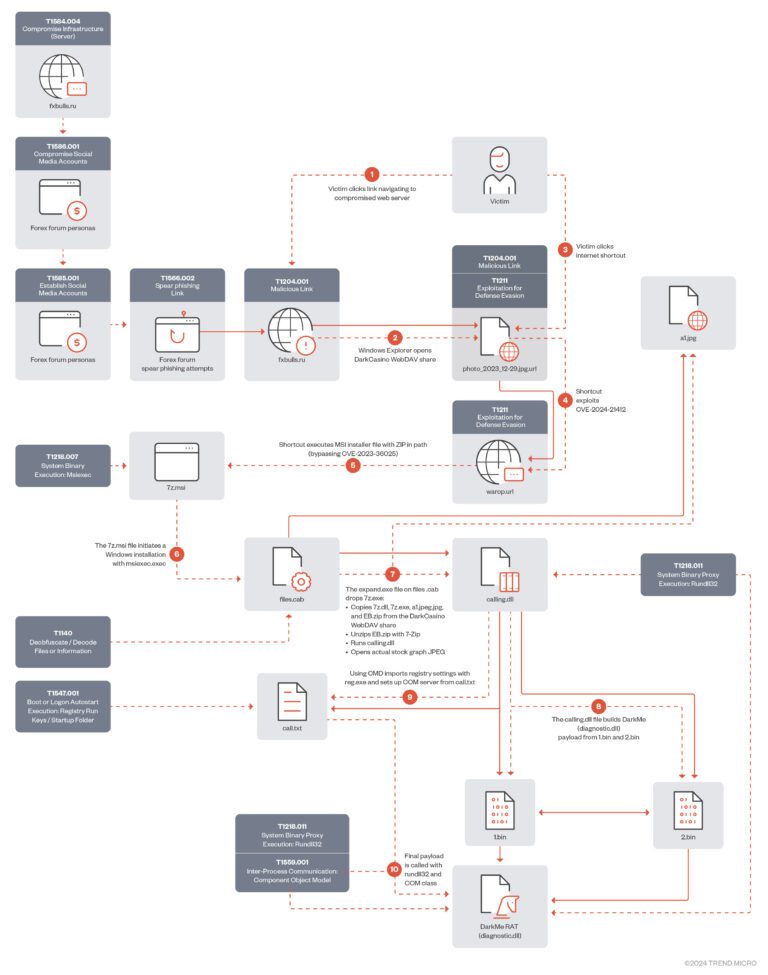
This flaw, exploited by Water Hydra, served as a linchpin in a complex 0-day attack chain, leading to a bypass of Defender SmartScreen

One notable aspect of CharmingCypress's tactics is their use of unusual social-engineering tactics in their phishing campaigns

two of these were 'zero-days' (CVE-2024-21351 and CVE-2024-21412), meaning hackers have already been exploiting them in the wild!
CVE-2024-24691 (CVSS score 9.6) could allow hackers to escalate their privileges, potentially gaining control of vulnerable systems
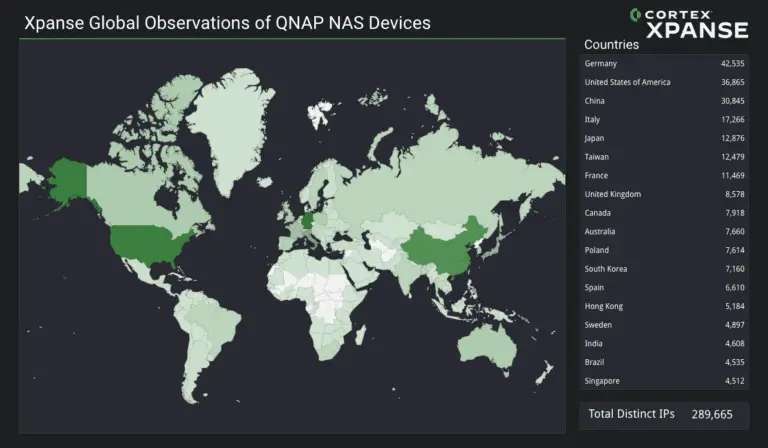
A severe zero-day vulnerability (CVE-2023-50358) has been discovered in QNAP Network Attached Storage (NAS) devices

Bumblebee malware, known for its complexity and versatility, was initially a favored payload by cybercriminals from its inception

The second "Hot News" patch targets a serious flaw (CVE-2024-22131, CVSS score 9.1) in the SAP Application Basis (ABA) layer

Industrial control systems (ICS) silently orchestrate the vital processes behind our modern world. These intricate networks of...

Introduction In today’s world of online applications, it’s important to keep our sensitive information safe, follow the...

Pikabot employs an arsenal of anti-analysis techniques, including string obfuscation, insertion of junk instructions, and anti-debug methods.
CVE-2024-25108 reveals that authorization checks within Pixelfed were insufficiently stringent, granting attackers unauthorized access

A formidable malware known as Glupteba has been lurking, evolving, and spreading its tentacles across the globe
CISA has sounded the alarm on a significant 'actively exploited' flaw in Roundcube Webmail (CVE-2023-43770)

Introduction In today’s digital age, more and more data is moving to the cloud. From personal photos...

Two disclosed critical vulnerabilities (CVE-2024-25106 and CVE-2024-24830) expose users to a dangerous combination of unauthorized access

Arctic Wolf Labs uncovered threat actors are leveraging CVE-2023-22527 to deploy C3RB3R ransomware alongside a suite of other malicious payloads
A recently discovered security bug in ExpressVPN's Windows software, tracked as CVE-2024-25728, has forced the popular VPN provider

This vulnerability, designated CVE-2024-0985 (CVSS 8.0), could allow attackers to execute malicious code with elevated privileges

Electron team has stepped forward to challenge these assertions, shedding light on the intricacies of the vulnerabilities

A PoC exploit code and technical details have been made available for a zero-day flaw, tracked as CVE-2022-4262, affecting Google Chrome

one of the internet giants, Namecheap has been hit by a series of DDoS attacks that threaten to disrupt its operations.