
 Do Son
Samsung has announced that it will host a new product unveiling event titled “Worlds Wide Open” on...
Latest news

Siemens has released a critical security update for its SIMATIC ET 200SP communication processors, addressing an authentication...

Apple’s Senior Vice President of Worldwide Marketing, Greg Joswiak, recently hinted at the arrival of a new...

In an effort to avoid multibillion-dollar fines for violating the EU Digital Markets Act (DMA), Google is...

As artificial intelligence continues its rapid expansion, OpenAI has announced the formation of a new advisory body...

Rockwell Automation has published a new security advisory warning customers about three vulnerabilities affecting its 1783-NATR Network...

Veeam Software has released patches addressing three newly disclosed vulnerabilities, including two critical Remote Code Execution (RCE)...
DOJ Files Record $15 Billion Bitcoin Seizure Against Prince Group Chairman Over Pig Butchering Scams

DOJ Files Record $15 Billion Bitcoin Seizure Against Prince Group Chairman Over Pig Butchering Scams
The U.S. Department of Justice (DOJ) has unsealed an indictment against Chen Zhi, also known as Vincent,...

A new report from Cyble Research and Intelligence Labs (CRIL) has uncovered a sophisticated Android malware campaign...

Google has released a new Stable Channel Update for Desktop, rolling out gradually to Windows, macOS, and...

The AhnLab Security Intelligence Center has uncovered that the LockBit ransomware is being spread through malicious Word files

A critical flaw, CVE-2024-22406 with a CVSS score of 9.3, poses a serious threat to businesses relying on this popular open-source platform

Remcos RAT malware communicates with a remote IP address and initiates malicious activities, including keylogging and capturing screenshots

Mint Sandstorm campaign's modus operandi includes innovative post-intrusion techniques, such as deploying a custom backdoor named MediaPl

Siemens fixes two critical vulnerabilities (CVE-2023-51438 and CVE-2023-49621) in their SIMATIC IPC and SIMATIC NC 4100 products

Atlantida stealer is not only adept at capturing entire screen contents but also targets specific data sources.

Kaspersky has released an open-source script, iShutdown, designed for rapid detection of spyware infections in iOS devices.

tracked as CVE-2018-15133 (CVSS score: 8.1), the vulnerability has been described as a deserialization of untrusted data vulnerability

Citrix has sounded an alarm for its customers regarding two critical zero-day vulnerabilities, CVE-2023-6548 and CVE-2023-6549

Nassim Asrir has released the details, and a proof-of-concept (PoC) exploit for a high-severity vulnerability, CVE-2023-6546

This year witnessed the alarming rise of mega ransomware attacks, characterized by their extensive scale and impact.

The crux of the LeftoverLocals vulnerability (CVE-2023-4969) lies in the inadequate isolation of process memory in GPGPU platforms.
In a move that underscores the seriousness of the threat, Google confirmed that an exploit for CVE-2024-0519 is already prowling in the wild

Recently, two vulnerabilities were found in the Linux kernel that pose significant security threats: CVE-2024-0562 and CVE-2024-0565.

The recent discovery of CVE-2023-34063, a critical vulnerability with a CVSS score of 9.9, allows attackers to gain remote execution.

CVE-2023-22527 vulnerability, with a CVSS score of 10, signifies the highest level of severity in the realm of cybersecurity threats.

CherryPie, another stealthy infiltrator, exemplifies the cross-platform threat. Despite being caught by Apple, many static engines lag in detection

CVE-2023-4001 is an authentication bypass flaw in GRUB. GRUB is the gatekeeper of the booting process in many UEFI-based computers

The report by Forescout Vedere Labs provides a comprehensive analysis of two separate attack waves on Denmark's energy infrastructure

CVE-2023-31029 and CVE-2023-31030 (CVSS 9.3): Both of these vulnerabilities exist in the NVIDIA DGX A100's baseboard management controller

Adding to the severity, Michael Maltsev released a Proof-of-Concept (PoC) code, demonstrating the practical application of CVE-2023-36003
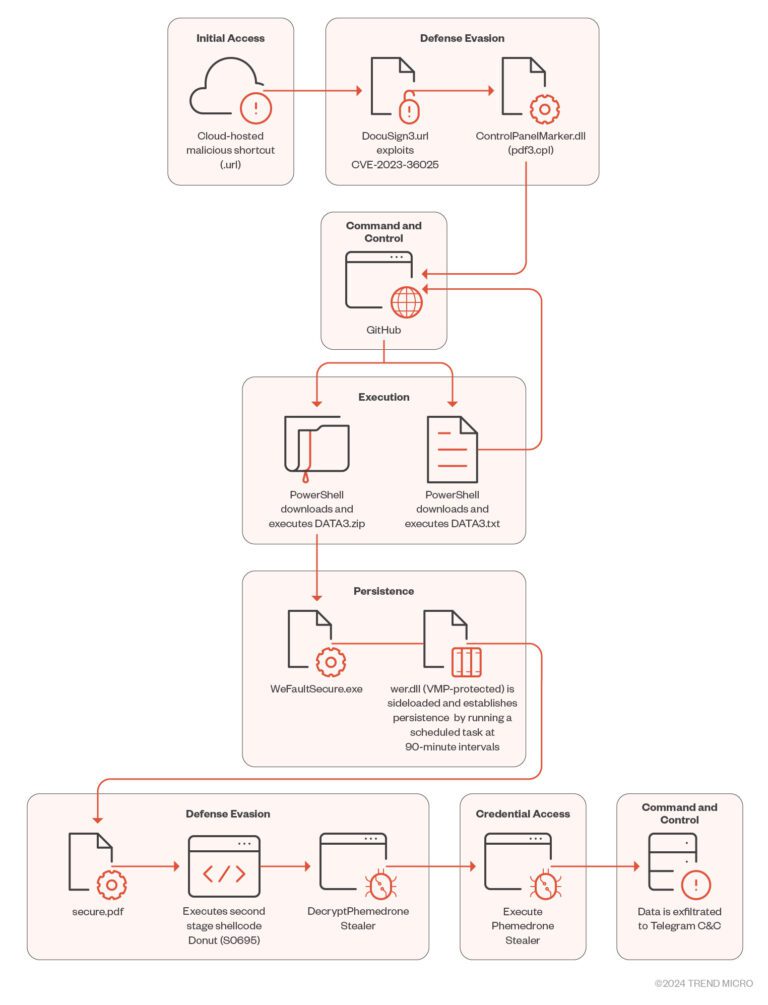
Phemedrone Stealer's infection chain begins with the hosting of malicious Internet Shortcut files on platforms like Discord or cloud services