
 Do Son
Researchers at Kaspersky’s Global Research and Analysis Team (GReAT) have published a detailed report on a newly...
Latest news

A newly released report from ReliaQuest reveals how the China-backed advanced persistent threat (APT) group “Flax Typhoon”...

 cybernewswire
New York, United States, 15th October 2025, CyberNewsWire

New York, USA, New York, 15th October 2025, CyberNewsWire

Samsung has announced that it will host a new product unveiling event titled “Worlds Wide Open” on...

Siemens has released a critical security update for its SIMATIC ET 200SP communication processors, addressing an authentication...

Apple’s Senior Vice President of Worldwide Marketing, Greg Joswiak, recently hinted at the arrival of a new...

In an effort to avoid multibillion-dollar fines for violating the EU Digital Markets Act (DMA), Google is...

As artificial intelligence continues its rapid expansion, OpenAI has announced the formation of a new advisory body...

Rockwell Automation has published a new security advisory warning customers about three vulnerabilities affecting its 1783-NATR Network...

Citrix has sounded an alarm for its customers regarding two critical zero-day vulnerabilities, CVE-2023-6548 and CVE-2023-6549

Nassim Asrir has released the details, and a proof-of-concept (PoC) exploit for a high-severity vulnerability, CVE-2023-6546

This year witnessed the alarming rise of mega ransomware attacks, characterized by their extensive scale and impact.

The crux of the LeftoverLocals vulnerability (CVE-2023-4969) lies in the inadequate isolation of process memory in GPGPU platforms.
In a move that underscores the seriousness of the threat, Google confirmed that an exploit for CVE-2024-0519 is already prowling in the wild

Recently, two vulnerabilities were found in the Linux kernel that pose significant security threats: CVE-2024-0562 and CVE-2024-0565.

The recent discovery of CVE-2023-34063, a critical vulnerability with a CVSS score of 9.9, allows attackers to gain remote execution.

CVE-2023-22527 vulnerability, with a CVSS score of 10, signifies the highest level of severity in the realm of cybersecurity threats.

CherryPie, another stealthy infiltrator, exemplifies the cross-platform threat. Despite being caught by Apple, many static engines lag in detection

CVE-2023-4001 is an authentication bypass flaw in GRUB. GRUB is the gatekeeper of the booting process in many UEFI-based computers

The report by Forescout Vedere Labs provides a comprehensive analysis of two separate attack waves on Denmark's energy infrastructure

CVE-2023-31029 and CVE-2023-31030 (CVSS 9.3): Both of these vulnerabilities exist in the NVIDIA DGX A100's baseboard management controller

Adding to the severity, Michael Maltsev released a Proof-of-Concept (PoC) code, demonstrating the practical application of CVE-2023-36003
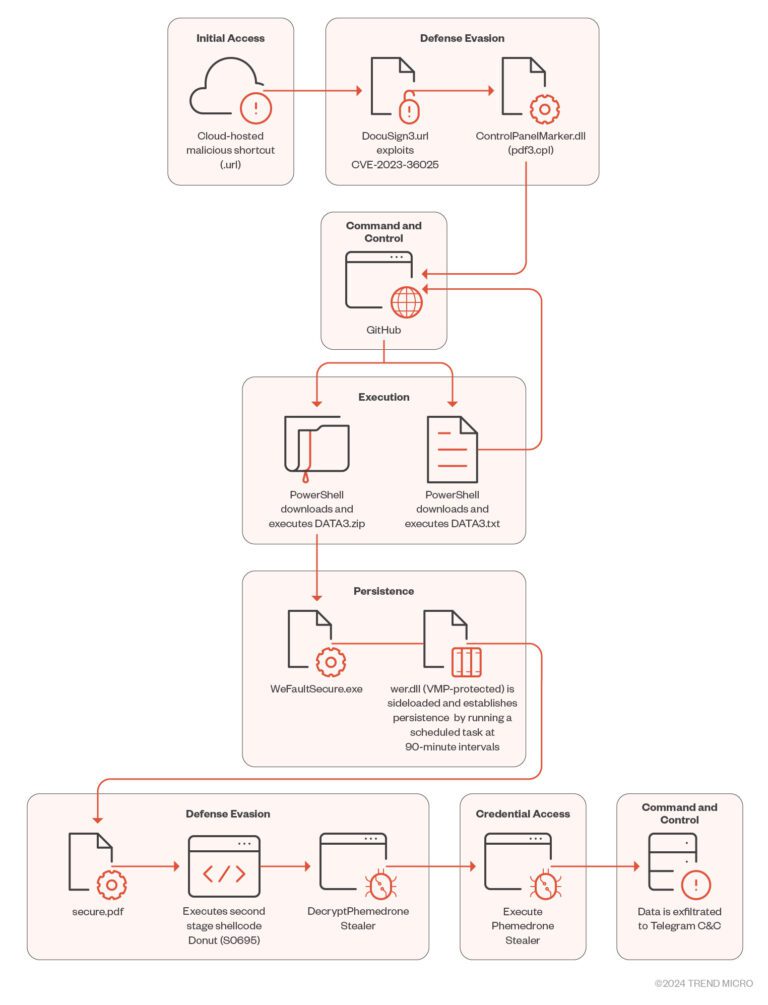
Phemedrone Stealer's infection chain begins with the hosting of malicious Internet Shortcut files on platforms like Discord or cloud services

A new predator lurks, targeting unsuspecting Chinese users through a sophisticated Financial Fraud APK campaign.

Valentin-Metz unveiled a critical buffer overflow vulnerability in Factorio. This flaw, lurking within the game's custom-engine C++ code

A deceptive package called 'sellpass-sdk' in PyPI, which turned out to be a distributor of the "Blank Grabber" infostealer malware

Details and proof-of-concept (PoC) exploit code have emerged about a now-patched security flaw, CVE-2024-20656, in Microsoft Visual Studio
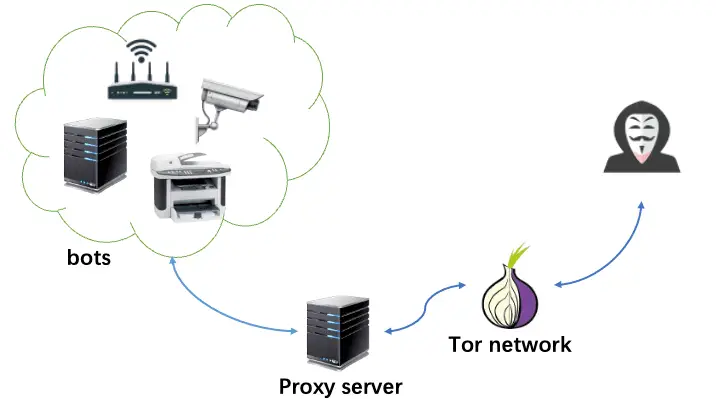
Rimasuta botnet is designed to infiltrate systems and evade detection. It employs advanced data encryption and communication techniques

CVE-2023-50290 is a security flaw that allows unauthorized read access to the host environment of Apache Solr instances
The Beijing Office of Justice said it had found a way to bypass AirDrop's encryption, allowing it to see the content and source of data transfers.

Sebastien Raoult, 22, a citizen of Epinal, France, was arrested in Morocco in 2022 and extradited to the United States in 2023.