
 Do Son
DomainTools Threat Intelligence has exposed a sprawling cybercrime operation that uses a single infrastructure to power multiple...
Latest news

Between July and August 2025, global security teams have observed a resurgence in Akira ransomware incidents targeting...

Apple has announced a major overhaul of its Security Bounty vulnerability reward program, set to take effect...

The UK Competition and Markets Authority (CMA) has formally designated Google as holding a “Strategic Market Status”...

A critical-severity vulnerability has been disclosed in Happy DOM, a popular JavaScript package used to emulate web...

The Zero Day Initiative (ZDI) has published details of two critical vulnerabilities in the popular open-source compression...

The Socket Threat Research Team has sounded the alarm on an escalating wave of malicious npm activity...
China’s State Administration for Market Regulation (SAMR) recently announced the launch of an antitrust investigation into U.S....

OpenAI’s newly launched short-video platform “Sora,” which enables users to generate audiovisual content directly through AI, has...
Microsoft Finally Fixes Windows 11 Bug Causing PCs to Auto-Restart Instead of ‘Update and Shut Down’

Microsoft Finally Fixes Windows 11 Bug Causing PCs to Auto-Restart Instead of ‘Update and Shut Down’
Windows 11 users are likely familiar with the system’s habit of prompting a restart after automatically installing...

Proof-of-concept (PoC) exploit code has been published for a Windows kernel vulnerability tracked as CVE-2023-36424.

A new predator lurks - sophisticated threat actors using malicious JavaScript to steal sensitive information

In an era where mobile banking has become the norm, a new threat looms large, especially in India's banking sector - Android phishing.

One of the most alarming aspects of CVE-2023-7024 is that it had been actively exploited in the wild before its discovery.

Identified as CVE-2023-48738 and rated 9.3 on the CVSS scale, this vulnerability was a ticking time bomb in the Porto theme's code.

Magecart, the perpetual phantom haunting e-commerce, continued its reign of terror by exploiting unpatched websites to steal credit card data

a malicious software distribution campaign they uncovered, which uses JavaScript web injections to steal banking data from 40 banks

Neurosurgical Associates of New Jersey announced a security breach wherein an unauthorized malicious actor accessed the email of one of the employees

A staggering 26,447 vulnerabilities were disclosed in 2023, surpassing 2022's total by over 1,500 CVEs.

The discovery of CVE-2023-50917 serves as a stark reminder of the importance of cybersecurity in the realm of smart home automation

In light of a CVE-2023-50164 vulnerability discovered in Apache Struts, Cisco Systems has elucidated the impact on its products.

Unauthenticated attackers can exploit the CVE-2023-6750 (CVSS 9.8) flaw to download database backups made with the plugin.

Tagged as CVE-2023-43826 (CVSS score of 7.5), this security flaw in Apache Guacamole represents a significant threat

The U.S. Department of Justice has announced the FBI's successful infiltration into the infrastructure of the ransomware group ALPHV

Interpol announced that the international law enforcement operation "Operation HAECHI IV," aimed at combating financial crimes online

The Konni group leveraged LNK files, essentially commonplace Windows shortcuts increasingly used by various threat actors,

CVE-2023-49734 vulnerability allows a lower-privileged user, or 'Gamma user,' to gain undue control over chart permissions.
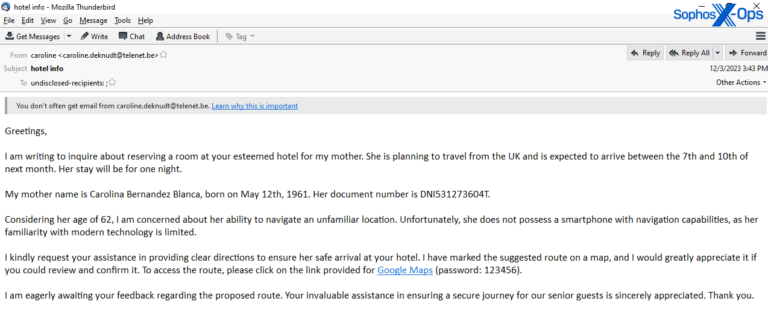
Sophos X-Ops warns that the "Inhospitality" malspam campaign represents a cunning blend of social engineering and malware

the Iranian espionage group Seedworm (also known as Muddywater) has emerged as a sophisticated and elusive adversary

GitHub Gists Abuse: This technique involves using GitHub Gists, a feature for sharing code snippets, to host two-stage malicious payloads.

The Smishing Triad Gang's ability to adapt and refine its tactics poses a significant challenge to cybersecurity efforts globally.

The leak includes files of prototypes and beta versions of applications and games released through TestFlight