
 Do Son
The Akka.NET team has issued a critical security advisory for a severe vulnerability in its Akka.Remote module...
Latest news

Shopping for a smartphone on a budget presents two main options: refurbished devices and used phones. While...

 cybernewswire
Tel Aviv, Israel, 8th October 2025, CyberNewsWire

Microsoft has confirmed that in the consumer editions of Windows 11 — including Home and Pro —...

Google has unveiled a preview of its next-generation AI model, Gemini 2.5 Computer Use, a system that...

In response to Google’s recent request to postpone enforcement of the injunction and seek a comprehensive review,...

Qualcomm has announced its acquisition of Arduino, the globally renowned open-source hardware and software platform — a...

Microsoft continues to advance its renewable energy transition in Japan, having recently confirmed the signing of three...

Meta has announced its investment in the construction of a new submarine cable system, “Candle,” which will...

Once the defining name in note-taking applications, Evernote had seen its presence wane in recent years. Yet...

CVE-2023-6448 allows unauthenticated attackers with network access to take complete control of the PLC and manipulate critical infrastructure functions

In the intricate web of modern computing, a new threat has emerged, casting a shadow over the...

While WordPress Core currently does not have any known object injection vulnerabilities, they are rampant in other plugins and themes.

SpyLoan apps often mimic legitimate loan services in wording and design, making it difficult for users to discern their authenticity.

Kaspersky researchers have identified several cracked applications disseminated through unofficial channels, harboring a Trojan-Proxy.

In the dynamic realm of eCommerce, Magento stands as a titan, offering robust functionalities that cater to...

SLAM emerges from the intersection of hardware features intended for memory efficiency and the notorious Spectre vulnerabilities

In the dynamic world of machine learning (ML), where innovation and efficiency are paramount, a new challenge...
A critical Remote Code Execution (RCE) vulnerability, tracked as CVE-2023-22523 (CVSS score of 9.8), has been discovered in Assets Discovery

A critical Remote Code Execution (RCE) vulnerability, tracked as CVE-2023-22522, has been discovered in Confluence Data Center and Server

Teal Kurma primarily targets government, telecommunication, and IT service providers, sectors rich in high-value information

CVE-2023-43121 allows unauthenticated users to read root files, thereby exposing password hashes for the device
CVE-2023-33063 vulnerability arises from memory corruption in DSP Services during a remote call from the High-Level Operating System (HLOS)

2023 witnessed a significant shift in the tactics and approaches of cyber attackers, influenced by global conflicts and advancements in technology

Identified as CVE-2023-26360, this flaw has been exploited by threat actors for initial access to government servers, as confirmed by CISA
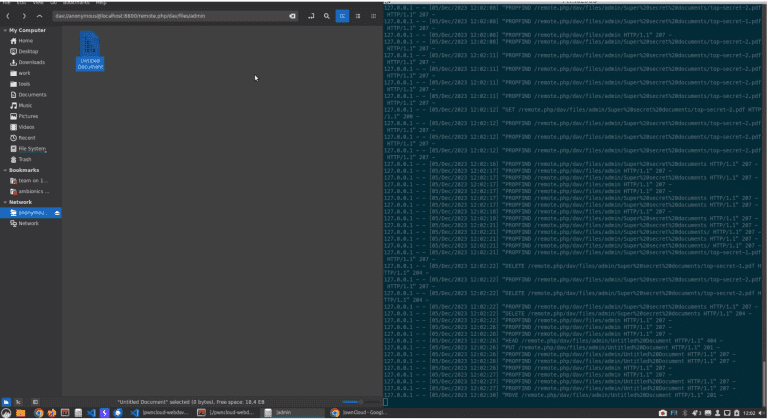
CVE-2023-49105 affecting ownCloud versions 10.6.0 to 10.13.0 has been made public, and a PoC exploit code is readily available

A new chapter unfolds with the discovery of a novel and menacing Trojan targeting macOS users – the BlueNoroff loader.
CVE-2023-6269 (CVSS: 10): Unpatched Vulnerability Leaves Atos Unify OpenScape at Risk of Root Access
CVE-2023-6269 (CVSS: 10): Unpatched Vulnerability Leaves Atos Unify OpenScape at Risk of Root Access
Rated with a CVSS3.1 Base score of 10 (critical), the CVE-2023-6269 vulnerability underscores the severity and potential impact

Over 1,500 HuggingFace API Tokens were left exposed, putting millions of users of Meta-Llama, Bloom, and Pythia at risk

Vladimir Dunaev, a 40-year-old Russian national from Amur Blast, pleaded guilty to his involvement in Trickbot malware. Learn about this notorious malware and its impact on American entities in this blog post.

By exploiting the CVE-2023-49070 vulnerability, an attacker can execute arbitrary code on the affected Apache OFBiz server

Protect your business from the powerful cyber threats of state-sponsored Russian group, Forest Blizzard. As Microsoft tracks their exploits, uncover the group's tactics & targets to secure your data.