
 Do Son
Qualcomm has announced its acquisition of Arduino, the globally renowned open-source hardware and software platform — a...
Latest news

Microsoft continues to advance its renewable energy transition in Japan, having recently confirmed the signing of three...

Meta has announced its investment in the construction of a new submarine cable system, “Candle,” which will...

Once the defining name in note-taking applications, Evernote had seen its presence wane in recent years. Yet...

Amazon Web Services (AWS) has released an important security bulletin warning users of a critical local privilege...

Security researchers have identified two critical vulnerabilities in Nagios Log Server, the enterprise log management solution widely...
A cross-site scripting (XSS) vulnerability in Synacor Zimbra Collaboration Suite (ZCS) — tracked as CVE-2025-27915 — has...

Security researcher David Leadbeater has disclosed a vulnerability in OpenSSH, identified as CVE-2025-61984, which highlights how even...

Google has released a new Stable Channel update for Chrome 141.0.7390.65/.66 on Windows and macOS and 141.0.7390.65...

A new phishing campaign analyzed by malware researcher 0x0d4y has uncovered fresh insights into Mustang Panda’s evolving...

A North Korean hacking organization known as Andariel has been wreaking havoc in the digital realm, stealthily infiltrating South Korean firms

The Bluesky ransomware was unleashed about 30 minutes post initial breach. Its deployment was chillingly efficient

Papercut privilege escalation security vulnerability still doesn't seem to be fixed on the current version (23.0.3)

The report, covering June to August 2023, documents over 3.3 million cyberattacks, equating to about 26 attacks per minute.

AeroBlade first came into the spotlight in September 2022, revealing a meticulously planned cyber espionage campaign.
CVE-2023-40626 stems from an issue in the language file parsing process, which could be manipulated to disclose environment variables.

It warns of a remote code execution vulnerability on the user's site, citing the non-existent CVE-2023-45124.

Marketing is a lively and tough field in business. It needs new ideas and imagination to get...
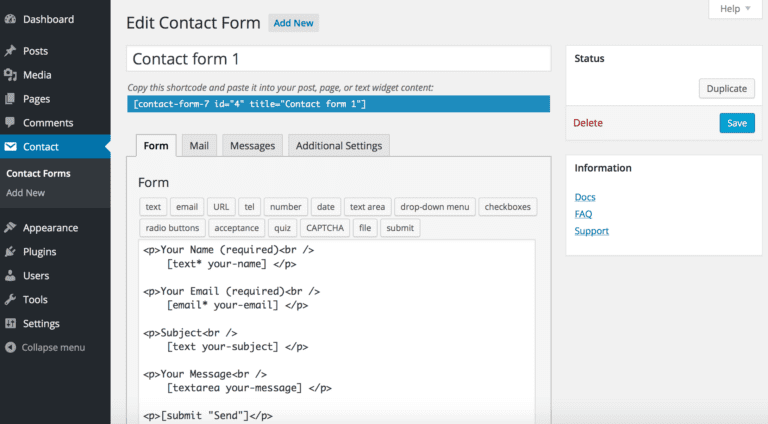
Contact Form 7, a popular WordPress plugin with over 5 million installations, has been found to harbor a vulnerability (CVE-2023-6449)

Researchers from Unit 42 at Palo Alto Networks have uncovered a new toolset being used in cyber attacks against organizations

A critical risk has surfaced within Google Workspace's Domain-Wide Delegation feature, as revealed by Unit 42 researchers at PaloAlto Networks

SugarGh0st is a customized variant of the infamous Gh0st RAT, which has been active for over a decade. Developed by a Chinese group

LogoFAIL vulnerabilities are not vendor-specific and impact devices and chips from a wide range of manufacturers, affecting UEFI firmware

APT29 orchestrated a malicious campaign employing counterfeit BMW advertisements, the Ngrok tool, and exploiting a vulnerability in WinRAR

Promon has uncovered a novel Android malware dubbed FjordPhantom, which employs a unique virtualization tactic to evade detection

Cybercrime in Iran continues to escalate, posing a significant threat to the financial security of local citizens....

Former Motorola technical specialist, admitted to attempting to fraudulently obtain a passport while awaiting trial for a cyberattack on his former employer

Ukrainian citizen Vitalii Chychasov, aged 37, was sentenced to eight years of imprisonment in the United States for establishing
This issue stemmed from a susceptibility to cross-site scripting (XSS) via shortcodes (CVE-2023-48321, CVSS: 6.5).

North Korean cyber criminals have weaponized their skills to become the world's most proficient cryptocurrency thieves

A striking example of this evolution is the use of WebSockets in credit card skimming attacks, a method that is both sophisticated

CVE-2023-42916: An out-of-bounds read vulnerability could allow attackers to read sensitive information from the affected device's memory