Skip to content
September 16, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Sovereign Ascent: Anthropic Deploys Flagship Fable 5 Architecture Anthropic Fable 5 model
  • Technology

Sovereign Ascent: Anthropic Deploys Flagship Fable 5 Architecture

Do Son June 10, 2026 0
Read More Read more about Sovereign Ascent: Anthropic Deploys Flagship Fable 5 Architecture
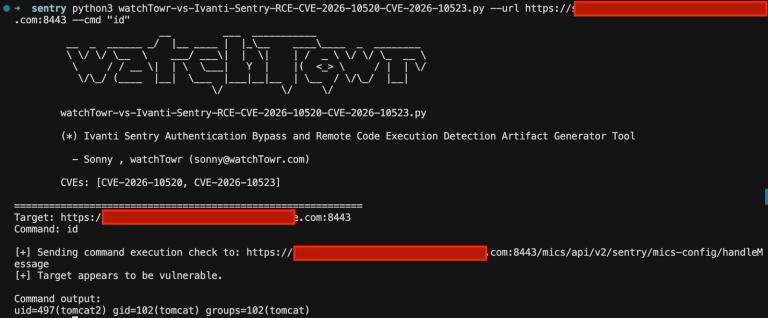
Ivanti Sentry RCE: Publicly Disclosed PoC for CVSS 10 Ivanti Sentry RCE publicly disclosed PoC
  • Vulnerability Report

Ivanti Sentry RCE: Publicly Disclosed PoC for CVSS 10

Do Son June 10, 2026 0
Read More Read more about Ivanti Sentry RCE: Publicly Disclosed PoC for CVSS 10
OpenSSL Security Patches Fix Remote Code Execution Risk CVE-2022-3602 OpenSSL security patches remote code execution risk
  • Vulnerability Report

OpenSSL Security Patches Fix Remote Code Execution Risk

Do Son June 10, 2026 0
Read More Read more about OpenSSL Security Patches Fix Remote Code Execution Risk
New Microsoft Defender Zero Day Exploit Released Publicly Online Defender zero day exploit race condition vulnerability
  • Vulnerability Report

New Microsoft Defender Zero Day Exploit Released Publicly Online

Do Son June 10, 2026 0
Read More Read more about New Microsoft Defender Zero Day Exploit Released Publicly Online
CISA Expands Active Exploit Catalog with Cisco, Arista, and Chromium Flaws CISA active exploit catalog known exploited vulnerabilities ActiveMQ RCE CVE-2026-34197 CISA KEV Catalog Actively Exploited Vulnerabilities CISA KEV Catalog CVE-2025-37164 GeoServer XXE, CISA KEV FortiWeb SQLi, CISA KEV Critical Vulnerabilities CVE-2024-20953
  • Vulnerability Report

CISA Expands Active Exploit Catalog with Cisco, Arista, and Chromium Flaws

Do Son June 10, 2026 0
Read More Read more about CISA Expands Active Exploit Catalog with Cisco, Arista, and Chromium Flaws
Microsoft Patch Tuesday Fixes Address Critical Zero-Day Flaws Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability Report

Microsoft Patch Tuesday Fixes Address Critical Zero-Day Flaws

Do Son June 10, 2026 0
Read More Read more about Microsoft Patch Tuesday Fixes Address Critical Zero-Day Flaws
High-Severity Vulnerabilities Addressed in Endpoint Manager Mobile Ivanti EPMM security updates Ivanti ITSM vulnerability authenticated privilege escalation Ivanti Xtraction vulnerability CVE-2026-8043 Ivanti EPM RCE, SQL Injection Ivanti EPM, remote code execution CVE-2024-50330 - CVE-2025-0282 and CVE-2025-0283
  • Vulnerability Report

High-Severity Vulnerabilities Addressed in Endpoint Manager Mobile

Do Son June 10, 2026 0
Read More Read more about High-Severity Vulnerabilities Addressed in Endpoint Manager Mobile
Critical Rclone Command Execution Bug Threatens Cloud Environments rclone command execution execute local commands Rclone RCE CVE-2026-41176
  • Vulnerability Report

Critical Rclone Command Execution Bug Threatens Cloud Environments

Do Son June 10, 2026 0
Read More Read more about Critical Rclone Command Execution Bug Threatens Cloud Environments
Critical Veeam Backup Vulnerability Exposed Veeam Backup vulnerability remote code execution Veeam Backup vulnerability Veeam Vulnerabilities CVE-2024-42448 & CVE-2024-42449
  • Vulnerability Report

Critical Veeam Backup Vulnerability Exposed

Do Son June 10, 2026 0
Read More Read more about Critical Veeam Backup Vulnerability Exposed
Critical FortiSandbox Flaw Requires Immediate Patching CVE-2026-25089 CVE-2023-45590
  • Vulnerability Report

Critical FortiSandbox Flaw Requires Immediate Patching

Do Son June 10, 2026 0
Read More Read more about Critical FortiSandbox Flaw Requires Immediate Patching
Critical TinyMCE Cross Site Scripting Flaws Threaten Millions of Applications TinyMCE cross site scripting stored XSS vulnerability
  • Vulnerability Report

Critical TinyMCE Cross Site Scripting Flaws Threaten Millions of Applications

Do Son June 10, 2026 0
Read More Read more about Critical TinyMCE Cross Site Scripting Flaws Threaten Millions of Applications
MBS Universal Gateway Flaws Threaten Building Automation Networks Haskell TLS vulnerability CVE-2026-9648, X.509 NameConstraints, crypton-x509-validation MBS Universal Gateway flaws stack buffer overflow bugs SystemLink authentication bypass privilege escalation bug Cache Warmer RCE flaw Magento PHP object injection
  • Vulnerability Report

MBS Universal Gateway Flaws Threaten Building Automation Networks

Do Son June 10, 2026 0
Read More Read more about MBS Universal Gateway Flaws Threaten Building Automation Networks
Spring Framework Security Vulnerabilities Addressed in Critical Maintenance Updates Spring framework security vulnerabilities authentication bypass threat
  • Vulnerability Report

Spring Framework Security Vulnerabilities Addressed in Critical Maintenance Updates

Do Son June 9, 2026 0
Read More Read more about Spring Framework Security Vulnerabilities Addressed in Critical Maintenance Updates
New MagicAd Android Trojan Bypasses OS Restrictions to Flood Devices with Ads MagicAd Android trojan GetApps malware distribution
  • Malware

New MagicAd Android Trojan Bypasses OS Restrictions to Flood Devices with Ads

Do Son June 9, 2026 0
Read More Read more about New MagicAd Android Trojan Bypasses OS Restrictions to Flood Devices with Ads
Strategic Value: Google Slashes AI Plus Subscription Fees While Doubling Storage Google AI Plus subscription
  • Technology

Strategic Value: Google Slashes AI Plus Subscription Fees While Doubling Storage

Do Son June 9, 2026 0
Read More Read more about Strategic Value: Google Slashes AI Plus Subscription Fees While Doubling Storage
Decentralized Diffusion: Z-Library Upgrades Mirror Infrastructure to Evade Seizures Z-Library mirror network
  • Technology

Decentralized Diffusion: Z-Library Upgrades Mirror Infrastructure to Evade Seizures

Do Son June 9, 2026 0
Read More Read more about Decentralized Diffusion: Z-Library Upgrades Mirror Infrastructure to Evade Seizures
Structured Expiration: Microsoft Enforces Comprehensive Lifecycle Management for OneDrive OneDrive data retention policy
  • Technology

Structured Expiration: Microsoft Enforces Comprehensive Lifecycle Management for OneDrive

Do Son June 9, 2026 0
Read More Read more about Structured Expiration: Microsoft Enforces Comprehensive Lifecycle Management for OneDrive
Malicious Traffic Routing Stack Exploited to Spread Global Malware malicious traffic routing Check Point research report
  • Malware

Malicious Traffic Routing Stack Exploited to Spread Global Malware

Do Son June 9, 2026 0
Read More Read more about Malicious Traffic Routing Stack Exploited to Spread Global Malware
Argamal Trojan Campaign Targets Adult Gamers with COM Hijacking Argamal Trojan campaign Kaspersky malware analysis
  • Malware

Argamal Trojan Campaign Targets Adult Gamers with COM Hijacking

Do Son June 9, 2026 0
Read More Read more about Argamal Trojan Campaign Targets Adult Gamers with COM Hijacking
SAP Security Patch Day: Critical Security Vulnerabilities Remediated SAP security patch day critical security vulnerabilities SAP SQL Injection April 2026 Patch Day SAP Security, Critical Vulnerabilities Security Patch Day CVE-2025-42944
  • Vulnerability Report

SAP Security Patch Day: Critical Security Vulnerabilities Remediated

Do Son June 9, 2026 0
Read More Read more about SAP Security Patch Day: Critical Security Vulnerabilities Remediated
Sophisticated TA4922 Cybercrime Operations Expand Globally Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cybercriminals

Sophisticated TA4922 Cybercrime Operations Expand Globally

Do Son June 9, 2026 0
Read More Read more about Sophisticated TA4922 Cybercrime Operations Expand Globally
Seamless Interoperability: Apple Notes Optimizes Markdown Integration in iOS 27 Apple Notes Markdown support
  • Technology

Seamless Interoperability: Apple Notes Optimizes Markdown Integration in iOS 27

Do Son June 9, 2026 0
Read More Read more about Seamless Interoperability: Apple Notes Optimizes Markdown Integration in iOS 27
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-87827CVSS 10.0
    Certain KGUARD DVR devices running vulnerable firmware expose a system command execution service on all network interfaces without...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-78006CVSS 9.8
    The The Events Calendar plugin for WordPress is vulnerable to Remote Code Execution in all versions up to,...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-39364
    Vite is a frontend tooling framework for JavaScript. From 7.1.0 to before 7.3.2 and 8.0.5, on the Vite...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-27540CVSS 9.0
    Unrestricted Upload of File with Dangerous Type vulnerability in Rymera Web Co Pty Ltd. Woocommerce Wholesale Lead Capture...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-76461CVSS 9.8
    A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco Secure Email Gateway could allow an...
    CISA KEV📅 Added to KEV: Sep 14, 2026
  • CVE-2026-51990
    A critical remote code execution vulnerability in Sogou Input Method, one of the most widely used Chinese-language input...
    Admin intel📅 Updated: Sep 12, 2026
  • CVE-2026-85706CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, an unauthenticated user could have read arbitrary files from...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
  • CVE-2026-42016CVSS 8.1
    JFrog Artifactory (Self Hosted) versions before 7.133.11 are vulnerable to a privilege escalation attack due to a validation...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
Powered by CVE Watchtower

🔴 Live Critical Threats

  • CVE-2026-73807CVSS 9.8
    The mySCADA myPRO Manager command API does not properly enforce authentication for...
  • CVE-2026-81855CVSS 9.1
    A hardcoded cryptographic client authentication key vulnerability exists in the robot testing...
  • CVE-2026-78225CVSS 9.0
    A hardcoded cryptographic server key vulnerability exists in the deployer-ng Update Controller...
  • CVE-2026-61560CVSS 9.8
    `@zereight/mcp-gitlab` is a Model Context Protocol server for GitLab. Prior to version...
  • CVE-2026-73437CVSS 9.6
    On affected platforms running Arista EOS with Dynamic Host Configuration Protocol (DHCP)...
  • CVE-2026-61559CVSS 9.6
    `@zereight/mcp-gitlab` is a Model Context Protocol server for GitLab. Starting in version...
  • CVE-2026-91939CVSS 9.8
    Cotonti 1.0.0 Comments plugin passes the ci GET parameter to unserialize() without...
  • CVE-2026-61568CVSS 9.6
    `@zereight/mcp-gitlab` is a Model Context Protocol server for GitLab. Versions prior to...
  • CVE-2026-66887CVSS 9.6
    The affected products are missing authorization on state-changing CGIs and session checks...
  • CVE-2026-66890CVSS 9.6
    The affected products use hard-coded credentials, which could allow remote access to...
Powered by CVE WATCHTOWER

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.