Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
OpenMatter Network Introduces Verifiable Trust Layer for Secure Collaboration and AI Agents Untitled_17_x_9_in_1782765623hTY1a9UzBA
  • Press Release

OpenMatter Network Introduces Verifiable Trust Layer for Secure Collaboration and AI Agents

cybernewswire June 30, 2026 0
Melbourne, Florida, June 30th, 2026, CyberNewswire OpenMatter Network today announced the launch of its cryptographically verifiable platform for...
Read More Read more about OpenMatter Network Introduces Verifiable Trust Layer for Secure Collaboration and AI Agents
AppViewX Launches Global Partner Program Amid Rising Demand for Machine and Agent Identity Security app
  • Press Release

AppViewX Launches Global Partner Program Amid Rising Demand for Machine and Agent Identity Security

cybernewswire June 30, 2026 0
New York, United States, June 30th, 2026, CyberNewswire Building on the momentum of its Agent Identity Security...
Read More Read more about AppViewX Launches Global Partner Program Amid Rising Demand for Machine and Agent Identity Security
NLnet Labs Patches Four Critical NSD Vulnerabilities NSD DNS vulnerabilities and CVE-2026-12244
  • Vulnerability Report

NLnet Labs Patches Four Critical NSD Vulnerabilities

Do Son June 30, 2026 0

NLnet Labs patched critical NSD DNS vulnerabilities, including CVE-2026-12244. Update now to protect your multi-tenant secondary DNS deployments.

Thousands Affected by NVIDIA 9.8 Auth Bypass NVIDIA security updates fixing CVE-2026-24270, CVE-2026-24260, and CVE-2026-24264
  • Vulnerability Report

Thousands Affected by NVIDIA 9.8 Auth Bypass

Do Son June 30, 2026 0

NVIDIA security updates patch a critical 9.8 CVSS authentication bypass in AIStore, plus severe flaws in Triton and Container Toolkit impacting thousands.
INC Ransomware Targets Mainframes in APAC Campaign INC ransomware targets mainframes using cross-platform ransomware payloads
  • Malware

INC Ransomware Targets Mainframes in APAC Campaign

Do Son June 30, 2026 0

INC ransomware targets mainframes using cross-platform ransomware payloads. Attackers expose a new campaign hitting APAC manufacturing and food companies.

Claude Fable 5 Requires Separate Credits and Strict ID Checks Claude Fable 5 credit purchase and identity verification UI leak
  • Technology

Claude Fable 5 Requires Separate Credits and Strict ID Checks

Do Son June 30, 2026 0

Anthropic's upcoming Claude Fable 5 model may require separate credit purchases and strict government ID verification, according to newly leaked app strings.

Gemini Personalized Images Now Free for US Users Gemini personalized images created free with Nano Banana and Google Photos showing the user's real face and life details
  • Technology

Gemini Personalized Images Now Free for US Users

Do Son June 30, 2026 0

Gemini personalized images are now free for eligible US users, using Nano Banana and Google Photos to create AI pictures that look like you.

Hospitality Malware Campaign Deploys Node.js Implant North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Cybercriminals

Hospitality Malware Campaign Deploys Node.js Implant

Do Son June 30, 2026 0

An active hospitality malware campaign uses photo lures and authentication laundering to infect hotel networks with a persistent Node.js implant.
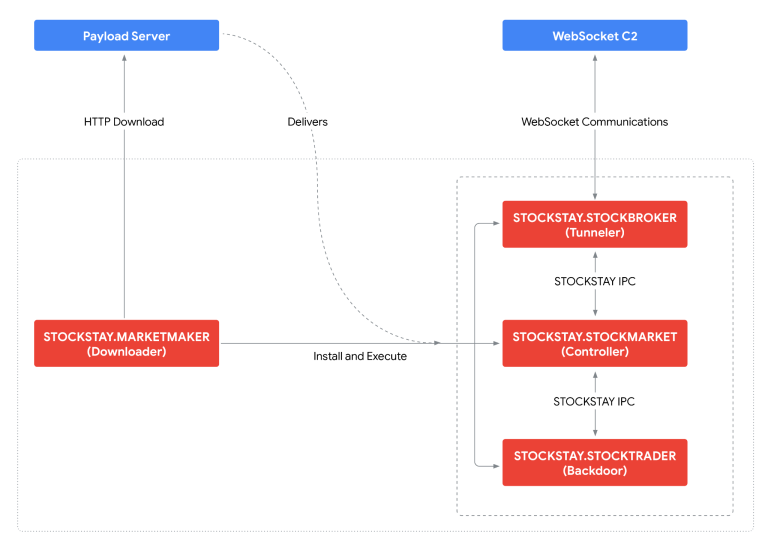
Turla STOCKSTAY Backdoor Targets Ukrainian Military Turla STOCKSTAY backdoor attacks Ukrainian military targets
  • Malware

Turla STOCKSTAY Backdoor Targets Ukrainian Military

Do Son June 30, 2026 0

Turla STOCKSTAY backdoor attacks Ukrainian military targets. Russian cyber espionage groups deploy this .NET malware via malicious RDP and WinRAR flaws.

TinyRCT Backdoor Attacks Target Asian Critical Infrastructure North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Cybercriminals

TinyRCT Backdoor Attacks Target Asian Critical Infrastructure

Do Son June 30, 2026 0

Chinese-speaking actors deploy TinyRCT backdoor attacks against Southeast Asian government and energy sectors. Discover the CL-STA-1062 cyber espionage tactics.

OpenClaw Brings Agentic AI to iOS and Android Phones OpenClaw app bringing agentic AI to iOS and Android with deep device permissions for an AI agent assistant
  • Technology

OpenClaw Brings Agentic AI to iOS and Android Phones

Do Son June 30, 2026 0

The OpenClaw app brings agentic AI to iOS and Android, letting an AI agent access your camera, screen, contacts, calendar, and more.
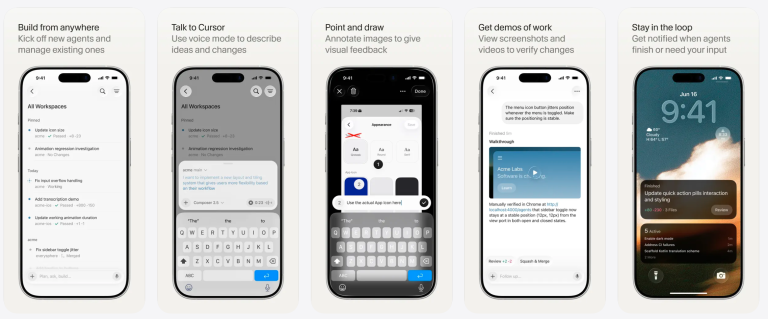
Cursor iOS Beta App Brings Remote AI Coding to Mobile Cursor iOS beta app interface for remote AI coding
  • Malware

Cursor iOS Beta App Brings Remote AI Coding to Mobile

Do Son June 30, 2026 0

Discover the new Cursor iOS beta app. This remote AI coding tool lets developers manage agents, review code, and merge pull requests directly from mobile.
iPhone 18 Pro Secrets Leaked in Tata Electronics Breach iPhone 18 Pro leak from the Tata Electronics data breach exposing Apple supplier lists, components, and drop-test photos RCS End-to-End Encryption
  • Data Leak

iPhone 18 Pro Secrets Leaked in Tata Electronics Breach

Do Son June 30, 2026 0

An iPhone 18 Pro leak from the Tata Electronics breach exposes supplier lists, component details, and device photos on the dark web.

WhatsApp Usernames Let You Hide Your Phone Number WhatsApp usernames privacy feature letting users connect without sharing a phone number, with reservations open now
  • Technology

WhatsApp Usernames Let You Hide Your Phone Number

Do Son June 30, 2026 0

WhatsApp usernames let you chat without sharing your phone number. Reservations open this week ahead of the full launch later this year.

WSO2 API Manager Hit by CVSS 10 Auth Bypass and Six More Flaws WSO2 API Manager vulnerabilities CVE-2026-5430 CVSS 10 JWT authentication bypass security advisory
  • Vulnerability Report

WSO2 API Manager Hit by CVSS 10 Auth Bypass and Six More Flaws

Do Son June 30, 2026 0

WSO2 patched seven flaws across API Manager and gateways, led by a CVSS 10 JWT auth bypass (CVE-2026-5430). Update WSO2 API Manager now.

Synology MailPlus Server Patched for CVSS 10 Flaw CVE-2026-13136 Synology MailPlus Server vulnerability CVE-2026-13136 CVSS 10 security advisory
  • Vulnerability Report

Synology MailPlus Server Patched for CVSS 10 Flaw CVE-2026-13136

Do Son June 30, 2026 0

Synology MailPlus Server has three new flaws, including CVE-2026-13136 at CVSS 10. Update to 4.0.1-31663 now. No exploit confirmed.
SimpleHelp Authentication Bypass Exploited in the Wild to Deploy TaskWeaver and Djinn Stealer hacked
  • Vulnerability Report

SimpleHelp Authentication Bypass Exploited in the Wild to Deploy TaskWeaver and Djinn Stealer

Do Son June 30, 2026 0

CVE-2026-48558, a SimpleHelp authentication bypass, is exploited in the wild to deploy TaskWeaver and Djinn Stealer. CISA added it to KEV. Patch now.
Critical wolfSSL Security Vulnerabilities Expose IoT Systems Diagram explaining wolfSSL security vulnerabilities and X.509 trust-chain bypass.
  • Vulnerability Report

Critical wolfSSL Security Vulnerabilities Expose IoT Systems

Do Son June 30, 2026 0

Developers patched six severe wolfSSL security vulnerabilities, including an X.509 trust-chain bypass. Update embedded systems to protect against exploits.

EVoke Systems Vulnerabilities Expose Charging Stations EVoke Systems vulnerabilities and charging station security
  • Vulnerability Report

EVoke Systems Vulnerabilities Expose Charging Stations

Do Son June 30, 2026 0

Critical EVoke Systems vulnerabilities expose charging stations to unauthorized access and DoS attacks. Update security profiles to mitigate these risks.

Migrate Large Number of Outlook Data Files (PST) to Office 365 Without Downtime? Fractile AI inference chip AI Market Trends 2025, Similarweb AI Report
  • Technique

Migrate Large Number of Outlook Data Files (PST) to Office 365 Without Downtime?

Do Son June 30, 2026 0
Whether you are an admin, an MSP for a business unit, or an individual – migrating user...
Read More Read more about Migrate Large Number of Outlook Data Files (PST) to Office 365 Without Downtime?
Four Critical Cacti Vulnerabilities Fixed in 1.2.31 Cacti vulnerabilities CVE-2026-39955 CVE-2026-39938 pre-auth SQL injection LFI security update 1.2.31
  • Vulnerability Report

Four Critical Cacti Vulnerabilities Fixed in 1.2.31

Do Son June 30, 2026 0

Cacti vulnerabilities in 1.2.30 include pre-auth SQL injection and LFI, both CVSS 9.8 (CVE-2026-39955, CVE-2026-39938). Update to 1.2.31 now.
Pollo AI Avatar Hands-On Review: Testing Its True Commercial Performance tes
  • Technique

Pollo AI Avatar Hands-On Review: Testing Its True Commercial Performance

Do Son June 30, 2026 0

Read this Pollo AI Avatar Review to understand how the Pollo Avatar AI avatar generator transforms a single photo into a lifelike talking presenter for marketing, ads, and social media content in a high-speed cloud workflow.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-79589CVSS 9.8
    The WIFI4 N300 router (Model: T1 Pro) v1.0.0 by U-speed contains an insecure access control flaw that allows...
    📅 Updated: Nov 3, 2026
  • CVE-2026-61567CVSS 10.0
    AVideo is a video-sharing Platform. Prior to 8.1.0, the live-streaming endpoint `view/videosListToLive.php` accepts an attacker-named streamer in `webSiteRootURL`,...
    📅 Updated: Nov 3, 2026
  • CVE-2026-107029CVSS 9.1
    Insecure permissions in rubenalfon Pile v1.1.3 allows unauthorized attackers to invoke an exported component, leading to arbitrary data...
    📅 Updated: Nov 3, 2026
  • CVE-2026-120447CVSS 9.2
    HotGo 2.8.4 through 2.15.1 contains an authentication bypass vulnerability that allows unauthenticated attackers to choose the SMS login...
    📅 Updated: Nov 2, 2026
  • CVE-2023-29073CVSS 9.8
    A maliciously crafted MODEL file when parsed through Autodesk AutoCAD 2024 and 2023 can be used to cause...
    📅 Updated: Nov 2, 2026
  • CVE-2023-29074CVSS 9.8
    A maliciously crafted CATPART file when parsed through Autodesk AutoCAD 2024 and 2023 can be used to cause...
    📅 Updated: Nov 2, 2026
  • CVE-2026-77526CVSS 9.9
    ## Summary `FacturaScripts\Core\UploadedFile::move($destiny, $destinyName)` concatenates `$destiny` and `$destinyName` without normalizing the resulting path. Every caller in the codebase...
    📅 Updated: Nov 2, 2026
  • CVE-2026-45262CVSS 9.9
    ## Summary > **Live PoC verified 2026-04-30** against a stock FacturaScripts master at `127.0.0.1:8081`. A scoped `ApiKey` with...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.