Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Technique
  • Pentesters – the new cybersecurity heroes
  • Technique

Pentesters – the new cybersecurity heroes

Do Son March 26, 2020 4 minutes read
cybersecurity heroes

Pentesting is exactly what you think it is, penetration testing. A certain simulated attack meant to detect vulnerabilities within a system. While the market of software development and IT outsourcing are constantly growing, the necessity to integrate pentesters is becoming vital.
Remember what the S stands for in HTTPS? Secure. While it is just a basic security measure it is still relevant. It is meant to protect the privacy and integrity of the data on that platform.

Also, privacy is becoming one of the central issues in today’s narrative. Especially since Europe has introduced its GDPR policy that has affected every other nation that is collaborating with Europeans.

However, cyberattacks have become so advanced that not even complex firewalls can protect against them. Understanding what a cyberattack is, is crucial to a business.

What is a cyberattack?

Most dictionaries agree that it is a

  • deliberate action
  • on networks or technology-dependent entities
  • for the result of disrupting, destroying, altering data.

Every 39 seconds there is a hacker attack, according to Security magazine. Also, the “market” for hacking is always growing, making cybercrime more profitable than the illegal drug trade.

However, there is still some good news, as the heroes of the modern age, the pentesters come to the rescue and help businesses.

Black hat vs. White hat

Black hats have malicious intents, always looking to do bad things, and contrasting it, white hats put their knowledge at good use to help to find vulnerabilities before a malicious actor would find these, thus helping companies avoid revenue and repudiation loss that could cripple the business.

White hat hacking is an ethical way of hacking. This is where the term ethical hacking comes from. Some differentiate grey hat hackers as well, meaning hackers with good intentions that penetrate a system without permission (this way of hacking is also illegal).

Pentesting is a serious business

Pentesters have an important mission, they need to assure that no vulnerability passes their gates, vulnerabilities that an attacker could leverage to get into the network. This same work in most cases needs to be done without bringing the network down while running these tests. On the other hand, a black hat hacker doesn’t worry about any collateral damage done during the process, more so, that might be the purpose.

Pentesting process

Hence, there is a certain process that one needs to follow. Usually, it goes like this:
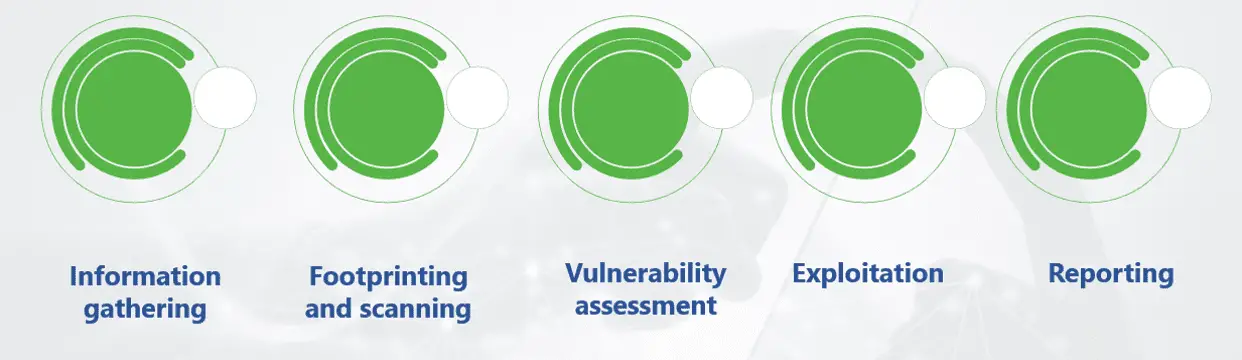
  • Information gathering – is a fundamental stage of the process that requires a lot of patience. The goal is to gather as much information as possible about the system, infrastructure, and business that is under assessment, information that will be used in the following steps.
  • Footprinting and scanning – this stage is for deepening knowledge of the scope servers and service by fingerprinting the used operating system, port scanning, and certain service detecting.
  • Vulnerability assessment – here the pentester builds a list of vulnerabilities, and carefully assesses each of the targets found in the previous steps. One can do it manually or with automated tools. However, these automated tools won’t carry the overall pentesting.
  • Exploitation – since the process is cyclic, it only ends when there are no more targets in-scope to exploit.
  • Reporting – the report explains the result of the pentesting. It is as important as the whole penetration testing process.

This must address the

  • Technique used
  • Vulnerabilities found
  • The impact and risk for each vulnerability
  • And tips for remediation.

Given that human activity in general moves to the virtual world, black hat hackers become the most dangerous enemies of the system that can do the most serious harm to the whole business ecosystem.

As a response to this, ethical hackers appear to help strengthen the system. Hence, pentesting is becoming one of the most in-demand jobs.

Tags: cybersecurity heroes pentester

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-123958CVSS 9.4
    A vulnerability was identified in TOTOLINK CA300-PoE 6.2c.884. The affected element is the function setLanConfig of the file...
    📅 Updated: Nov 7, 2026
  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 7, 2026
  • CVE-2026-18836CVSS 9.3
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to obtain sensitive...
    📅 Updated: Nov 7, 2026
  • CVE-2026-18838CVSS 9.4
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to obtain sensitive information and modify API...
    📅 Updated: Nov 7, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 7, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 7, 2026
  • CVE-2026-17410CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to access...
    📅 Updated: Nov 7, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.