Skip to content
October 26, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • PHP 7.3 is 22% faster than PHP 7.0
  • Technology

PHP 7.3 is 22% faster than PHP 7.0

Do Son July 12, 2018 2 minutes read
PHP 7.3
Add Daily CyberSecurity as a preferred source on Google
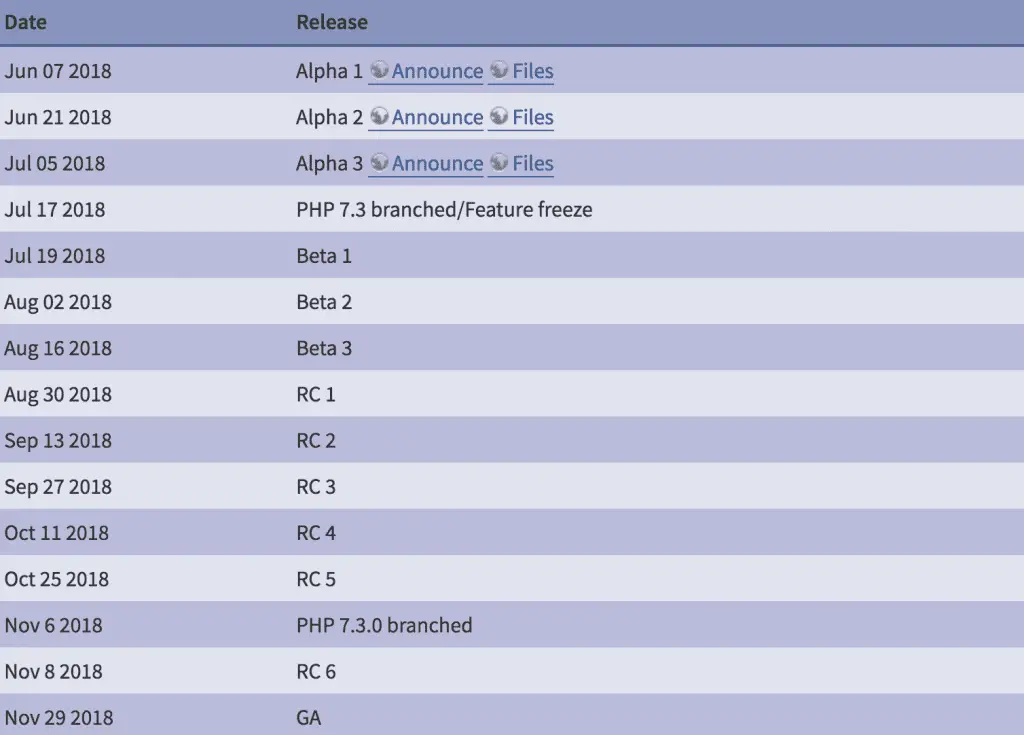
With the release of PHP 7.3 Alpha3 last week, it means that PHP 7.3 is about to enter the feature freeze phase, no new features will be added, and subsequent beta and RC versions will be mainly fixed until the official release is released on November 29.
From the current update instructions, PHP 7.3 is not a version that focuses on new features, including more bug fixes. PHP 7.3 removes support for BeOS, improves PHP GC, and implements the more flexible Heredoc and Nowdoc syntax.
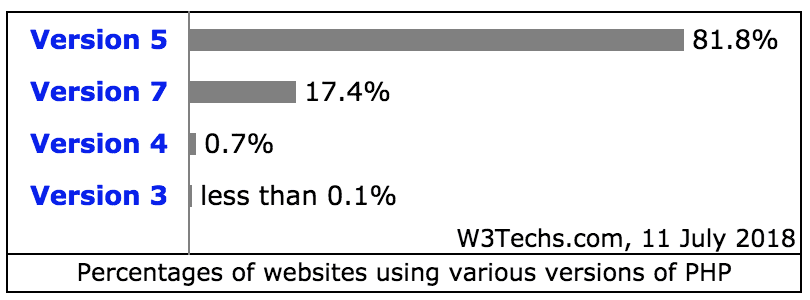
PHP 7 was officially released in December 2015. After more than two years of development and iteration, usage has been rising, but it still lags behind the PHP 5 series. The latest statistics for W3Techs.com are as follows:
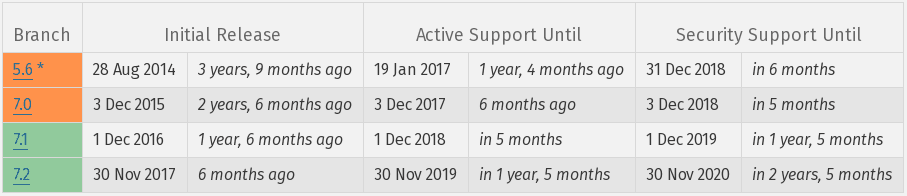
The latest version of the PHP 5 series is PHP 5.6 released in 2014 and is the most widely used version. However, after six months, PHP 5.6 will completely lose official support. At that time, it may bring a round of user surge to PHP 7.
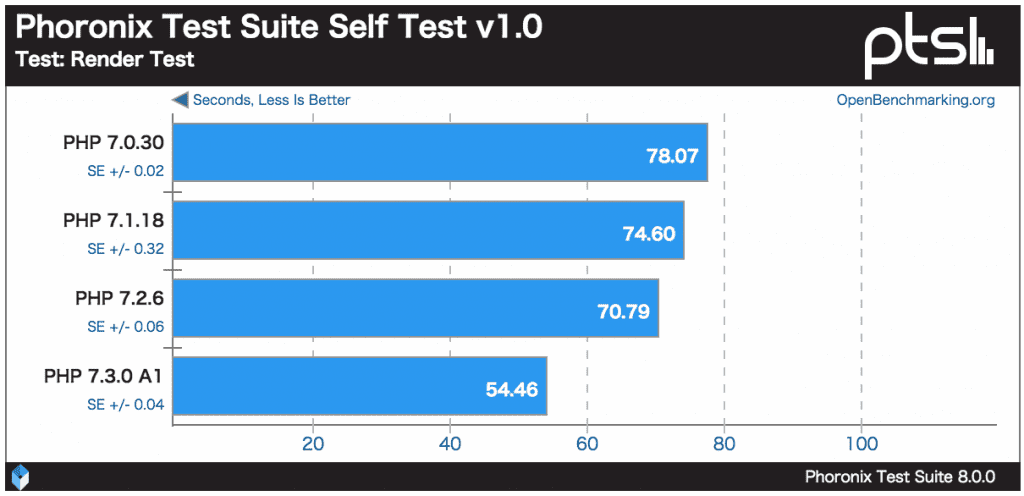
Everyone knows that when PHP 7 was released, it claimed to be twice as fast as PHP 5.6. What about the performance of PHP 7.3? Phoronix conducted a benchmark test when PHP 7.3 Alpha1 was released. It turns out that in the popular PHPBench benchmark, PHP 7.3.0 Alpha 1 is about 7% faster than the current PHP 7.2 stable version and 22% faster than PHP 7.0:
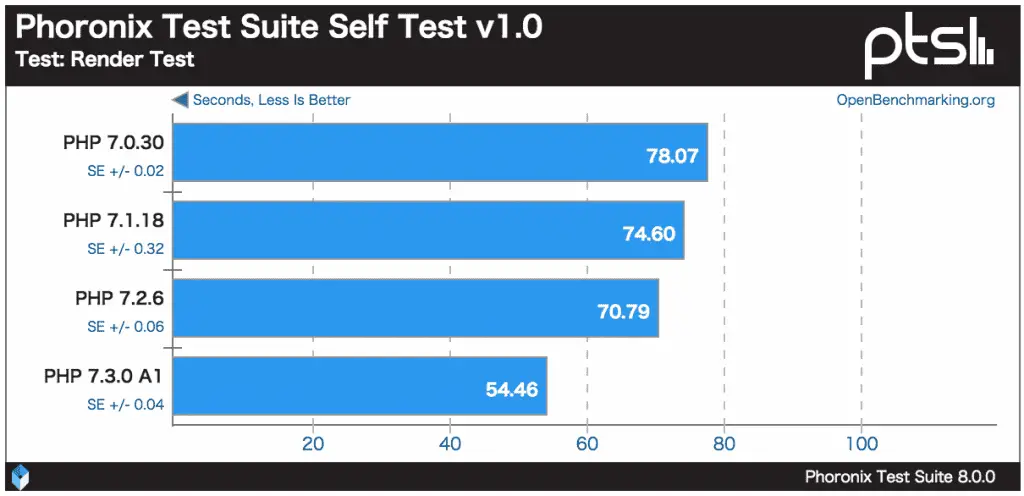
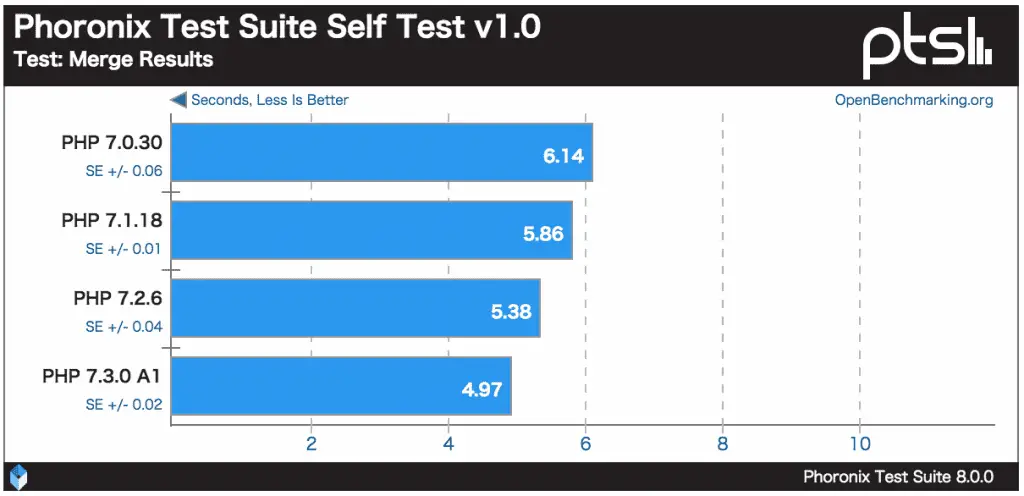
PHP 7.3 also performed well when using Phoronix’s own test suite. Significant improvements in both rendering and data processing tests.
 

Related coverage

  • U.S. Marshals Service will auction off 3,813 bitcoins valued at about $52 million
  • The Vibe Coding Invasion: Why Your AI-Built App is Stuck in Apple’s “Review Purgatory”
  • Elon Musk’s Grok Faces “Large-Scale” EU Probe Over Deepfake Imagery and Data Rights
  • Parallel Realities: Google Gemini Prepares to Launch Branching AI Conversations
  • OpenAI Unveils AI-Powered Browser: ChatGPT Integration to Revolutionize Web Browse & Challenge Chrome
  • Samsung Sets Oct 21 Event to Unveil “Project Moohan,” Its Android XR Headset Rival to Vision Pro
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: PHP 7.3

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 26, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 26, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 26, 2026
  • CVE-2026-106173CVSS 9.8
    A improper limitation of a pathname to a restricted directory (\'path traversal\') vulnerability in Fortinet FortiSIEM 7.5.0 may...
    Admin intel📅 Updated: Oct 25, 2026
  • CVE-2014-125133CVSS 8.7
    NativeChurch theme for WordPress before 1.6.2 contains a path traversal vulnerability that allows unauthenticated attackers to download arbitrary...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2015-20128CVSS 8.8
    FooSun DotNetCMS 1.0 and 2.0 contains an SQL injection vulnerability that allows unauthenticated attackers to manipulate MSSQL queries...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2016-20104CVSS 8.7
    EyeLock nano NXT 3.05.1193, 3.04.1108, 3.03.944, and 3.01.646 contain a path traversal vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2026-110447CVSS 9.2
    Collabora Online Built-in CODE Server before 26.4.303 (richdocumentscode), a Nextcloud app, allows remote code execution, as exploited in...
    CISA KEV📅 Added to KEV: Oct 23, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-45083CVSS 9.8
    The Goobi viewer is a web application that allows digitised material to be displayed in a web browser....
    📅 Updated: Oct 26, 2026
  • CVE-2026-47323CVSS 9.8
    Camel-CXF and Camel-Knative Message Header Injection via Missing Inbound Filtering The CXF and Knative HeaderFilterStrategy implementations (CxfRsHeaderFilterStrategy in...
    📅 Updated: Oct 26, 2026
  • CVE-2026-42731CVSS 9.8
    Incorrect Privilege Assignment vulnerability in miniOrange miniorange otp verification miniorange-otp-verification allows Privilege Escalation.This issue affects miniorange otp verification:...
    📅 Updated: Oct 26, 2026
  • CVE-2026-32999CVSS 9.0
    Insufficient character filtering in backup agent signing module on Comet Backup server allows authenticated tenant administrator to execute...
    📅 Updated: Oct 26, 2026
  • CVE-2026-46907CVSS 9.9
    Vulnerability in the JD Edwards EnterpriseOne Order Promising product of Oracle JD Edwards (component: Order Promising Integration). The...
    📅 Updated: Oct 26, 2026
  • CVE-2026-46908CVSS 9.9
    Vulnerability in the JD Edwards EnterpriseOne Accounts Payable product of Oracle JD Edwards (component: Accounts Payable). The supported...
    📅 Updated: Oct 26, 2026
  • CVE-2026-46909CVSS 9.8
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Enterprise Infrastructure Security). Supported versions...
    📅 Updated: Oct 26, 2026
  • CVE-2026-46910CVSS 9.1
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Enterprise Infrastructure Security). Supported versions...
    📅 Updated: Oct 26, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.