 Do Son
Patch 9 critical Adobe vulnerabilities in Adobe Campaign Classic and Connect, including 9.9 CVSS RCE flaws CVE-2026-104351 and CVE-2026-48360.
Adobe
Three critical Adobe Campaign Classic flaws (CVE-2026-76197, CVSS 10.0) allow arbitrary code execution. Update to build 9401 now.

Adobe patched critical Adobe Campaign Classic flaws. CVE-2026-48331 scores CVSS 10.0 and enables arbitrary code execution. Update to build 9399 now.
Adobe Campaign Classic flaw CVE-2026-48449 scores a perfect CVSS 10.0 and allows arbitrary code execution. Update to build 9398 now.
Adobe patches critical RCE and security bypass flaws in ColdFusion 2023 & 2025. Protect your enterprise servers from takeover—update to the latest version now.

Adobe is bypassing Chrome security by quietly editing your hosts file to track Creative Cloud installations. Learn how this stealth telemetry works in 2026.
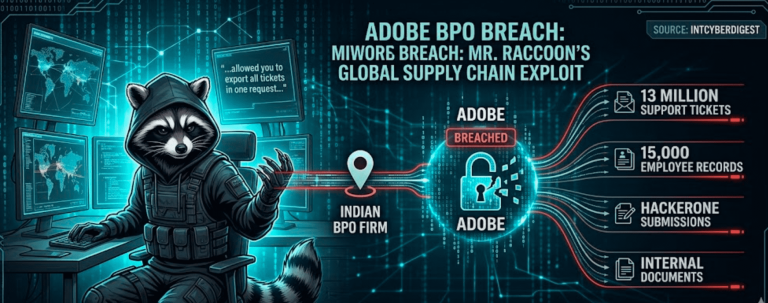
13M Adobe tickets leaked! Mr. Raccoon bypassed elite defenses by targeting a BPO partner in India. See how the "human element" cracked the supply chain.

Active exploitation alert: The PolyShell flaw in the Magento REST API allows unauthenticated RCE via malicious images. Learn how to protect your store now.

OpenAI integrates Photoshop, Acrobat, and Adobe Express into ChatGPT via MCP. The move creates an "AI super-app," enabling 800M users to edit images and PDFs directly in chat.

Adobe and Google partnered to integrate Premiere Mobile's professional tools directly into the YouTube Shorts workflow, adding AI features and exclusive templates.

Figma has relaunched its IPO plans, aiming to raise $1.2 billion and achieve a $19.3 billion valuation after its $20 billion acquisition by Adobe collapsed due to regulatory scrutiny.
Get insights into a large-scale phishing campaign targeting employees across 30 companies. Uncover the techniques used by threat actors to evade detection and deceive victims.
Stay informed about the latest Adobe Flash Player vulnerability. Learn about the critical flaws actively exploited in the wild.
Stay updated on the latest Magento security vulnerabilities and learn how to protect your e-commerce platform from potential threats.

Rooted in a flaw within the "file upload logic" of AEM Forms on JEE versions 6.5.19.0 and earlier, this flaw paves the way for unauthorized path traversal

Dubbed as CVE-2023-26369, this nefarious zero-day vulnerability stems from an out-of-bounds write weakness.

Adobe released security updates for ColdFusion versions 2021 and 2018 to resolve this critical flaw, tracked as CVE-2023-26360