 Do Son
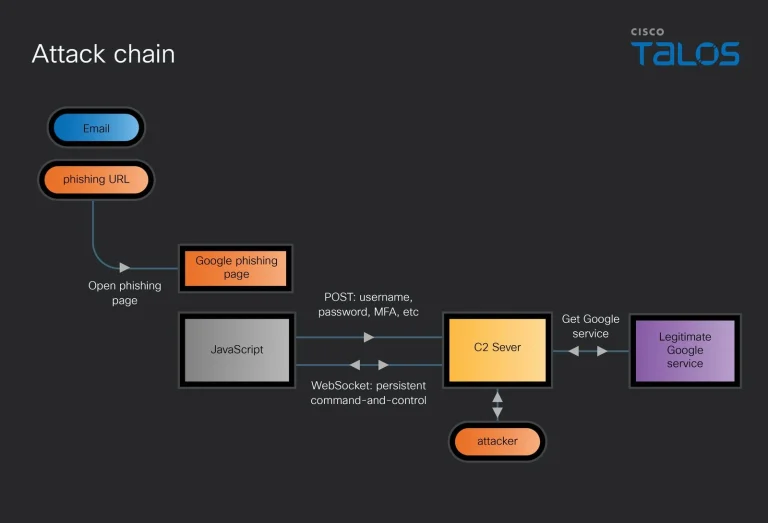
UAT-11985 used AI-written lures and an AitM phishing kit in a Taiwan spear-phishing campaign that steals Google logins and bypasses MFA.
AI Phishing

Varonis uncovers Bluekit, a new phishing-as-a-service kit using AI and 40+ templates to automate session hijacking and credential theft. See how it works.
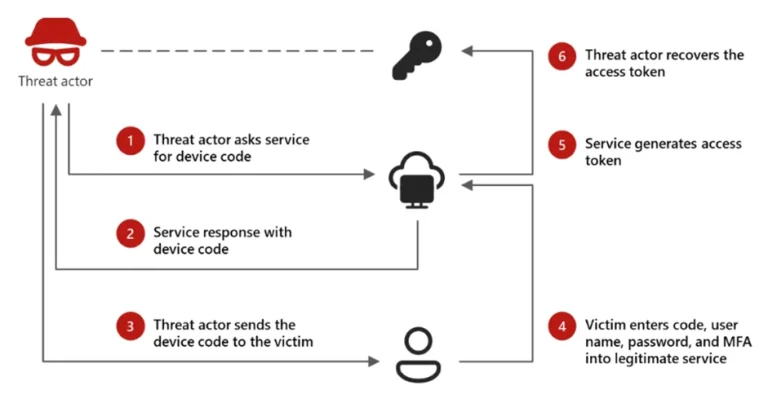
Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!

Intezer reveals EchoGather, a new Paper Werewolf backdoor using XLL files and AI-generated decoys to target Russian defense and high-tech firms.

Volexity found China-aligned APT UTA0388 used ChatGPT to generate multilingual spear-phishing lures and assist in GOVERSHELL malware development for espionage.