 Do Son
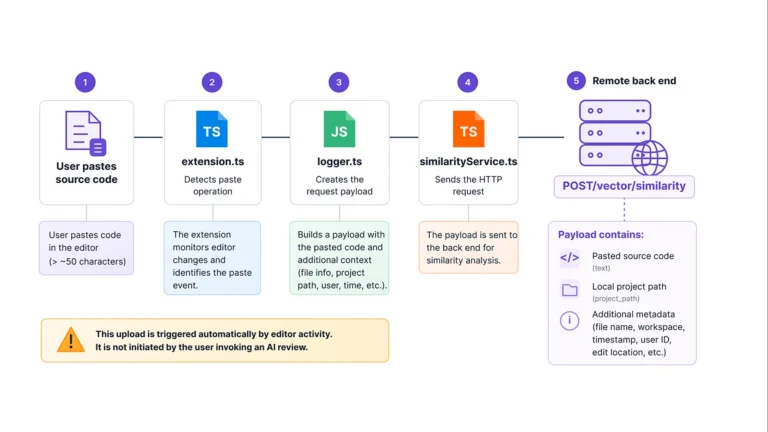
Akamai reveals the CodeAudit AI extension and VS Code CodeAudit AIextension upload pasted source code and metadata over unencrypted HTTP.
Akamai

Attackers exploit a Langflow RCE flaw to drop a custom Gafgyt botnet built purely for DDoS, Akamai reports. The payload hides C2 with a modified RC4 cipher.
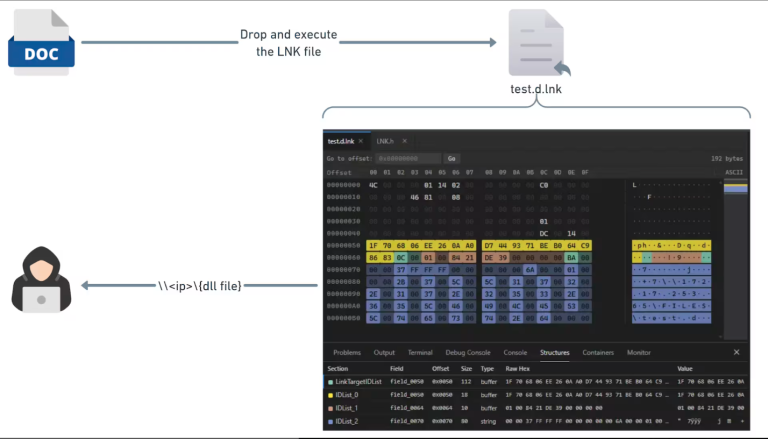
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!

A new malware strain is targeting exposed Docker APIs, evolving from a cryptominer into a stealthy botnet that blocks ports to "own" a victim's system for exclusive use.

A new Active Directory flaw, BadSuccessor, allows low-privileged users to become Domain Admins. Akamai researchers warn that the technique remains a threat even after patching.

Akamai confirms Coyote, a Latin America-focused banking trojan, is the first malware to exploit Microsoft's UI Automation (UIA) framework in the wild for credential theft.

Akamai reports active exploitation of critical Wazuh RCE (CVE-2025-24016) by multiple Mirai botnets, targeting IoT devices since March 2025.

Discover a major misconfiguration vulnerability affecting top WAF vendors. Find out how attackers can exploit this flaw to bypass WAF protections.