 Do Son
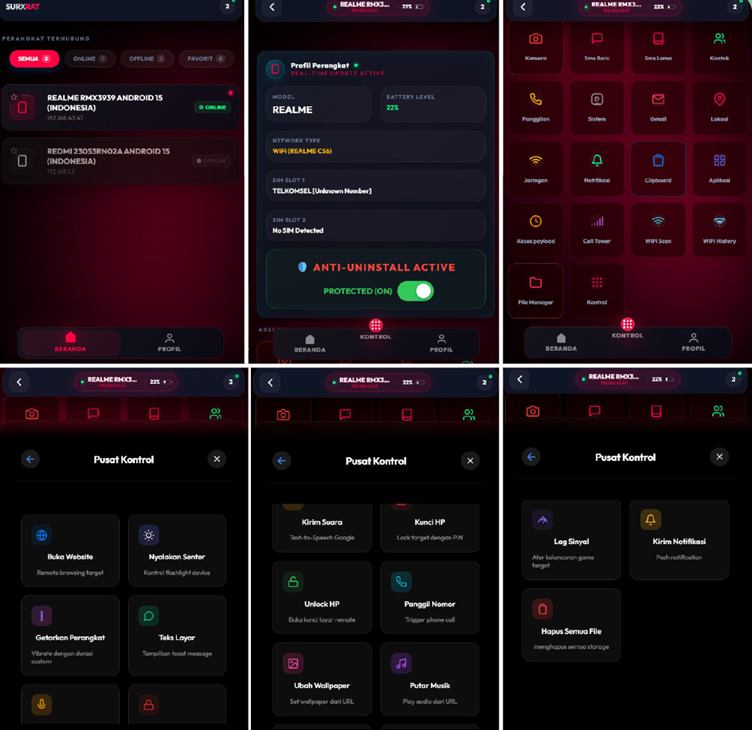
Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.
Android Malware
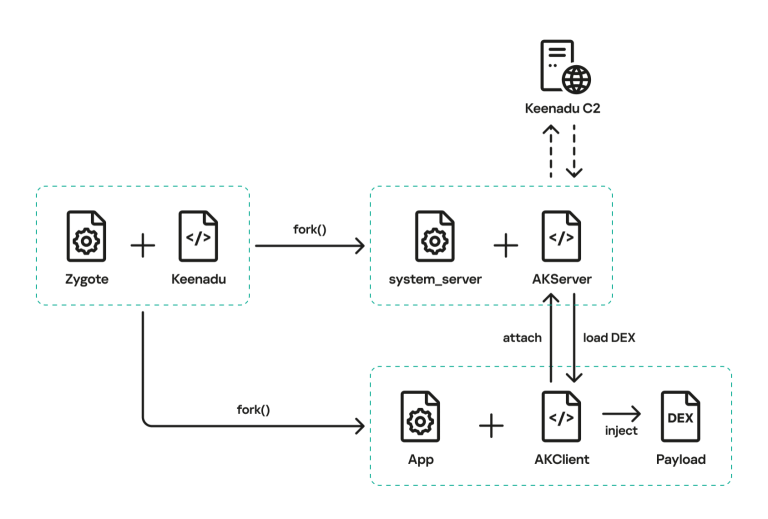
Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.
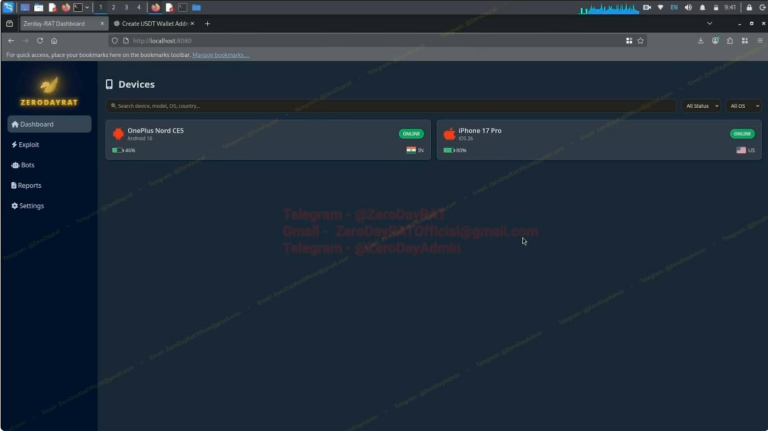
ZeroDayRAT mobile spyware is sold on Telegram. It offers full remote control of Android & iOS devices, including camera streaming & crypto theft.

New deVixor Android malware combines banking fraud with ransomware. Targeting Iranian users, it steals credentials and locks devices. Avoid APKs.

New "Ghost Tap" malware lets hackers relay NFC signals from your Android phone to steal funds remotely. Learn how this sophisticated Group-IB discovery works.

Kimsuky is deploying a new DOCSWAP RAT via QR codes and smishing. The DPRK-linked malware turns phones into surveillance tools for data theft.

RTO Challan malware hijacks Android devices in India using a fake traffic ticket lure, a malicious VPN, and SMS interception to steal UPI PINs and Aadhaar data.

A dangerous new Android malware called SeedSnatcher targets crypto users with overlay phishing on MetaMask/Trust Wallet. It uses BIP 39 validation to steal seed phrases and supports remote command execution for total device control.

Meet Albiriox, a new Russian Android banking Trojan sold as a service. Learn how its "AcVNC" tech enables on-device fraud against 400+ global apps.

CERT Polska exposed NGate, an Android malware that tricks users into tapping their card against their phone to steal NFC EMV data and PINs. The data is then relayed to an ATM for cash withdrawal.

Doctor Web exposed Android.Backdoor.Baohuo.1.origin, a malware hiding in a Telegram X clone. It uses a Redis database for C2, infects 58K+ devices, and steals crypto wallet info from the clipboard.

GhostGrab is a hybrid Android malware that steals banking credentials and OTPs via phishing WebView overlays while secretly running a Monero miner in the background to monetize the victim's device.

A sophisticated GhostBat RAT campaign targets Indian users by spoofing RTO apps (mParivahan). The malware steals UPI credentials and OTPs via phishing pages and uses a Telegram bot for C2.

SikkahBot, a new Android malware, is impersonating scholarship apps to steal financial data and automate transactions from students in Bangladesh.

A new report reveals a global malvertising campaign on Facebook spreading an evolved version of Brokewell malware to steal crypto and bypass 2FA.

ThreatFabric researchers have uncovered PhantomCard, an Android Trojan that uses an NFC relay attack to steal contactless card data and enable fraudulent payments.

McAfee uncovers a new Android malware campaign targeting Indian users. The malware impersonates major banks to steal financial data and silently mines Monero in the background.

Cleafy uncovers PlayPraetor, a Chinese-speaking MaaS Android RAT that has infected 11,000+ devices, using real-time control via Accessibility Services to conduct on-device fraud.

Cyble uncovers RedHook, a new Android banking trojan targeting Vietnamese users with sophisticated phishing, remote access, screen capture, and keylogging for full device takeover.

Trustwave uncovers an Android malware cluster using fake Facebook & TikTok apps to lure victims via brand impersonation, abusing permissions for data collection and traffic monetization.

McAfee warns of a new Android malware campaign targeting Bangladeshi expats with fake remittance apps like TapTap Send, stealing personal and financial data, including photo IDs.

Kaspersky warns that Triada Trojan now comes pre-installed in counterfeit Android device firmware, making it nearly impossible to remove without reinstallation.