
 Do Son
Kaspersky warns that Triada Trojan now comes pre-installed in counterfeit Android device firmware, making it nearly impossible to remove without reinstallation.
Android Malware

SuperCard X malware uses a novel NFC-relay technique to steal credit card data from Android devices, enabling fraudulent POS and ATM transactions.

Prodaft analysis reveals Gorilla, a new Android malware evolving to steal data and potentially conduct espionage.
Explore the rise of the Android malware campaign leveraging the .NET MAUI framework to evade security measures effectively.

Discover BackConnect, the new strain of QBot malware that has resurfaced with enhanced capabilities. Learn how it adapts and what it means for cybersecurity.

Uncover the alarming Android malware campaign attributed to the Indian APT group DONOT. Learn how this group targets individuals and organizations for strategic intelligence collection.

Uncover the new NGate malware: attackers target Czech bank customers through infected Android devices, stealing payment card data.
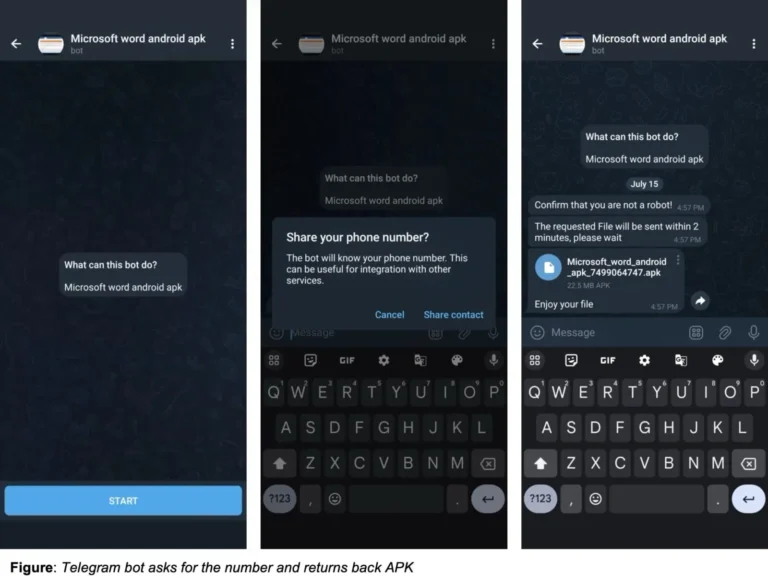
Discover the alarming spread of a new Android malware campaign: a silent SMS stealer targeting OTPs from top brands and compromising millions of accounts.

Making it imperative to develop innovative techniques and tools to combat sophisticated malware like BadPack

The malware, identified as an InfoStealer, poses as the official app of Bahrain’s Labour Market Regulatory Authority (LMRA)

The timing of the artifacts associated with this campaign suggests that Starry Addax may be ramping up its operations.

This sample included the SpyNote RAT, featuring new additions aimed at evading analysis and targeting cryptocurrencies specifically.

According to the latest report from Dr.Web, October 2023 witnessed a significant surge in the activity of malicious software targeting Android-based mobile devices