 Do Son
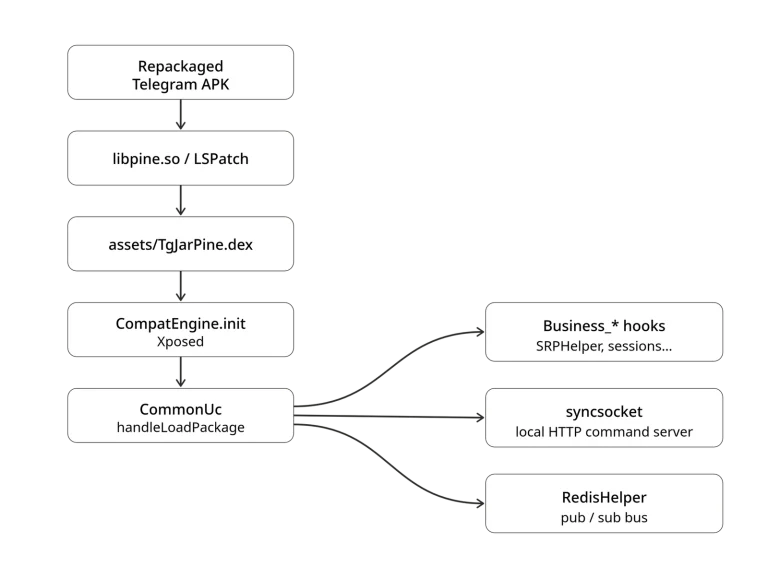
Researcher Ovi exposes uCreator Android spyware. The YingGai uCreator Android spyware platform uses VirtualApp and LSPatch to hijack 20 mobile apps.
Android Malware
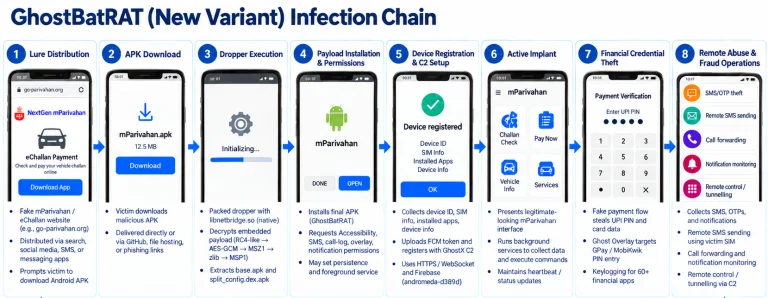
Cyble reveals the GhostX ecosystem where Android GhostBat RAT and the new GhostBat RAT variant use Ghost Overlay to steal PINs from 60 Indian apps.

ThreatFabric uncovers the Hirudo banking trojan. The Android Hirudo banking trojan replaces real banking apps with patched copies to steal funds.
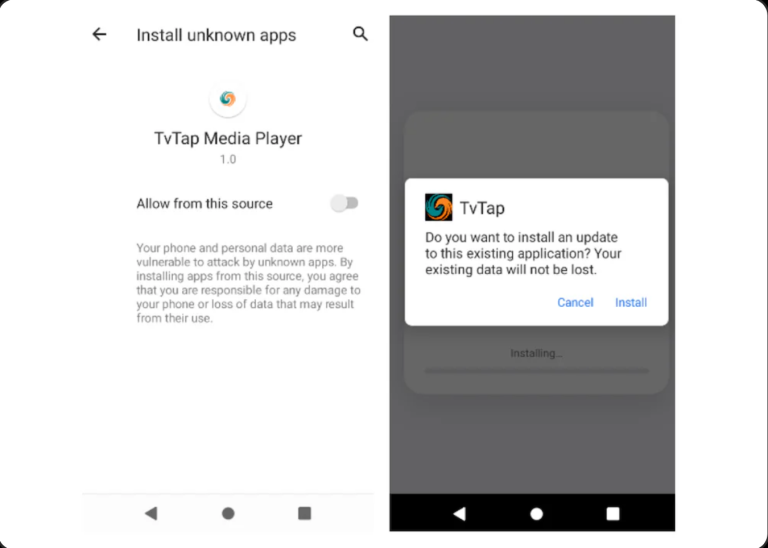
Group-IB found the RemControl Android banking trojan, a new malware using AI phishing overlays and fake TVTap apps to steal banking PINs and credentials.
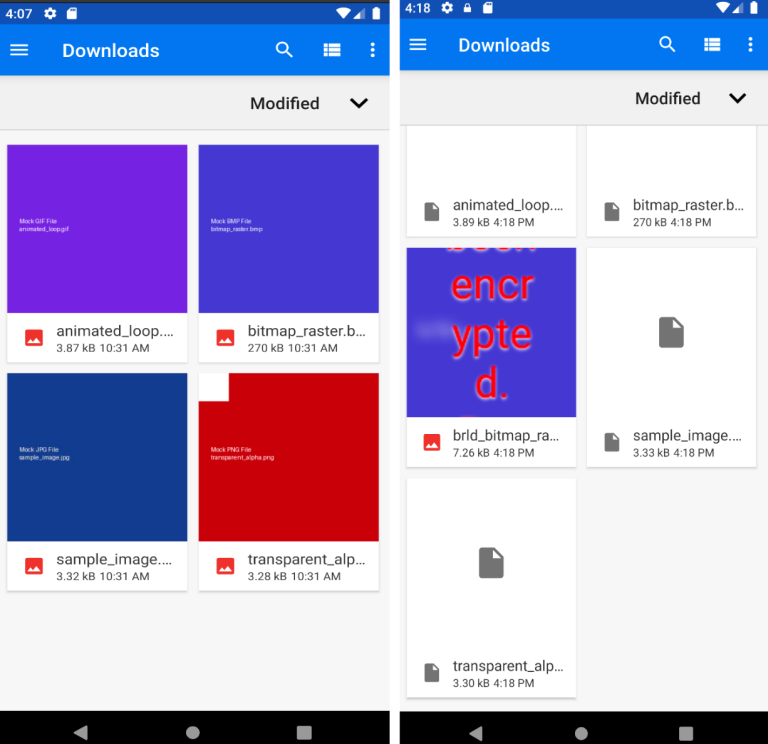
Zimperium zLabs discovered Mantax Otax Android malware, a fierce Indonesian mobile ransomware integrating spyware to hijack, record, and extort victims.
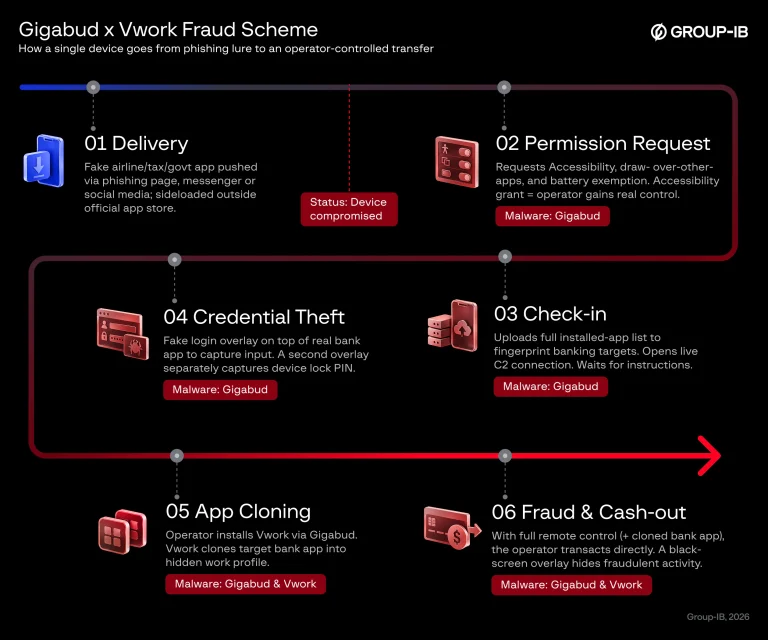
Group-IB uncovered how the Gigabud Vwork Android malware chain clones apps. Discover how Vwork Android malware evades bank detection.
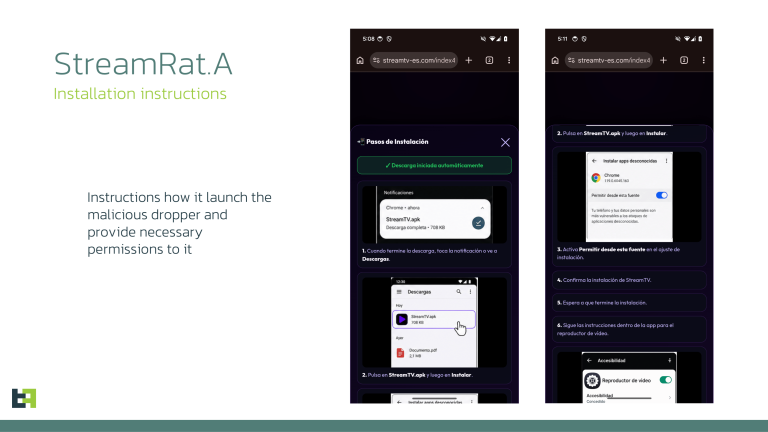
A StreamRat banking trojan campaign uses fake Meta TV-streaming ads to infect Android users. The StreamRat banking trojan enables full device takeover.
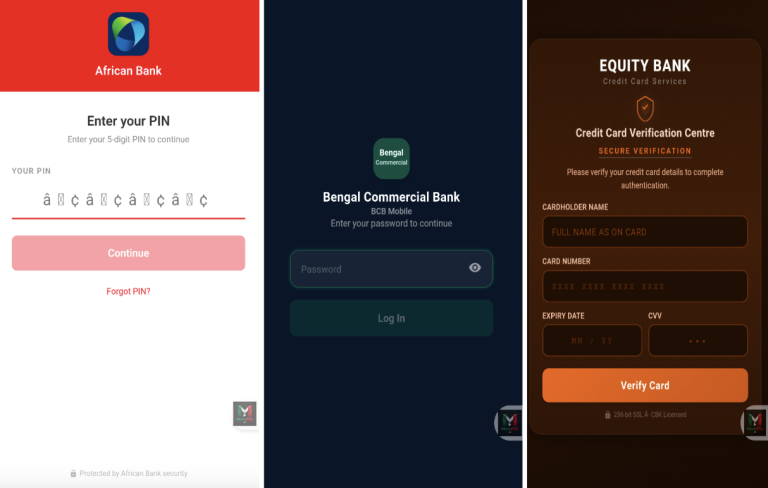
The new ToxicPanda 2.0 banking Trojan attacks target hundreds of financial apps globally. Learn how this ToxicPanda 2.0 banking Trojan steals credentials.
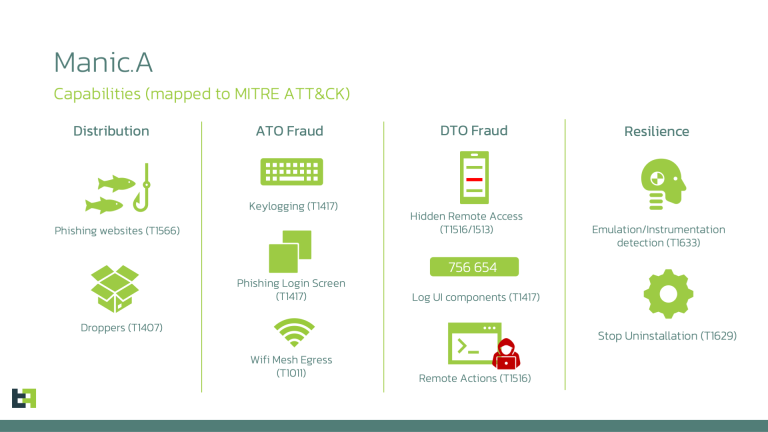
A new Manic Android malware campaign combines banking fraud and spyware, using a unique offline mesh relay to steal data even without internet access.
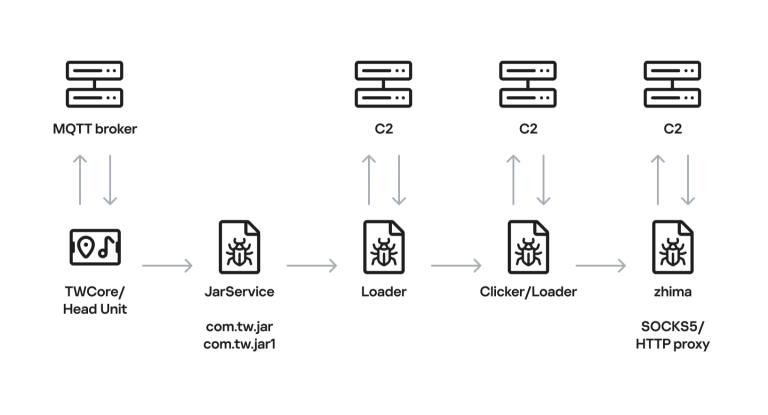
Kaspersky exposed Android head unit malware turned into a botnet. Discover how this Android head unit malware botnet infects smart cars.
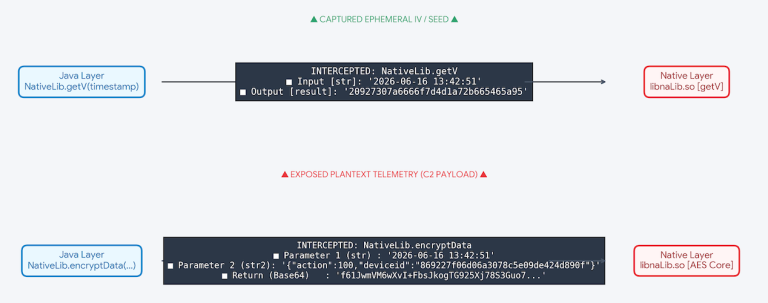
The GoldPickaxe banking Trojan returns, stealing biometric data, SMS, and lock screens from Android users across Asia, Zimperium warns.
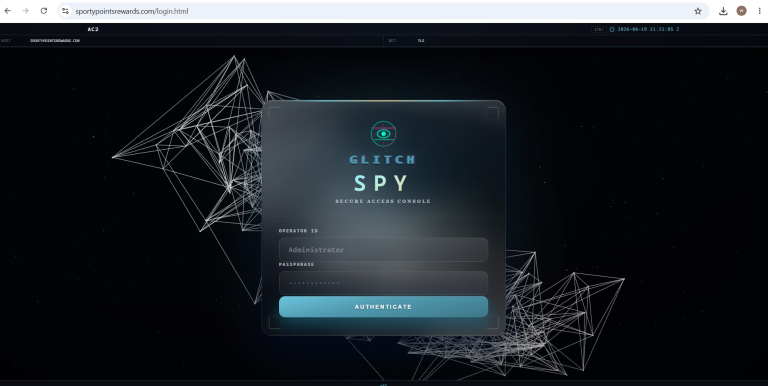
New Glitch SPY Android RAT spreads via a fake rental app, abusing Accessibility to steal data and swap crypto wallet addresses.
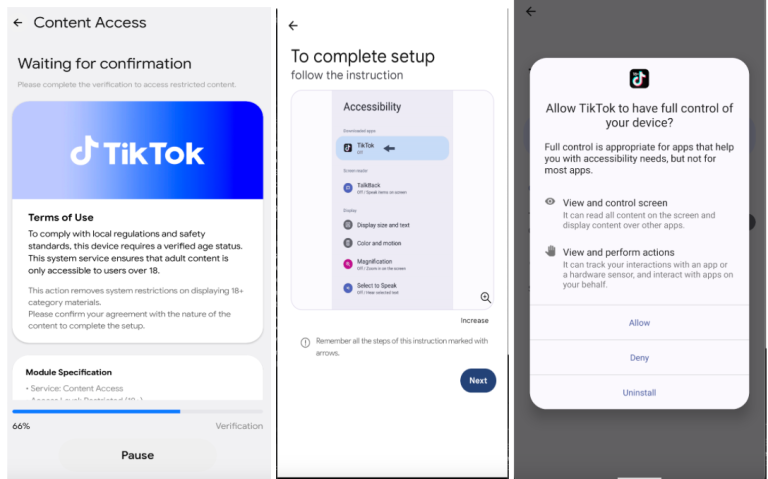
The Rokarolla Android banking trojan executes a complete device takeover. It targets 217 apps and steals credentials through fake overlays and keyloggers.

A new Android banking trojan threat targets 180+ apps. Learn how credential harvesting overlays steal banking data.

A sophisticated Android carrier billing fraud campaign hit users worldwide. Learn how fake apps trigger premium SMS abuse and how to stay safe.
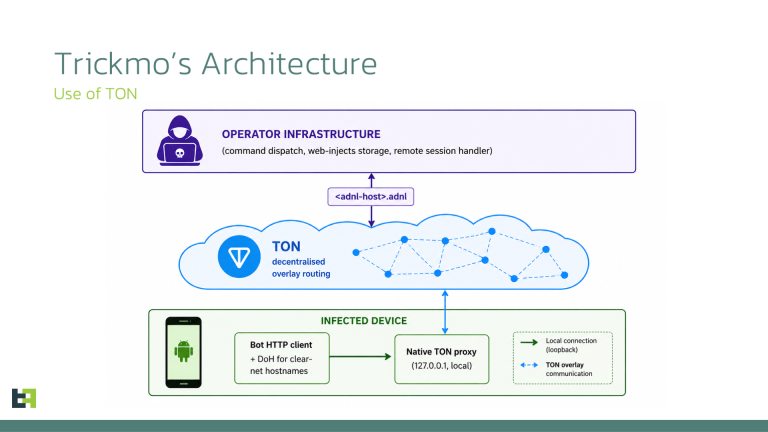
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
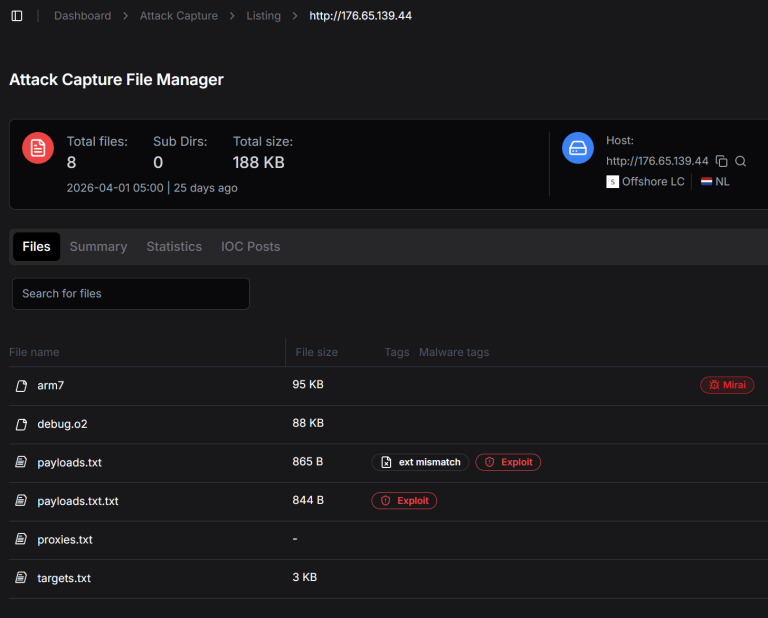
Hunt Intelligence dismantles xlabs_v1, a Mirai-derived botnet targeting 4M Android devices via port 5555. See how an exposed server leaked the entire toolkit.
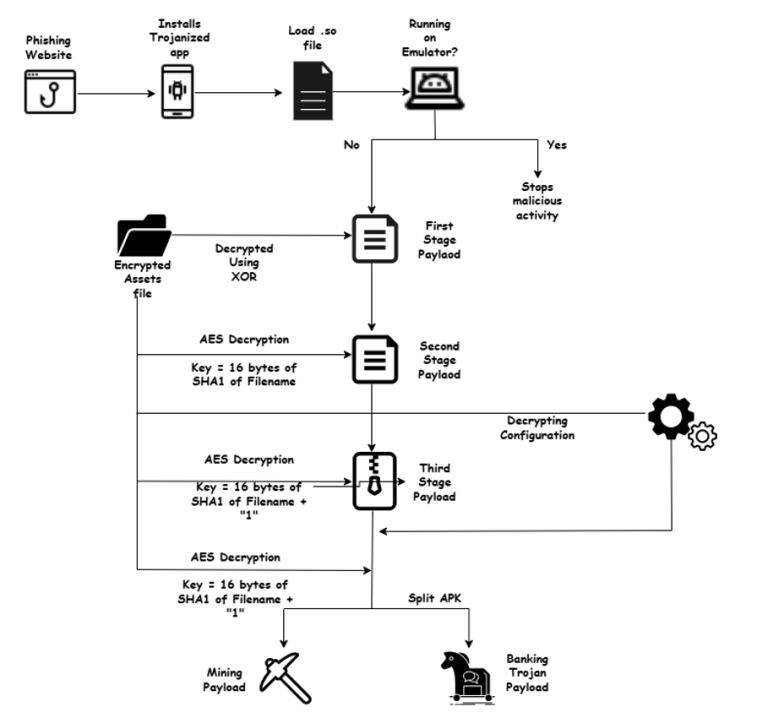
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.

Sophos uncovers Keenadu, a persistent Android firmware backdoor embedded in core libraries that gives attackers total control via the Zygote process.

Discover how Operation False Siren weaponizes Israel's Red Alert app via smishing, deploying advanced Android spyware for geo-fenced mobile espionage.
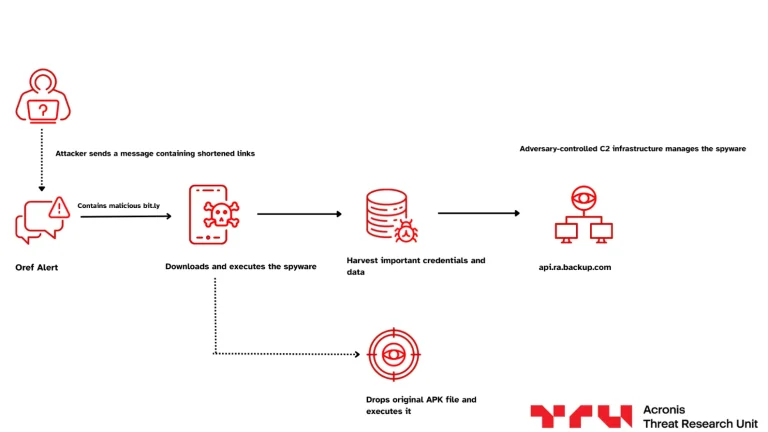
Acronis TRU uncovers a trojanized Red Alert rocket warning app targeting Israelis. Linked to APT-C-23, this Android malware steals data while alerting users.
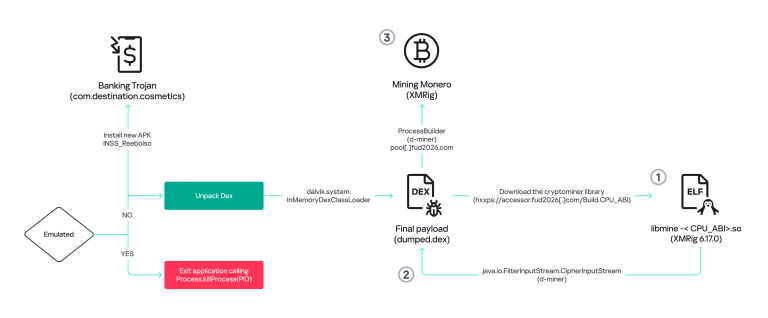
Kaspersky uncovers BeatBanker, an Android malware in Brazil using an audio loop to evade detection while mining crypto and stealing banking credentials.