
 Do Son
The MacSync macOS stealer targets Apple users worldwide. See how MacSync macOS stealer ClickFix lures evade Gatekeeper to steal sensitive credentials.
Apple Security

Full details and PoC exploit code for CVE-2026-39868 are public. The macOS kernel vulnerability in DTrace lets an app corrupt kernel memory. Patch now.

A macOS privilege escalation flaw gives an unprivileged user root with no user interaction. A full public PoC is out; Apple fixed it in 26.6 with no CVE.

Details and PoC exploit code for CVE-2026-39875 are now public. This macOS privilege escalation flaw lets a malicious app gain root. Patch now.
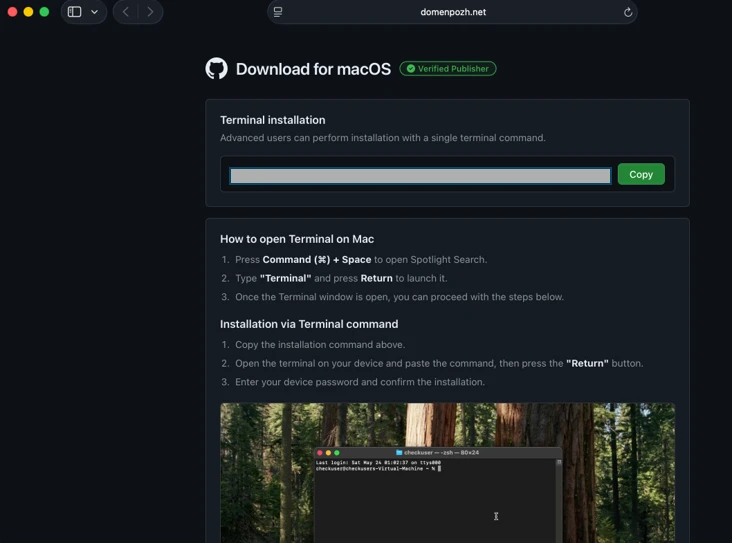
Microsoft reveals a macOS ClickFix campaign using fake "fixes" to trick users into running Terminal commands that bypass Gatekeeper and steal crypto wallets.

AI didn't kill the app—it became the production line. Discover how Vibe Coding fueled a 104% surge in new apps and the security risks facing Apple in 2026.
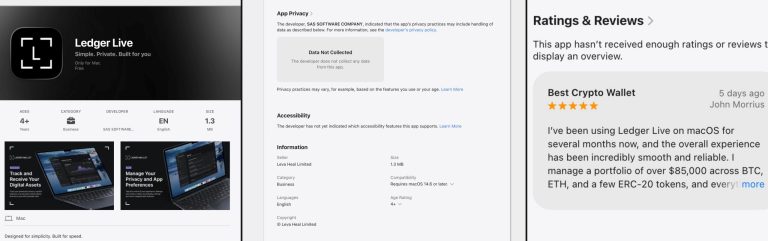
A malicious fake Ledger Live app on the Mac App Store has stolen $9.5M from users. Learn how the scam bypassed Apple's security and why your seed phrase is at risk.

Apple’s macOS Tahoe 26.4 introduces a "Paste Block" to stop terminal-based phishing. Learn how this 2026 security feature thwarts malicious PowerShell scripts.

Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
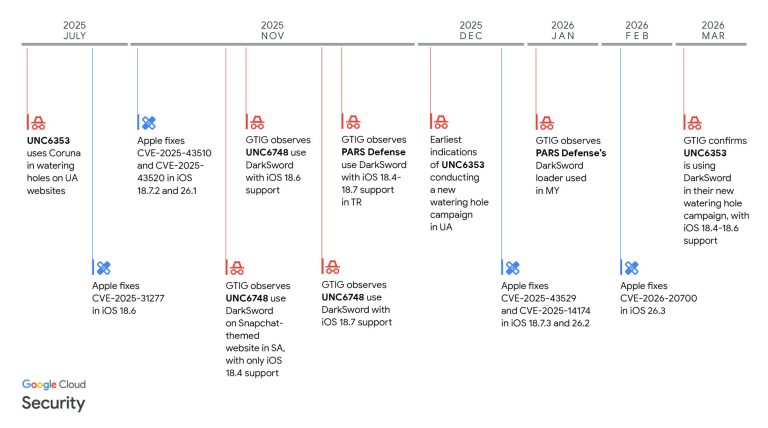
Google uncovers DarkSword, a sophisticated iOS full-chain exploit used globally to deploy spyware via zero-day vulnerabilities. Update to iOS 26.3 now.
CISA adds 5 actively exploited flaws to its KEV catalog, including a critical 10.0 CVSS Craft CMS bug and Apple zero-days linked to DarkSword malware.

PoC exploit code is now public for CVE-2026-20643. Apple issues its first Background Security Improvement to fix this cross-origin Navigation API flaw.
Apple releases emergency iOS 15.8.7 and 16.7.15 updates for older iPhones to block the actively exploited "Coruna" WebKit and Kernel exploit kit. Patch now.

New macOS malware "MonetaStealer" disguises itself as a Windows .exe to steal crypto & Keychain data. It currently has zero VirusTotal detection.

North Korea's "Contagious Interview" campaign uses DriverFixer0428 to steal macOS credentials via fake prompts and Dropbox C2. Stay alert!

PoC for CVE-2023-41992 reveals iOS kernel flaw enabling local privilege escalation. Apple patched it, but risks persist for outdated devices.

PoC exploit for CVE-2025-31258 in macOS RemoteViewServices shows sandbox escape risk. Fixed in Sequoia 15.5. No active exploitation reported yet.

Oligo reveals AirBorne flaws in Apple AirPlay protocol enabling zero-click wormable RCE across billions of Apple, CarPlay, and IoT devices.