
 Do Son
APT28 used the Hookedge backdoor, SSH tunnels, and a new loader to spy on a naval shipbuilder and defense firms in two NATO countries.
APT28
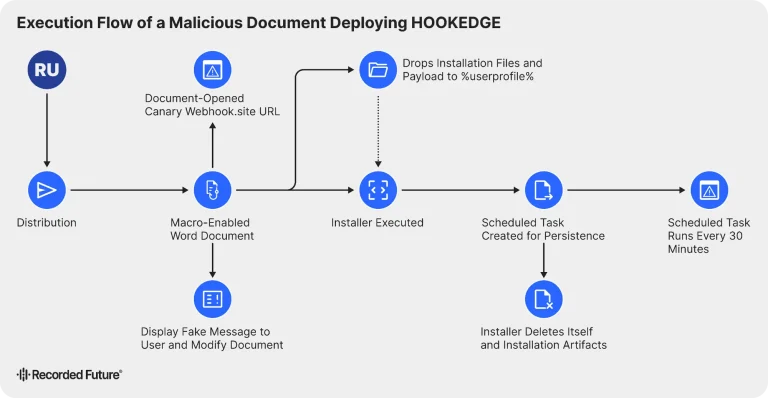
Insikt Group ties HOOKEDGE malware to Russian group BlueDelta (APT28), hitting EU diplomatic targets via webhook abuse and macro-enabled Word lures.
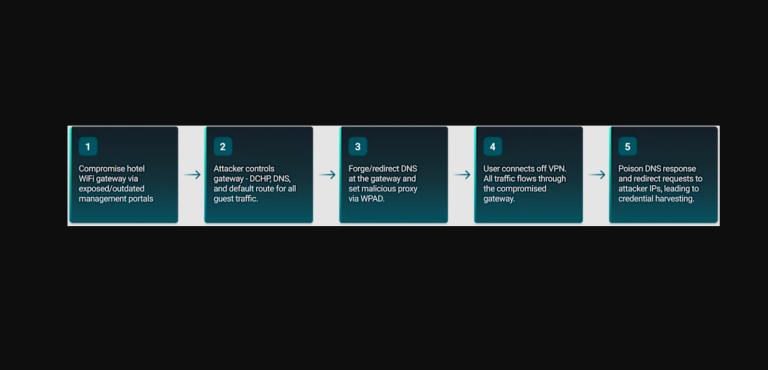
ReliaQuest found hotel Wi-Fi DNS poisoning sending travelers to fake Microsoft 365 pages. Full-tunnel VPN stops the Microsoft 365 account compromise.
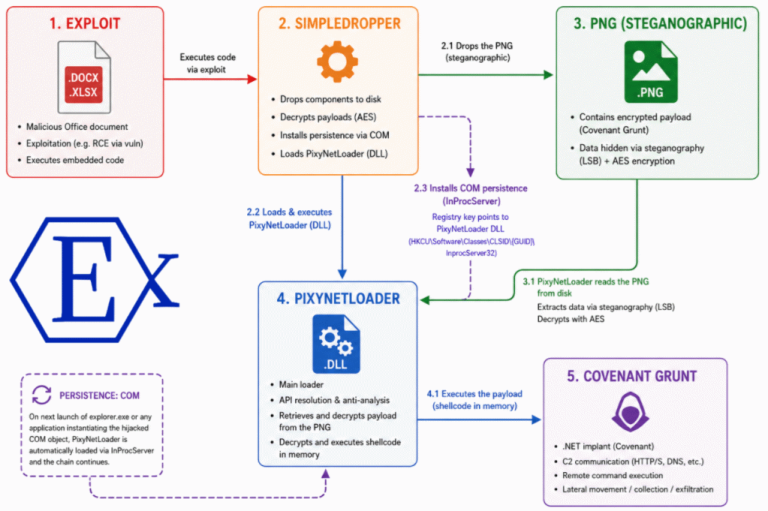
Researchers expose PixyNetLoader malware analysis revealing APT28's steganography APT28 attack, hiding Covenant Grunt payloads inside PNG pixels since 2024.
CISA warns as North Korean and Russian hackers weaponize ConnectWise and Windows Shell flaws. Patch by May 12, 2026, to prevent state-sponsored espionage.
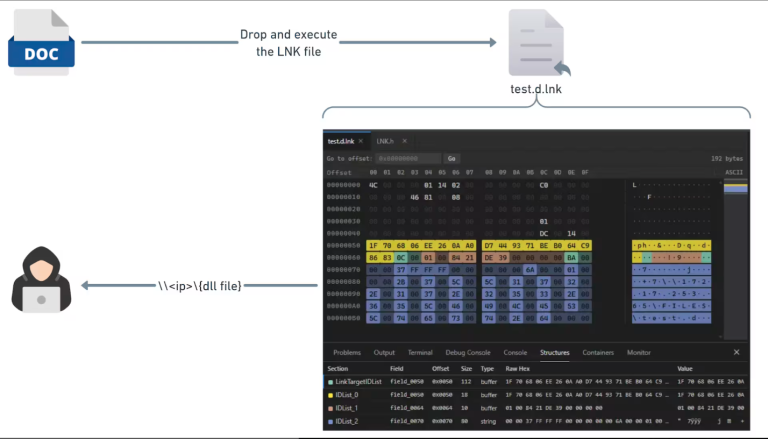
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!

NCSC unmasks APT28’s "digital funnel" using router DNS hijacking to steal OAuth tokens and passwords. Protect your remote workforce—patch your routers now.

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.
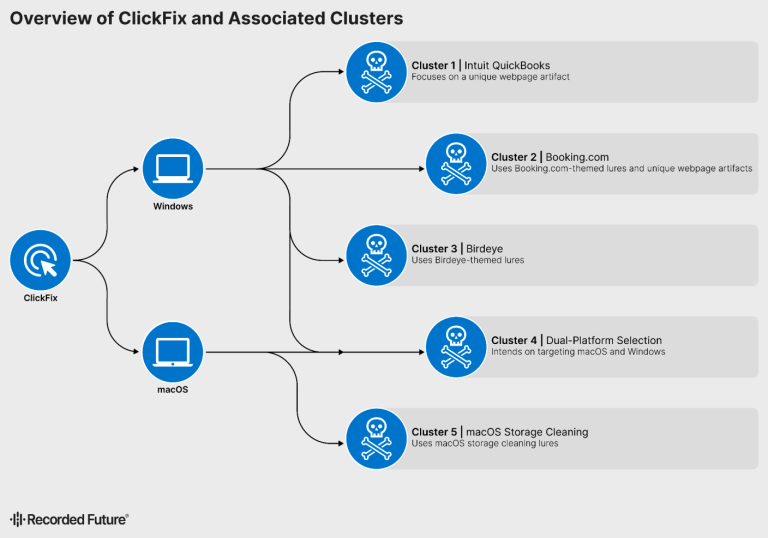
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.
Roundcube v1.6.14 patches a critical pre-authentication file write flaw and account hijacking bugs. Secure your webmail server with this high-priority update.
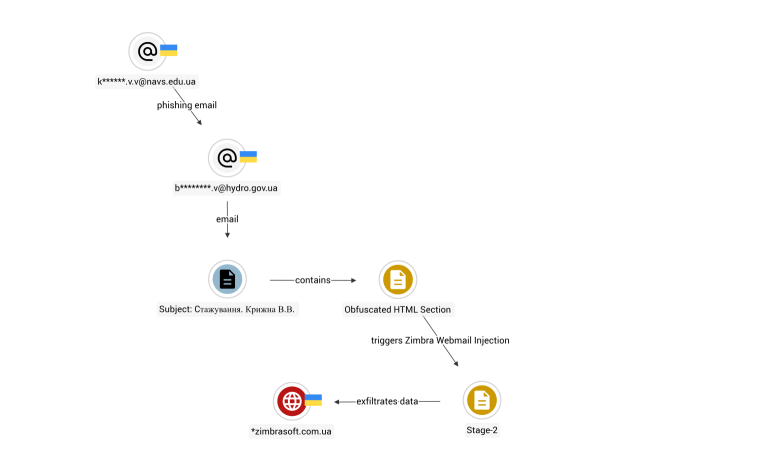
Seqrite Labs uncovers Operation GhostMail, an APT28-linked campaign using a zero-click XSS flaw in Zimbra to silently hijack Ukrainian government webmail.
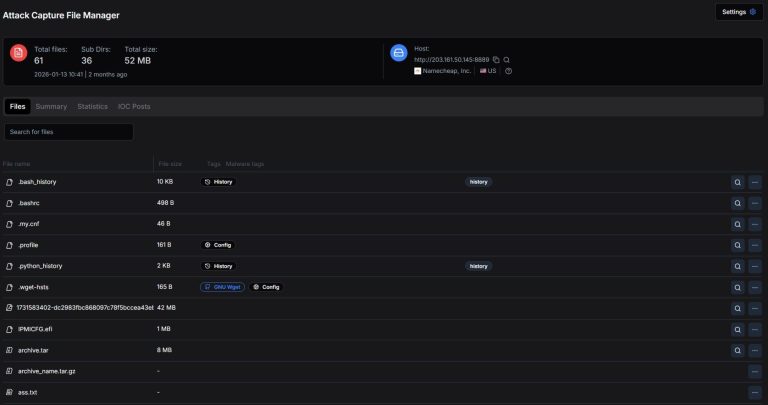
Hunt Intelligence unmasks APT28's 'Roundish' toolkit from an exposed server, revealing advanced CSS side-channel attacks and stealthy Linux implants.
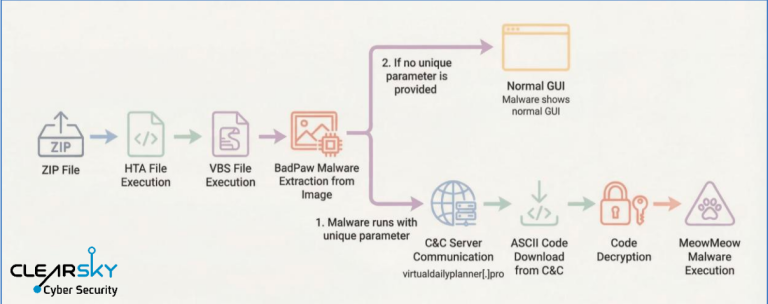
ClearSky uncovers a Russian campaign targeting Ukraine with BadPaw and MeowMeow malware, using steganography and feline decoys for stealthy espionage.
APT28's "Operation MacroMaze" targets Europe using Spanish gov decoys. The campaign uses "low-tech" macros & Webhook.site to evade detection.

APT28 (Fancy Bear) weaponized CVE-2026-21509 in 24 hours to target NATO. New "BeardShell" and "NotDoor" malware steals emails. Patch Office now.
APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.

BlueDelta (APT28) is targeting UKR.NET users with a sophisticated phishing campaign using ngrok and Mocky to bypass security and steal 2FA codes.

Google exposed AI-enabled malware like PROMPTFLUX, which uses the Gemini API to dynamically rewrite its own source code to evade detection. APT28 was seen deploying an LLM-assisted stealer.
A new APT28 campaign targets Ukraine's military with a blend of steganography, open-source tools, and legitimate cloud services for covert C2.

A new report reveals GONEPOSTAL, a backdoor by Russia's APT28 that hides in Outlook macros and uses email itself as a covert command-and-control channel for espionage.

A new report reveals NotDoor, a backdoor by Russia's APT28 that hides in Microsoft Outlook macros and uses specific email triggers to exfiltrate data and execute commands.

Russian-aligned TAG-110 (APT28) is launching a cyber-espionage campaign using macro-enabled Word docs to target Tajikistan's public sector for intelligence.