 Do Son
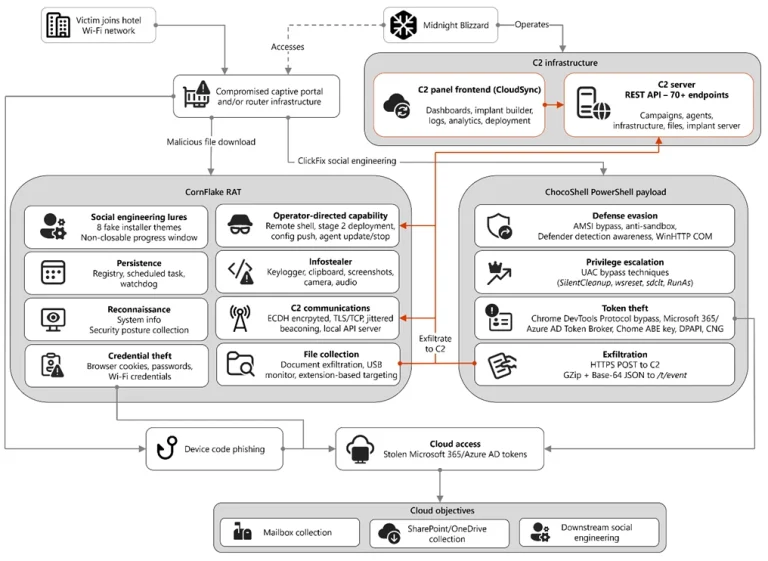
CaptiveCrunch malware campaign hijacks hotel Wi-Fi captive portals worldwide. Microsoft ties Storm-2945 to Midnight Blizzard, Russia SVR-linked group.
APT29

Amazon has disrupted a watering hole campaign by Russia's APT29. The hackers used compromised sites to trick users into authorizing attacker-controlled devices via Microsoft.

A Russian state-sponsored APT, UNC6293 (likely APT29), is exploiting Google Application-Specific Passwords in a sophisticated phishing campaign targeting critics of Russia

APT29, a Russia-linked group, targets European diplomats with phishing emails disguised as wine tasting invitations, deploying GRAPELOADER malware

Explore the risks of Device Code Authentication phishing targeted at Microsoft 365 users by Russian threat actors.
Alarming rise of cyber threats targeting the UK by Russian threat actors. Learn about the dangerous shift in geopolitical tensions and their impact on critical infrastructure.

Beware of the latest RDP phishing attack orchestrated by a Russian state-sponsored threat actor. Learn how to protect yourself from this targeted spear-phishing campaign.

Stay informed and protected from Russian cyber operations with this Joint Cybersecurity Advisory released by the NSA, FBI, CNMF, and NCSC.

Uncover the evolving cyberwarfare tactics of Russian state-backed hackers. Find out how they exploit mobile devices for espionage and data theft.

Discover how cybercriminals exploited Fortinet FortiClient EMS, exposing critical vulnerabilities and utilizing a sophisticated attack chain.

Uncover the series of watering hole attacks on Mongolian government websites and their connection to the Russian government-backed hacking group APT29.

A zero-day vulnerability in Google Chrome (CVE-2024-5274) has been publicly disclosed, along with technical details and a PoC exploit

TeamViewer, a remote control tool trusted by millions of users globally, has disclosed a significant cyberattack.

The Russia-linked Advanced Persistent Threat groups continues to evolve, posing a significant threat to Operational Technology globally

A detailed analysis by the Splunk Threat Research Team reveals a multi-pronged attack and the use of a new backdoor malware called ‘WINELOADER’

The employment of WINELOADER, endowed with features overlapping with other APT29 malware families such as BURNTBATTER and MUSKYBEAT

Masquerading an internal sale of a BMW vehicle, APT29 distributed over 200 emails, embedding the RAR file that served as the Trojan horse

APT29 orchestrated a malicious campaign employing counterfeit BMW advertisements, the Ngrok tool, and exploiting a vulnerability in WinRAR