 Do Son
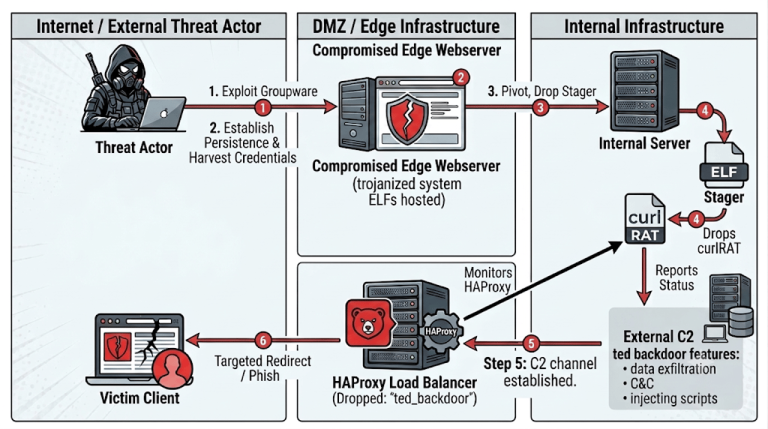
The ted backdoor is DPRK Linux malware hidden inside HAProxy. It pairs with curlRAT to spy on South Korean media and automotive firms, Rapid7 reports.
APT37
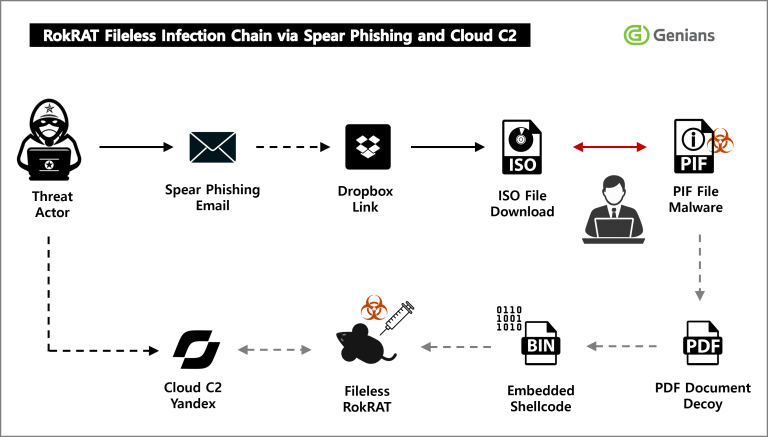
Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.

Discover how APT37 NarwhalRAT malware uses MS-themed phishing and a dead-drop C2 to target users with a sophisticated Python backdoor.
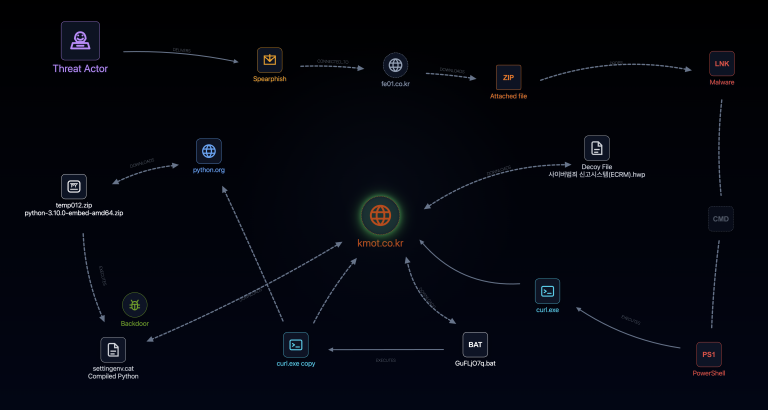
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.
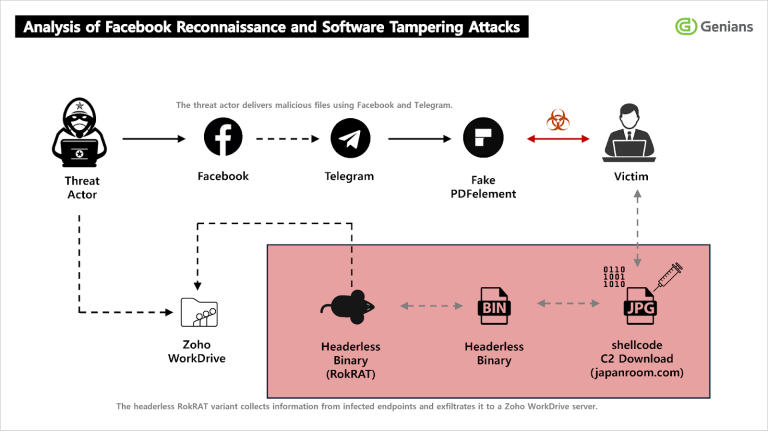
APT37 pivots to Facebook social engineering, using Wondershare PDFelement "code caves" to deploy RokRAT. Learn how they bypass EDR with memory-only payloads.

Zscaler unmasked APT37's "Ruby Jumper" campaign, which uses weaponized USBs and cloud services to bypass network isolation and steal data from air-gapped systems.

Genians exposes APT37's Artemis campaign, where hackers pose as Korean TV writers using fake casting calls to deliver malware via HWP documents.

A new report reveals North Korea's APT37 is using Rust-based malware called Rustonotto, marking a shift toward modern languages and multi-platform attacks.

S2W TALON exposes ScarCruft (APT37), a North Korean APT using a new campaign disguised as a postal notice, deploying NubSpy and VCD ransomware via PubNub C2.

APT37, a North Korea-linked group, is using a new RoKRAT backdoor to target South Korea. The malware uses stealthy LNK files and steganography to evade detection.

New report details APT37's "ToyBox Story" campaign, using spear phishing and cloud services to deploy RoKRAT malware. Fileless attacks and stealthy tactics revealed.
Explore the dangers of Konni RAT, a sophisticated Remote Access Trojan targeting Windows systems with multi-stage attacks.

Uncover insights on KoSpy Android Spyware, a new threat targeting Korean and English-speaking users with deceptive utility apps.

Uncover the Squid Werewolf cyber-espionage campaign and its tactics to exploit fake job offers for cyberattacks.

Learn how APT-C-28 operates in cyber espionage, targeting industries with advanced techniques and the RokRat Trojan.

Explore the impact of South Korean cyberattack threats on civil society organizations and their defenders in a detailed study.

Stay protected from the Operation Code on Toast campaign. Find out about the new zero-day vulnerability CVE-2024-38178 in Microsoft IE and the targeted attack.

Uncover the stealthy SHROUDED#SLEEP malware campaign attributed to North Korea's APT37. Learn how this operation targeting Southeast Asia remains undetected for extended periods.

SentinelLabs unraveled a campaign orchestrated by ScarCruft threat actor targeting media organizations and experts on North Korean affairs

The Konni group leveraged LNK files, essentially commonplace Windows shortcuts increasingly used by various threat actors,
On February 2, 2018, a research team from FireEye, a cyber-security company, published a blog detailing how...