 Do Son
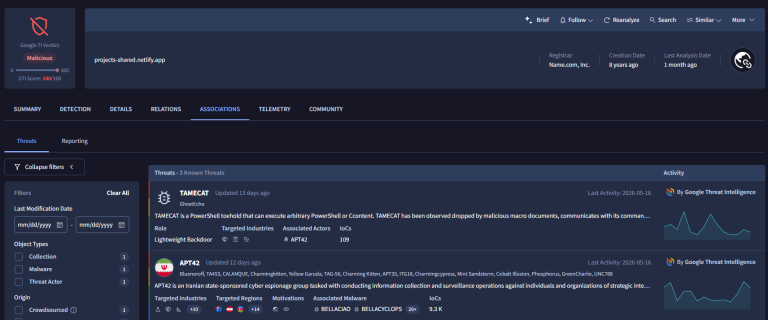
APT42 TAMECAT malware now blends AI-assisted phishing with cloud C2 to steal credentials from defense and nuclear-sector targets.
APT42
Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

Israel disclosed SpearSpecter: an IRGC-IO espionage campaign using weeks-long WhatsApp social engineering and search-ms/WebDAV abuse to deploy the fileless TAMECAT PowerShell backdoor with Discord/Telegram C2.

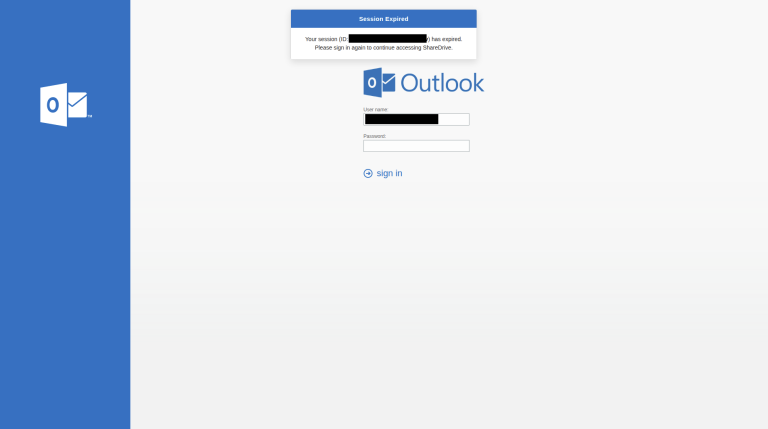
Iranian APT "Educated Manticore" (APT42) uses AI-assisted spear-phishing via email/WhatsApp to target critics with React-based phishing kits, bypassing MFA and stealing credentials.
Discover the attempted hacking of American officials' accounts by hacker group APT42. Meta uncovers the use of sophisticated social engineering tactics.

Find out about APT42's phishing campaigns targeting high-profile individuals and organizations in the U.S. and Israel.

APT42 operations are using two custom backdoors: NICECURL and TAMECAT. These backdoors are delivered via spear phishing

One notable aspect of CharmingCypress's tactics is their use of unusual social-engineering tactics in their phishing campaigns