 Do Son
Attackers are actively exploiting a critical WooCommerce Wholesale Lead Capture vulnerability. Patch WooCommerce Wholesale Lead Capture now.
Arbitrary File Upload
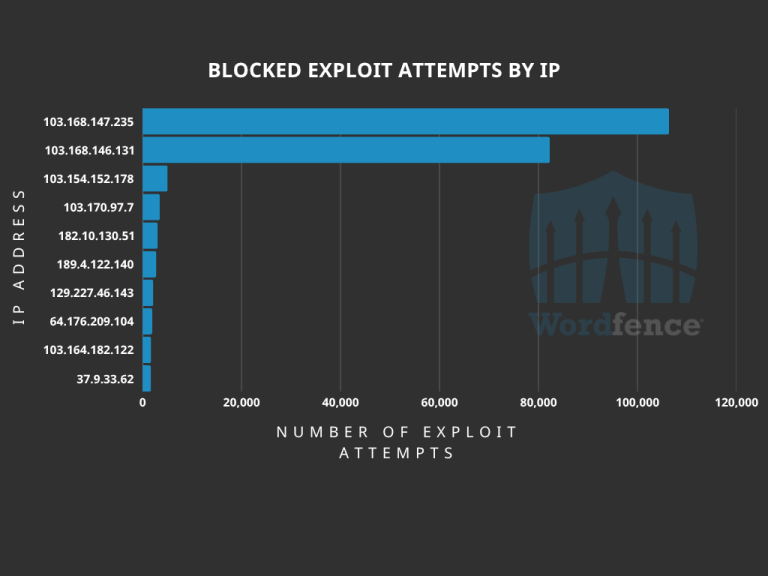
CVE-2026-14894, a critical Super Forms vulnerability, is exploited in the wild. The 9.8 CVSS file upload flaw enables unauthenticated remote code execution.
CVE-2026-32475 (CVSS 9.8) is an Elementor Pro arbitrary file upload flaw risking complete site compromise across 6 million WordPress sites. Update to 4.2.2.
CVE-2026-15748, a CVSS 9.8 flaw in Forminator Forms, lets unauthenticated attackers upload PHP files for pre-auth RCE. Update to 1.56.2 now.
Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!

Critical WPvivid Backup flaw CVE-2026-1357 (CVSS 9.8) allows unauthenticated file upload via null byte key. Update to v0.9.124 to prevent RCE.

Critical RealHomes CRM flaw CVE-2025-67968 (CVSS 9.9) allows any logged-in user to upload malicious files. Update to v1.0.1 immediately to prevent takeover.

A critical RCE flaw (CVE-2025-5394, CVSS 9.8) in the Alone WordPress theme allows unauthenticated attackers to upload arbitrary files and gain full site control. Exploitation is confirmed in the wild.

SonicWall warns of CVE-2025-40599 in SMA 100 series, allowing authenticated admins to upload arbitrary files, potentially leading to RCE.

Cisco addresses CVE-2025-20129 and CVE-2025-20130 in CCP and ISE platforms. PoC exploits are public. Admins urged to migrate to fixed versions.