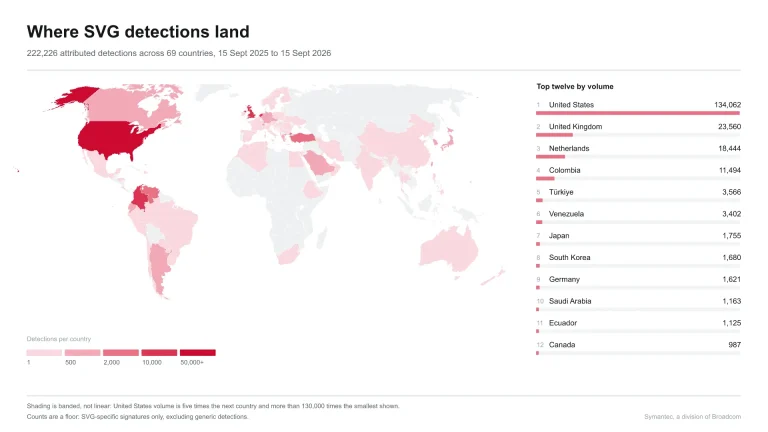
 Do Son
SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.
AsyncRAT
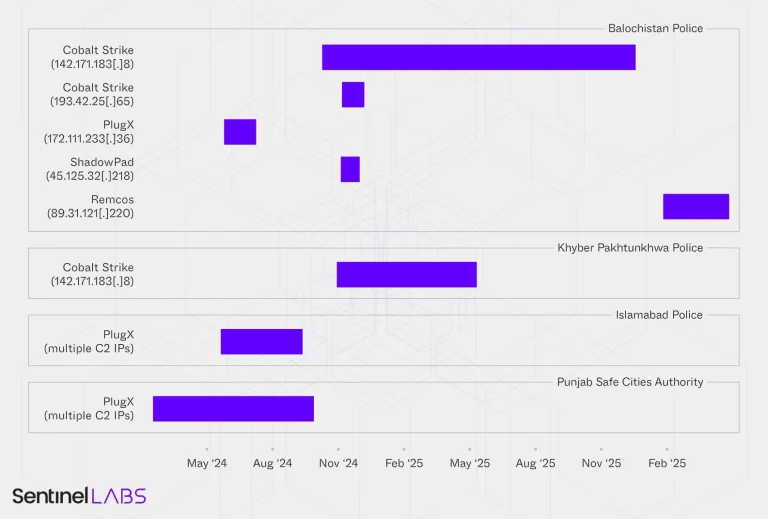
SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.
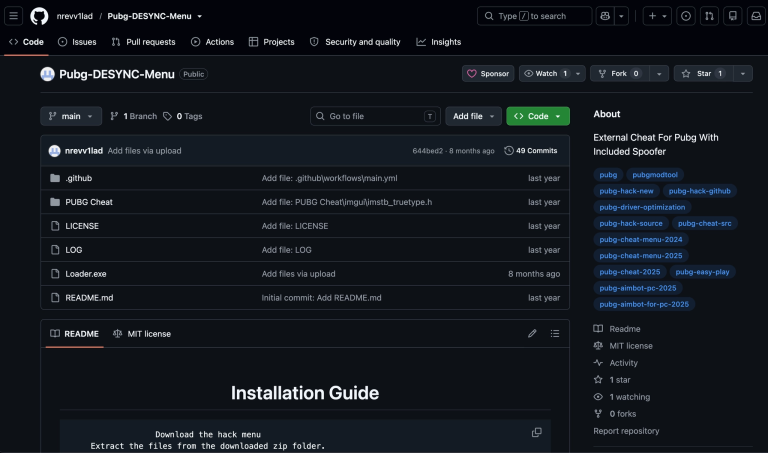
A malicious Go module exposed a GitHub lure network of 222 repositories, dubbed Operation Muck and Load, staging RATs and infostealers.
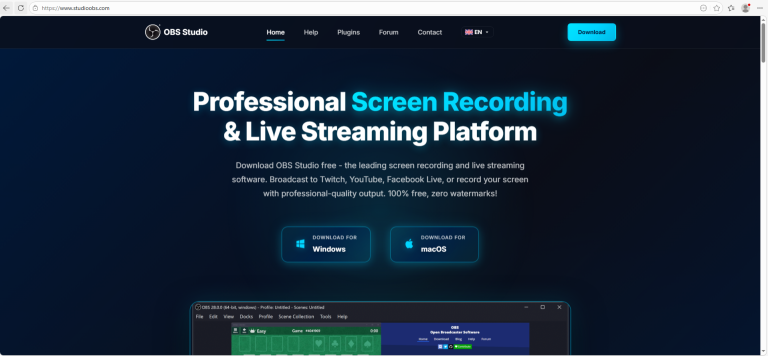
A massive ScreenConnect AsyncRAT campaign uses SEO poisoning and spoofed websites to drop malicious installer archives via remote monitoring tools.

FortiGuard Labs uncovered AsyncRAT AI lures using fake AI guides and an AutoHotkey loader to inject a stealthy .NET RAT into memory.
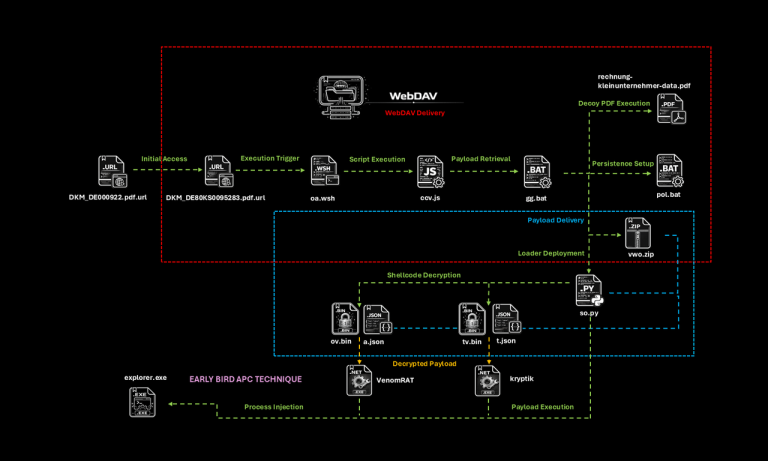
G DATA analysts chat with a malware author via Notepad while analyzing "Kiss Loader," a new threat using Early Bird APC injection and VenomRAT. Read more!

New AsyncRAT campaign abuses free Cloudflare tunnels for stealthy malware delivery. Learn how phishing emails lead to WebDAV attacks & Python injection.

PHALT#BLYX is a malware campaign using fake Booking.com alerts and BSOD screens to trick hotel staff into installing Russian-linked RATs.

Seqrite discovered a campaign using SVG smuggling and a fake Colombian court lure to deploy AsyncRAT. The SVG executes JS to stage a malicious HTA file, evading detection.

A new report reveals attackers are abusing ScreenConnect to deliver AsyncRAT and custom malware payloads, a serious supply chain risk for enterprises and MSPs.

A new campaign is abusing the legitimate RMM tool ScreenConnect to deliver RATs like AsyncRAT and PureHVNC, a trend that is on the rise, targeting US organizations.

Cisco Talos uncovers a sophisticated MaaS operation leveraging public GitHub repos and the Emmenhtal loader to distribute Amadey, SmokeLoader, and AsyncRAT, often via phishing.

Trustwave exposes Blind Eagle (APT-C-36) leveraging exposed infrastructure and VBS malware in phishing campaigns, targeting Colombian banks with blatant disregard for concealment.

Shadow Vector campaign uses malicious SVGs in phishing emails to deliver AsyncRAT & RemcosRAT in Colombia, leveraging advanced DLL sideloading and in-memory execution.

The SERPENTINE#CLOUD campaign exploits Cloudflare Tunnel subdomains and LNK files to deliver in-memory RATs like AsyncRAT and Remcos, evading detection.

A fileless AsyncRAT campaign, dubbed "Clickfix," targets German-speaking users, luring them into executing obfuscated PowerShell payloads via fake verification prompts.

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.
Attackers are hijacking expired Discord invite links, redirecting users to malicious servers that deploy AsyncRAT and crypto-stealing Skuld Stealer via clever social engineering.

A deep dive into a sophisticated multi-stage malware attack using Cloudflare to deliver AsyncRAT. Learn how attackers evade detection and compromise systems.

Uncover the ongoing steganographic campaign that distributes malware like Remcos RAT. Learn how it operates.

Stay informed about Booking Phishing schemes. Discover how attackers use social engineering to steal credentials in this campaign.

Explore how the Blind Eagle group has evolved since 2018, employing advanced tactics like Remote Access Trojans to conduct cyber espionage.