
 Do Son
Uncover the GitVenom campaign targeting GitHub users with malicious repositories designed to steal credentials and cryptocurrency.
AsyncRAT

Uncover how Null-AMSI is used in a malware campaign to bypass Windows security and deploy AsyncRAT effectively.

Discover the latest campaign spreading the AsyncRAT malware. Learn how cybercriminals are utilizing trusted infrastructure to evade detection.

Discover the latest cybersecurity threats during tax season. Find out how cybercriminals are targeting tax agencies and stealing sensitive information.
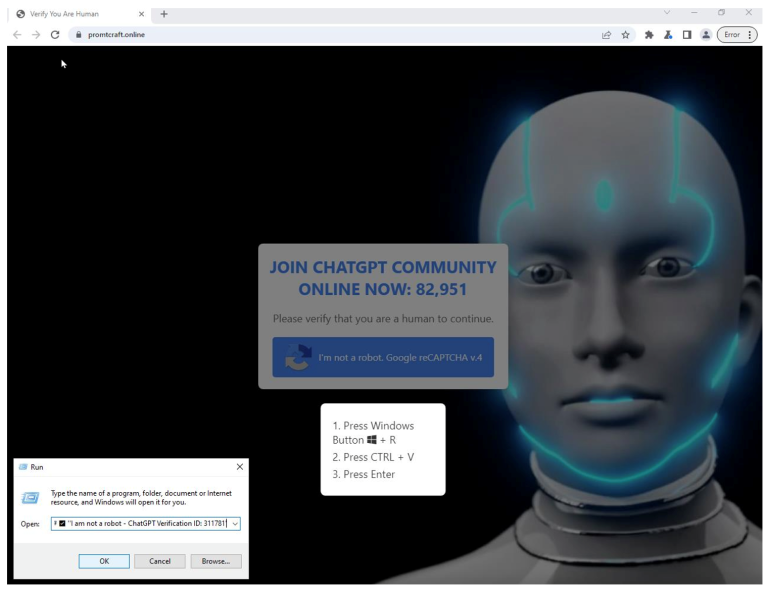
Discover the alarming rise of ClickFix, a unique social engineering method used to spread malware. Learn how it exploits human behavior and how to protect yourself.

Protect your organization from PythonRatLoader: a sophisticated malware loader that distributes harmful remote access trojans (RATs).

Uncover the details of a sophisticated AsyncRAT campaign utilizing Bitbucket. Learn how attackers distributed malicious payloads and evaded detection.

Beware of the evolving threat of AsyncRAT malware disguised as cracked software. Learn how cybercriminals are using this sophisticated remote access trojan to infiltrate systems.
Uncover the details of a sophisticated phishing campaign distributing AsyncRAT and the Infostealer plugin. Learn how cybercriminals bypass security defenses and infiltrate victim systems.

Learn about a recent government cyberattack that used a quartet of malicious software and took advantage of Cloudflare's TryCloudflare service

Huntress has recently uncovered a new wave of malicious activities involving the well-known SocGholish or FakeUpdates malware.

ASEC reveals new cyberattacks utilizing a novel method to distribute the AsyncRAT remote access trojan (RAT)

The campaign utilizes a complex DLL side-loading technique involving legitimate files from the IObit anti-malware solution to execute malicious payloads

AsyncRAT, which stands for Asynchronous Remote Access Trojan, is a sophisticated malware variant meticulously engineered

The recently disclosed vulnerabilities in ScreenConnect (CVE-2024-1709, CVE-2024-1708) necessitate immediate action

ASEC has recently uncovered a cunning method of distribution employed by VenomRAT: a shortcut file (.lnk) disguised as a legitimate Word

AsyncRAT reveals the evolving tactics of adversaries. It exploits aspnet_compiler.exe, intended for precompiling ASP.NET web applications