
 Do Son
AWS unveils Bedrock AgentCore, expands its Generative AI Innovation Center with $100M, and launches an "AI Agents and Tools" Marketplace category to accelerate enterprise AI adoption.
AWS

AWS introduces Kiro, a new AI Agent IDE designed to streamline the entire development lifecycle, from requirements (Specs) to automated quality checks (Hooks), accelerating AI service creation.
AWS replaced its 1-year free tier with a credit-based model (up to $200 credits, 6 months max) for new users, effective July 15, 2025. Accounts close if not upgraded.

JPCERT/CC warns of critical flaws in Nimesa Backup and Recovery (CVE-2025-48501, CVSS 9.8 RCE; CVE-2025-53473 SSRF). Unsupported versions pose severe risk to AWS data.

Trellix uncovers "OneClik," a sophisticated APT campaign abusing Microsoft ClickOnce and AWS cloud services to deploy Go-language backdoors, targeting energy, oil, and gas sectors.

Taiwan's BitoPro exchange confirms North Korea's Lazarus Group stole $11.5M in crypto via phishing an employee and bypassing MFA on AWS infrastructure.
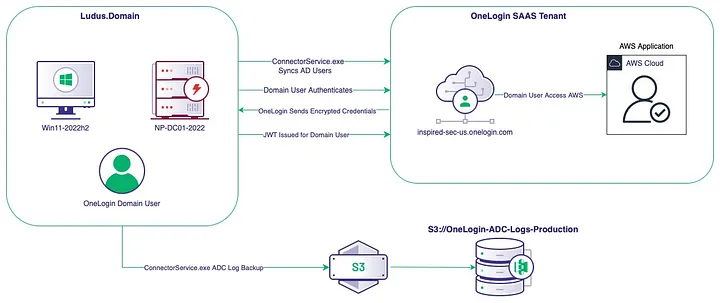
A critical flaw in OneLogin's AD Connector exposed API keys, allowing attackers to impersonate users across organizations via unclaimed S3 buckets and forged JWT tokens.

TeamFiltration is being actively exploited in UNK_SneakyStrike, targeting over 80,000 Microsoft Entra ID accounts with password spraying and data exfiltration.
Amazon is investing $10B in North Carolina for AI infrastructure, creating 500+ high-skilled jobs and boosting the local economy and STEM education.
CVSS 9.9 flaw in Cisco ISE cloud deployments with public PoC exploit enables remote attacks on AWS, Azure, and OCI. Patch now.
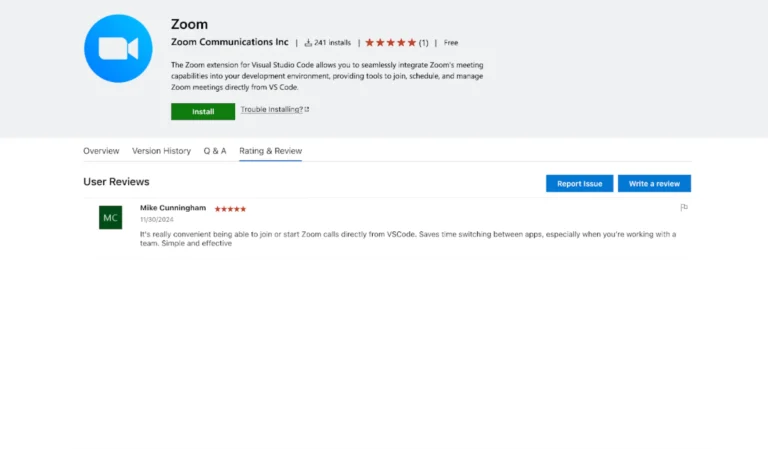
Beware of a malicious VS Code extension impersonating the Zoom Workspace tool. Learn how this deceptive extension targets software developers and steals sensitive data.

Discover Google's vision for 2025: leveraging advanced AI technology to shape the future of innovation and consumer applications.

Learn about ALBeast, a critical vulnerability affecting AWS Application Load Balancers (ALBs). Discover how this flaw can lead to unauthorized access and data breaches.

Learn about a massive ransomware campaign targeting over 100,000 domains. Understand the user errors in cloud services that enabled the attack and the impact on data security.

Learn about the dangerous vulnerability present in Google Pixel devices that allows cybercriminals to execute code at the system level.

One of the most concerning discoveries in this campaign is the deployment of a new Java-based RAT named VCURMS.