 Do Son
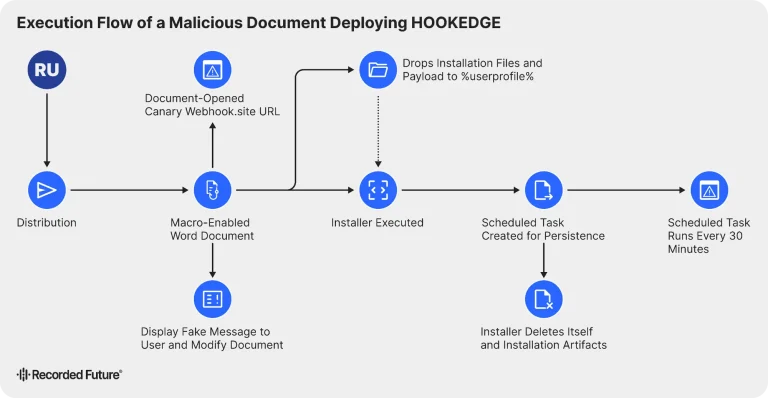
Insikt Group ties HOOKEDGE malware to Russian group BlueDelta (APT28), hitting EU diplomatic targets via webhook abuse and macro-enabled Word lures.
BlueDelta
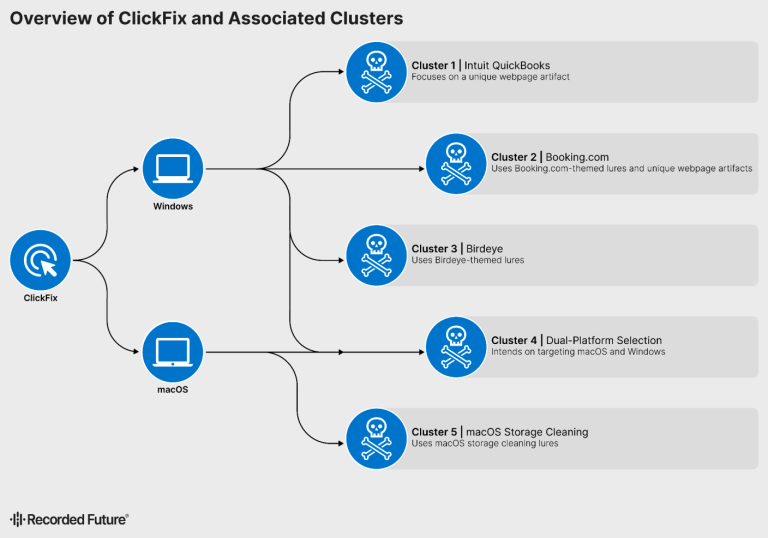
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.

Russian group BlueDelta targets energy researchers in Europe & Middle East. Learn how they abuse free web services for credential harvesting.

BlueDelta (APT28) is targeting UKR.NET users with a sophisticated phishing campaign using ngrok and Mocky to bypass security and steal 2FA codes.

Stay informed about the latest cyber-espionage threat actor, UAC-0063. Learn about their activities in Central Asia and Europe and the cybersecurity concerns they raise.

Uncover the cyberespionage campaign attributed to TAG-110. Learn about the Russia-aligned threat group targeting organizations and their motives.