 Do Son
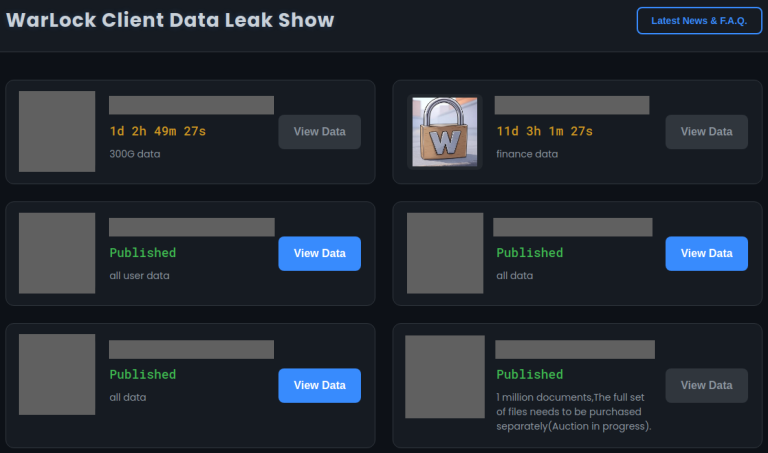
The Warlock ransomware group still exploits SharePoint vulnerabilities, hitting a water utility, a telecom firm, and more. Here is how to defend.
BYOVD
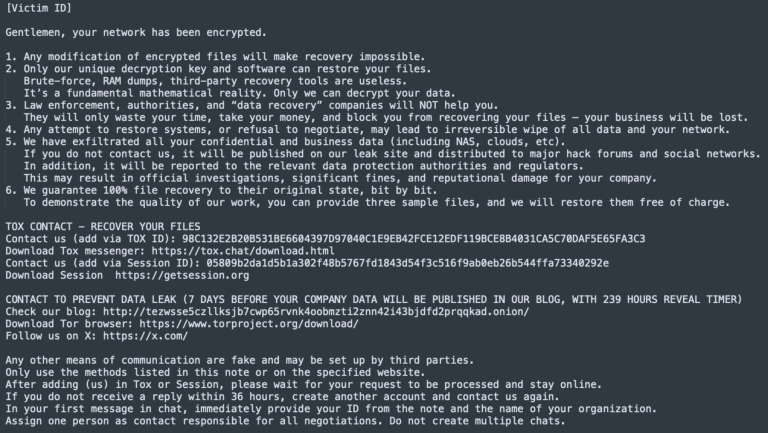
The Gentlemen ransomware, run by GOLD SHERWOOD, encrypts networks in under 24 hours. See the affiliate playbook and how to defend against it.
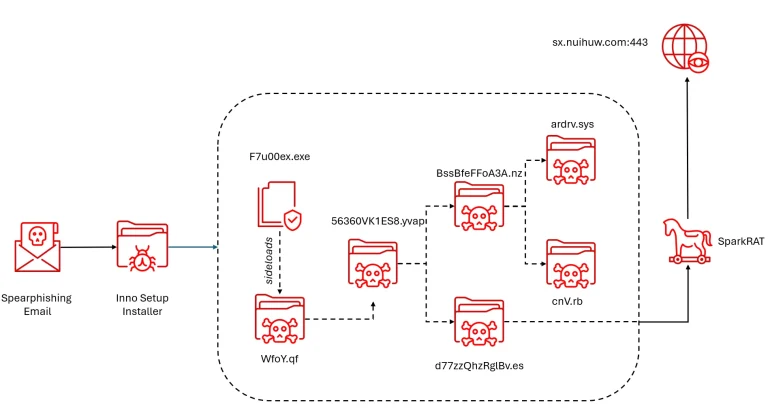
A Cambodia malware campaign hides SparkRAT in PNG files and abuses a vulnerable driver to kill antivirus, Acronis TRU reports.
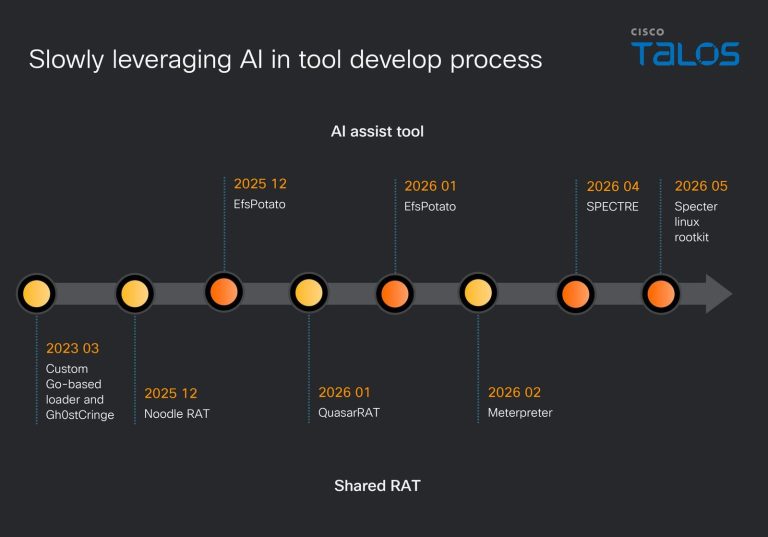
Cisco Talos reveals that Chinese-speaking threat group UAT-10147 deploys the SPECTRE cross-platform implant with Linux rootkits and BYOVD capabilities.
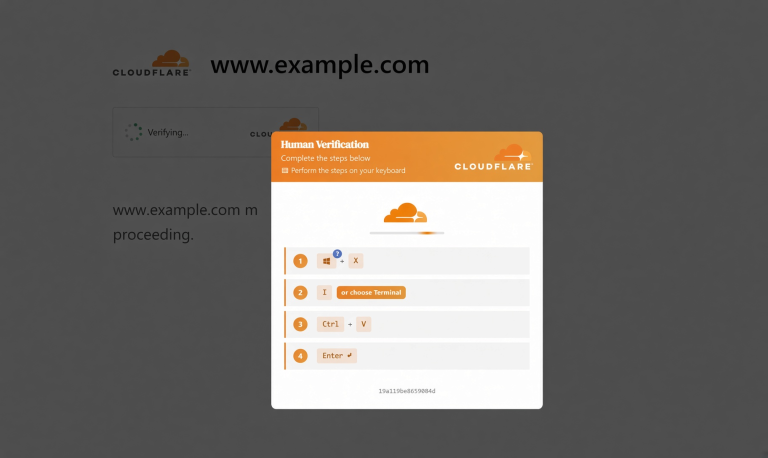
eSentire ties the Cruciferra malware loader to ClickFix EDR killer attacks that abuse a signed driver to stop 145 security processes.
Check Point details BTR.sys driver abuse: a signed Defender component turned into a kernel EDR/AV bypass with no exploit needed.

Cato CTRL details a new SilverFox ValleyRAT campaign in Japan using three BYOVD drivers and DLL sideloading to kill security tools.

Proofpoint details the Cruciferra crypter service that cloaks RATs and infostealers using BYOVD EDR tampering and 90+ custom encryption routines.

GodDamn ransomware is the latest Beast ransomware rebrand from Hyadina. It uses a Microsoft-signed malicious kernel driver, PoisonX, to disable EDR.

Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
ESET found vendor-signed UEFI applications vulnerable to a Secure Boot bypass. Attackers can run pre-boot code. Update firmware and the UEFI DBX now.
DragonForce ransomware deployed Backdoor.Turn, a Microsoft Teams backdoor that hides C2 in Teams TURN relays. Symantec details the novel technique.

Trend Micro reveals Warlock ransomware is using kernel-level BYOVD attacks and abused IT tools to bypass security and hijack Active Directory.
Aryaka Threat Labs exposes BlackSanta, a Russian-linked malware targeting HR teams with fake resumes to deploy an EDR-killer and steal crypto wallets.

Black Basta ransomware now embeds a vulnerable NsecSoft driver (BYOVD) to silently kill antivirus processes like Sophos & CrowdStrike.

Interlock ransomware exploits a zero-day in gaming anti-cheat drivers to blind defenses. "Hotta Killer" tool targets education sector. Read the analysis.

New Osiris ransomware hits Southeast Asia, linking to Inc & Medusa groups. It uses BYOVD tactics to disable defenses. Unrelated to the 2016 variant.

Huntress exposes "VSOCKpuppet" VM escape: Attackers used a hidden zero-day toolkit to breach VMware ESXi hosts and bypass network monitoring.

The Gentlemen ransomware group rapidly emerged, targeting 17 countries with double extortion. It uses BYOVD and GPO manipulation to bypass security and hit manufacturing, healthcare, and insurance sectors.

GOLD BLADE (RedCurl) targets Canadian firms (80% of attacks) with espionage and QWCrypt ransomware. The group uses fake resumes and a BYOVD EDR killer (Zemana driver) to disable security controls.

Makop ransomware operators now use GuLoader and BYOVD (ThrottleStop.sys) to bypass EDR and security. The "low-effort" campaign targets RDP-exposed networks, with 55% of attacks aimed at India.

DeadLock Ransomware uses BYOVD (Baidu driver exploit) and the EDRGay.exe loader to kill EDR/AV at the kernel level. It uses a custom stream cipher and deletes shadow copies to prevent recovery.