 Do Son
Check Point Research reveals VECT 2.0 ransomware is a broken wiper. A critical flaw makes file recovery impossible for files over 128KB. Read the analysis.
ChaCha20
Morphisec uncovers Pay2Key’s Linux evolution. This dual-arch ransomware disables SELinux and AppArmor to encrypt x64/ARM64 servers. Secure your infra today!
ASEC exposed Yurei, a new Go-based ransomware group using ChaCha20-Poly1305/ECIES for irreversible encryption. The stealthy RaaS operates with minimal initial setup and focuses on double extortion.

ENKI exposed a Lazarus Group espionage campaign targeting aerospace/defense firms. The new Comebacker variant uses malicious Word macros and ChaCha20/AES to deliver a memory-resident backdoor.

A Babuk successor, Midnight ransomware, contains a critical flaw in its RSA key handling. Gen researchers created a free decryptor that bypasses the encryption, allowing victims to recover files.

ASEC exposed a flaw in Gunra Linux ransomware: its ChaCha20 keys are generated using an insecure time()/rand() seed, potentially allowing victims to brute-force decryption and recover files.

AhnLab exposed Beast ransomware (Monster evolution) as a new RaaS threat, with 16+ victims by August 2025. It uses ChaCha20 encryption, deletes Shadow Copies, and features a hidden GUI control panel.

ThreatLabz reveals the evolution of Raspberry Robin malware, now featuring stronger encryption, complex obfuscation, and a new privilege escalation exploit to bypass detection.

Gen Digital has released a free decryptor for FunkSec ransomware, allowing victims to recover files. The group appears dormant, with no new victims since March 2025.

Learn about the recent spike in botnet activity from FICORA and CAPSAICIN targeting D-Link devices and the vulnerabilities they exploit.

Discover the dangerous Hail Cock botnet and its target: the vulnerable DigiEver DS-2105 Pro DVRs. Learn how to safeguard your devices.

CRIL published a detailed analysis of a newly identified ransomware variant named Trinity, highlighting its potential links to Venus ransomware
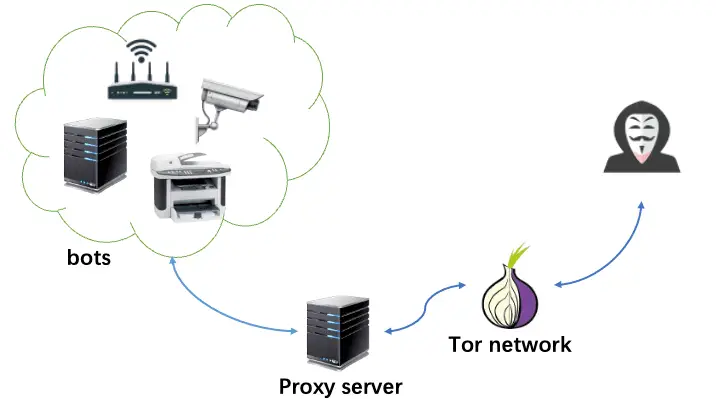
Rimasuta botnet is designed to infiltrate systems and evade detection. It employs advanced data encryption and communication techniques